amex-mitgliederpramieneinlosen241.ink
Appeared in the .ink zone on Thursday, September 17, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
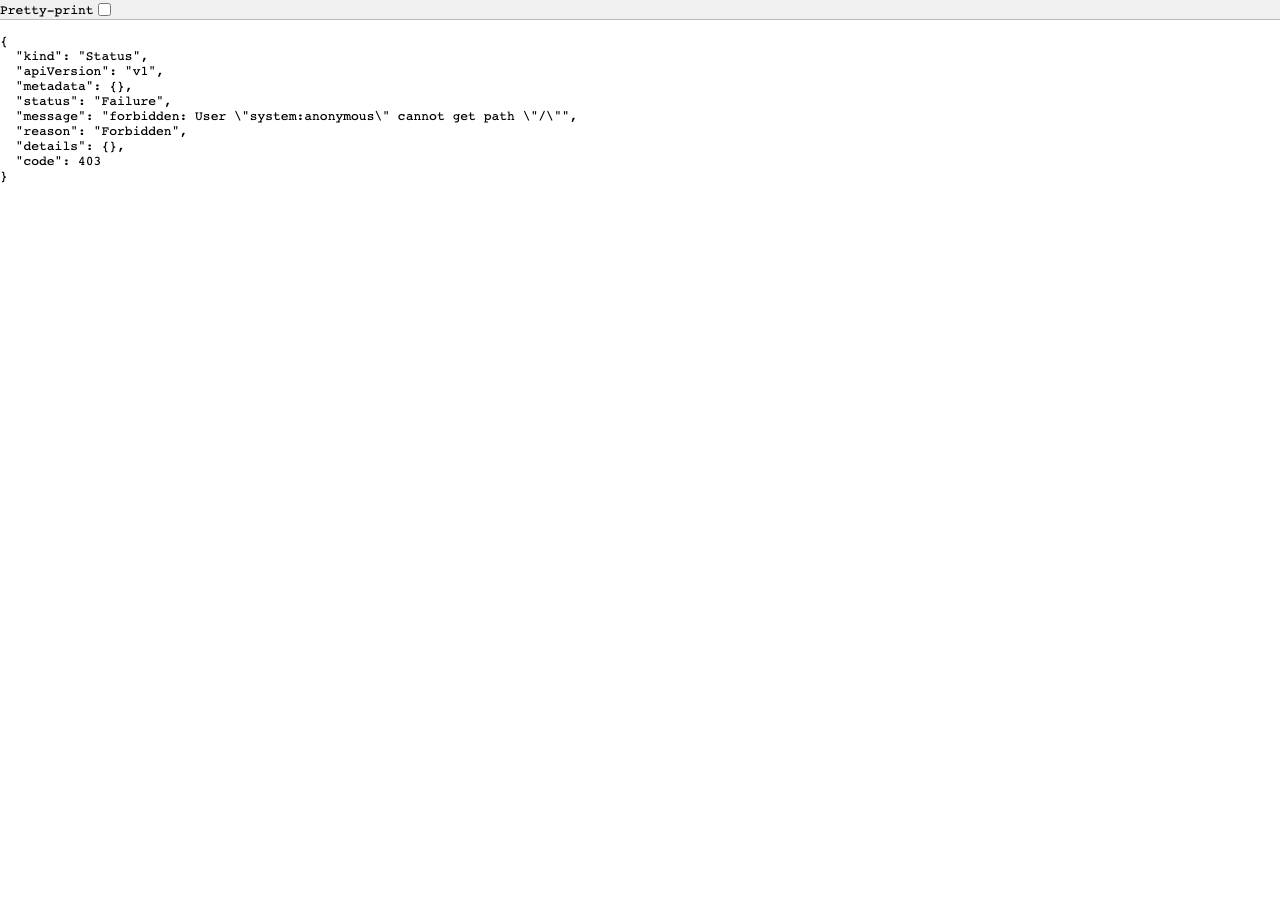
Domain spells out a German Amex lure phrase ('Mitglieder Prämien einlösen' = redeem member rewards) plus campaign digits '241', registered through a cheap HK retail registrar on Alibaba DNS — the classic Amex rewards-redemption credential phish naming pattern; the host currently returns only a Kubernetes API 403 JSON page, i.e. staged infrastructure with content not yet deployed.
typesafe first pass (gate 0.4): p=abuse:0.52 suspicious:0.36 phishing:0.10 | impersonates=0.82 credential=0.18 parked=0.78 evidence=1.0 | target=amex:1.00
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, September 17, 2026
Same data as JSON: /api/zone/domain/amex-mitgliederpramieneinlosen241.ink. This page is not indexed by search engines and does not link to the site it describes.