amex-punktegegenpramieneinlosen326.ink
Appeared in the .ink zone on Thursday, September 17, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
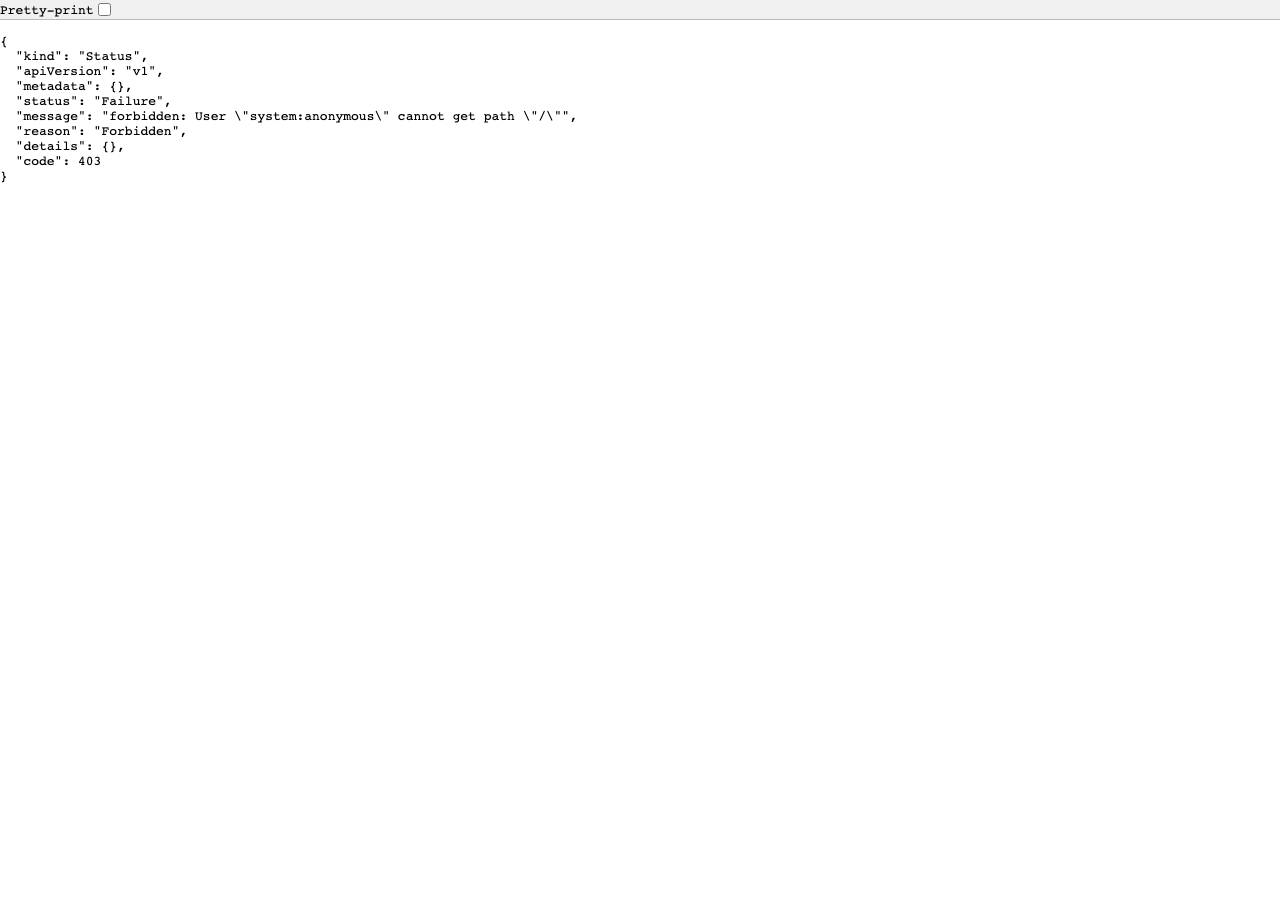
Domain name impersonates American Express (amex) combined with German text 'punktegegenpramieneinlosen' (points-for-rewards redemption), suggesting a phishing lure targeting German-speaking Amex customers. However, the site currently returns HTTP 403 with a generic API error message rather than a functional phishing page, making it either incomplete infrastructure or a blocked/suspended phishing attempt.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, September 17, 2026
Same data as JSON: /api/zone/domain/amex-punktegegenpramieneinlosen326.ink. This page is not indexed by search engines and does not link to the site it describes.