ams-off.top
Appeared in the .top zone on Saturday, October 3, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
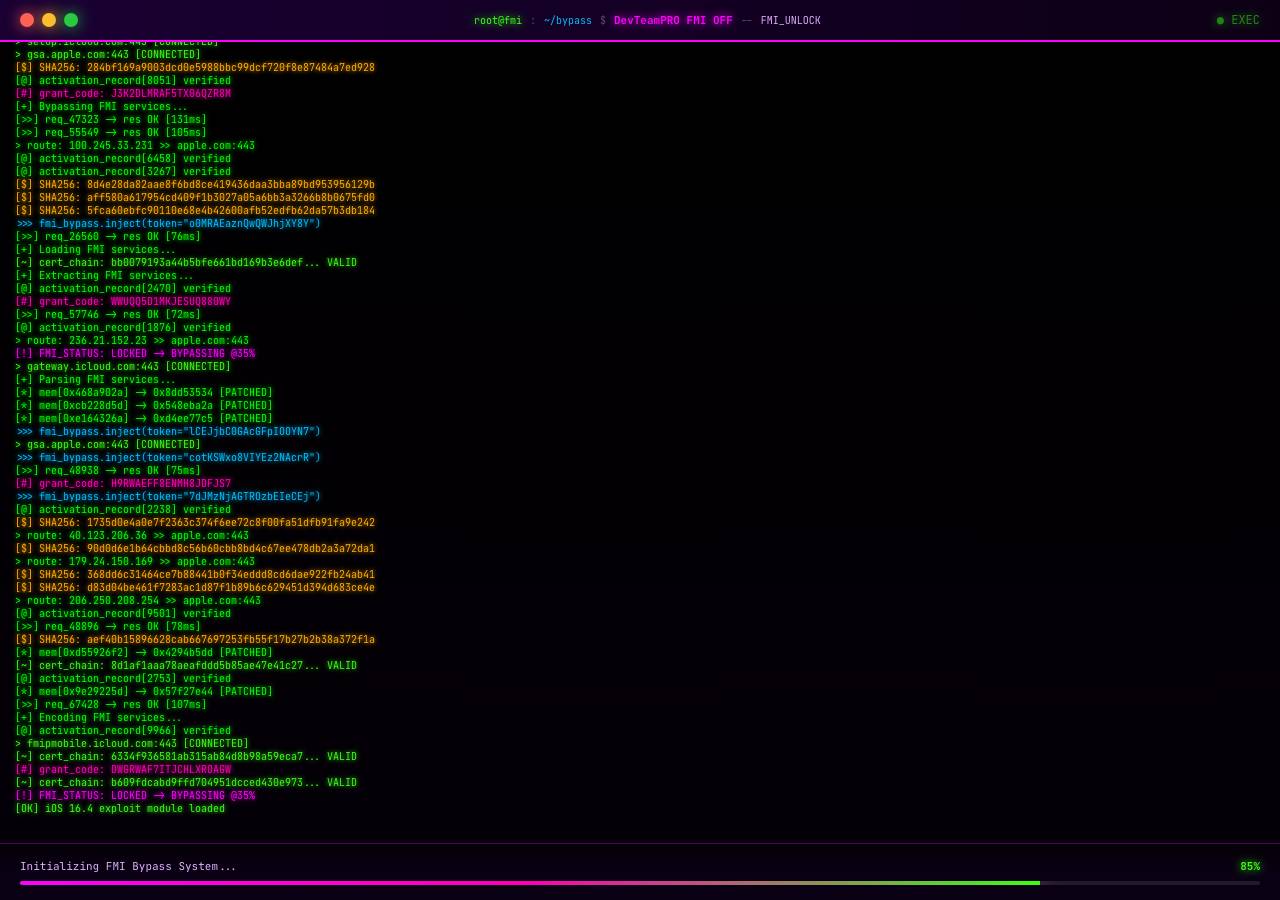
The domain redirects to an FMI/iCloud activation-lock 'bypass' service (DevTeamPRO FMI OFF, iLuminaT1sCode) that sells circumvention of Apple's Find My iPhone lock — a service to unlock stolen/locked devices, with Telegram/WhatsApp operator contacts and a code-submission form; this is illicit device-unlock abuse rather than credential phishing of Apple.
The domain ams-off.top redirects to a fake Apple iCloud FMI (Find My iPhone) bypass service. The destination page impersonates Apple's branding and FMI unlock process, presenting a fake 6-digit code entry form with Apple-themed UI ('DevTeamPRO FMI OFF', 'Desbloqueo iCloud Profesional') designed to deceive users into believing they are interacting with a legitimate Apple service. The form posts credentials to the attacker's infrastructure, and operator contact is via Telegram/WhatsApp, confirming
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, October 3, 2026
Same data as JSON: /api/zone/domain/ams-off.top. This page is not indexed by search engines and does not link to the site it describes.