apple-dns.top
Appeared in the .top zone on Thursday, October 1, 2026; by the end of that day the census found parked, for sale. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
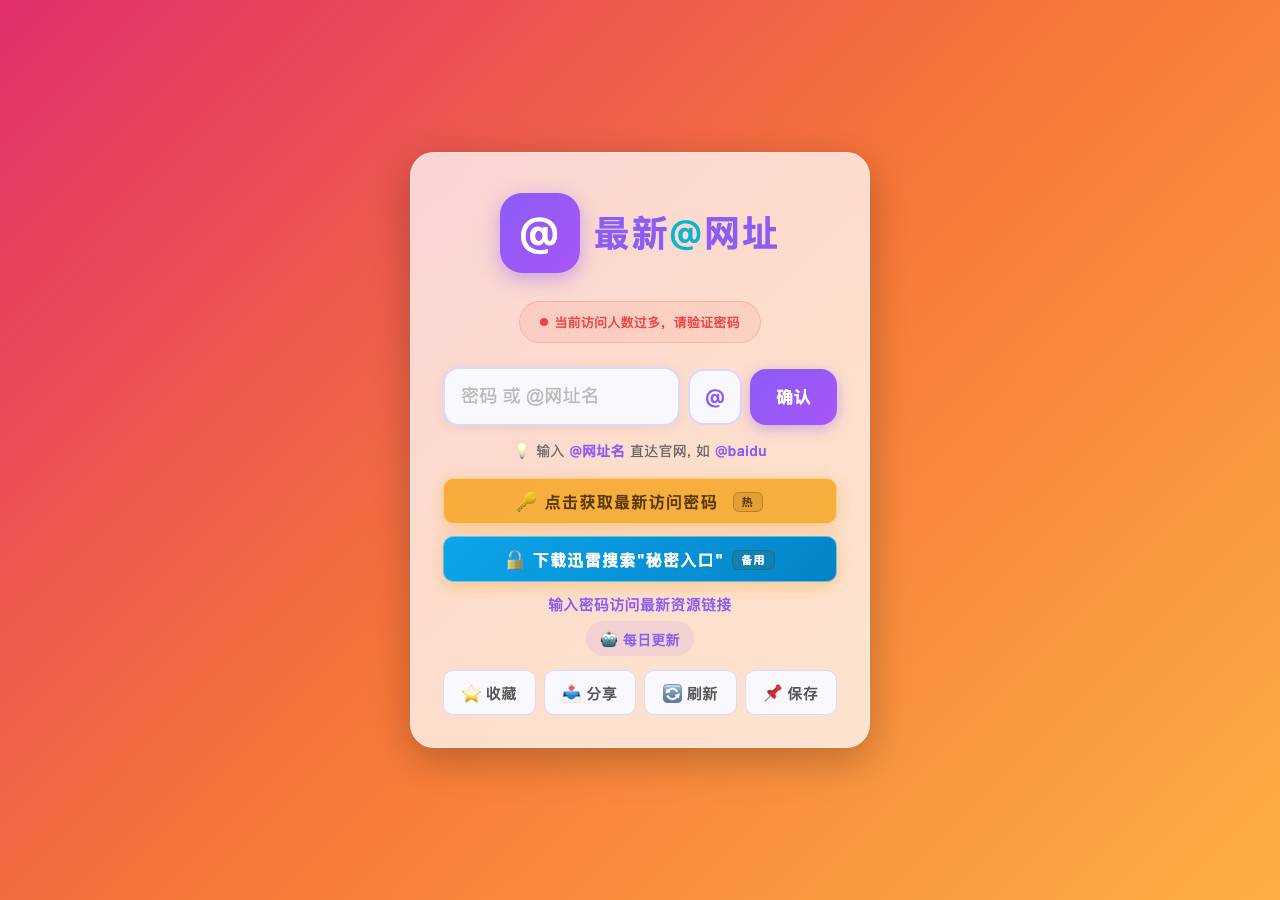
The name is built on the distinctive brand 'apple' (plus 'dns'), and the site redirects to a urldance.com page titled '最新@网址' ('latest URL'). That page is a password-gated link hub that pushes Xunlei downloads and 'secret entrance' searches, the usual funnel for adult, piracy or gambling content. It is shared across a 172-page cluster, so this is a brand-squat traffic funnel, not an Apple credential phish.
apple-dns.top is a brand-typosquat domain (Apple + DNS infrastructure word) registered at Dynadot and redirecting to a password-gated scam portal (urldance.com). The destination serves Chinese-language content prompting password entry to access 'latest resources,' with references to Xunlei (piracy tool) and claims of daily updates—a classic piracy/warez front. The 172-domain cluster with identical pages and redirect infrastructure indicates an organized typosquat abuse campaign, not phishing of
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 1, 2026
Same data as JSON: /api/zone/domain/apple-dns.top. This page is not indexed by search engines and does not link to the site it describes.