asset-content-delivery.shop
Appeared in the .shop zone on Tuesday, November 10, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
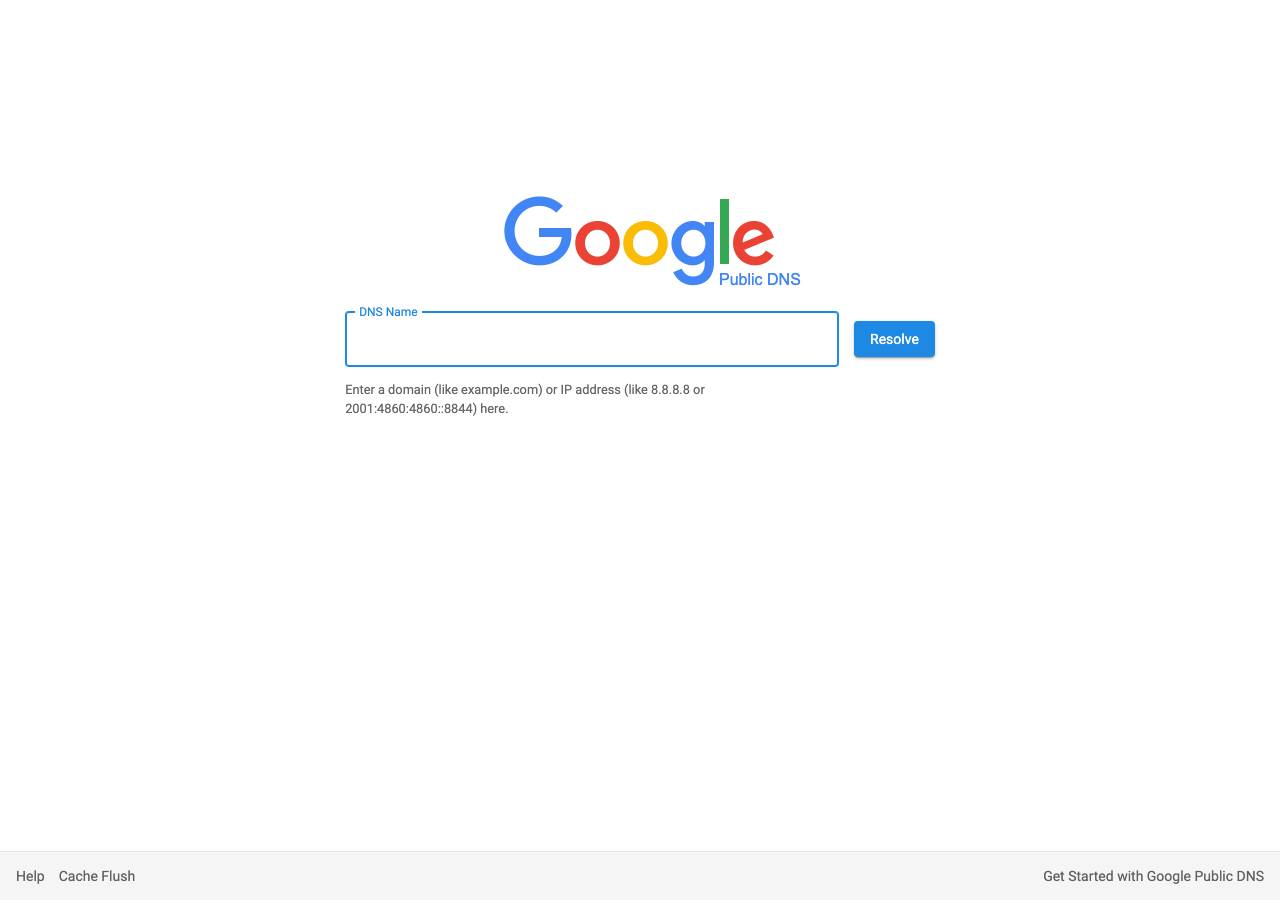
The domain serves no content of its own and redirects to the real dns.google, so the Google branding and DNS lookup form are the destination's, not impersonation. Still, a fresh, generic CDN-mimicking name ('asset-content-delivery') on .shop behind Cloudflare that bounces visitors to a neutral decoy fits how malware-staging or C2 domains are often cloaked, but the evidence is not decisive.
The domain asset-content-delivery.shop is a typosquat registered to redirect visitors to Google's legitimate dns.google site, creating a deceptive entry point. The attacker controls a misleading domain name ('asset-content-delivery') combined with a generic TLD that does not belong to Google, establishing false trust before redirecting to the real Google page—a classic phishing technique to harvest credentials or data during the redirect handoff or through URL manipulation.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, November 10, 2026
Same data as JSON: /api/zone/domain/asset-content-delivery.shop. This page is not indexed by search engines and does not link to the site it describes.