baiyangxi.lol
Appeared in the .lol zone on Saturday, September 26, 2026; by the end of that day the census found active website about ai software. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
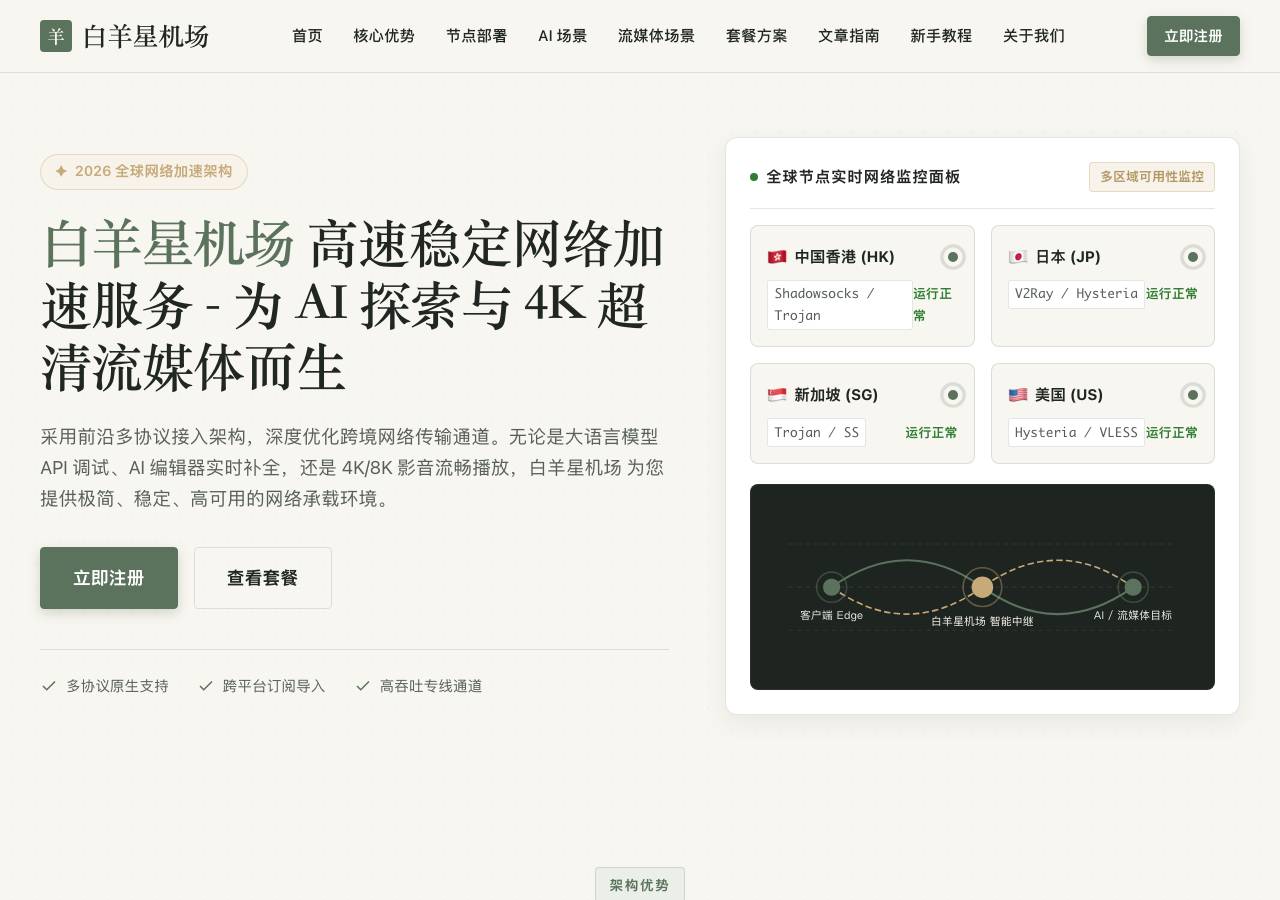
The page is a Chinese proxy/VPN subscription service ('机场') under its own brand 白羊星, which matches the pinyin domain baiyangxi. It advertises Shadowsocks, Trojan, V2Ray and Hysteria nodes, and Netflix appears only as a streaming-unlock feature, not as impersonation. There is no login form and no borrowed branding.
The domain baiyangxi.lol operates a VPN/proxy acceleration service ('白羊星机场' = 'Aries Airport') offering Shadowsocks, Trojan, V2Ray, and Hysteria protocols. While the page title mentions 'netflix' (likely for SEO), the actual service is a network circumvention tool, not Netflix impersonation. The .lol TLD combined with the abuse-flagging protocols and circumvention language (anti-blocking, geolocation unlocking) indicate this is infrastructure abuse rather than phishing.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, September 26, 2026
Same data as JSON: /api/zone/domain/baiyangxi.lol. This page is not indexed by search engines and does not link to the site it describes.