be-bestandsupdates.info
Appeared in the .info zone on Saturday, September 26, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
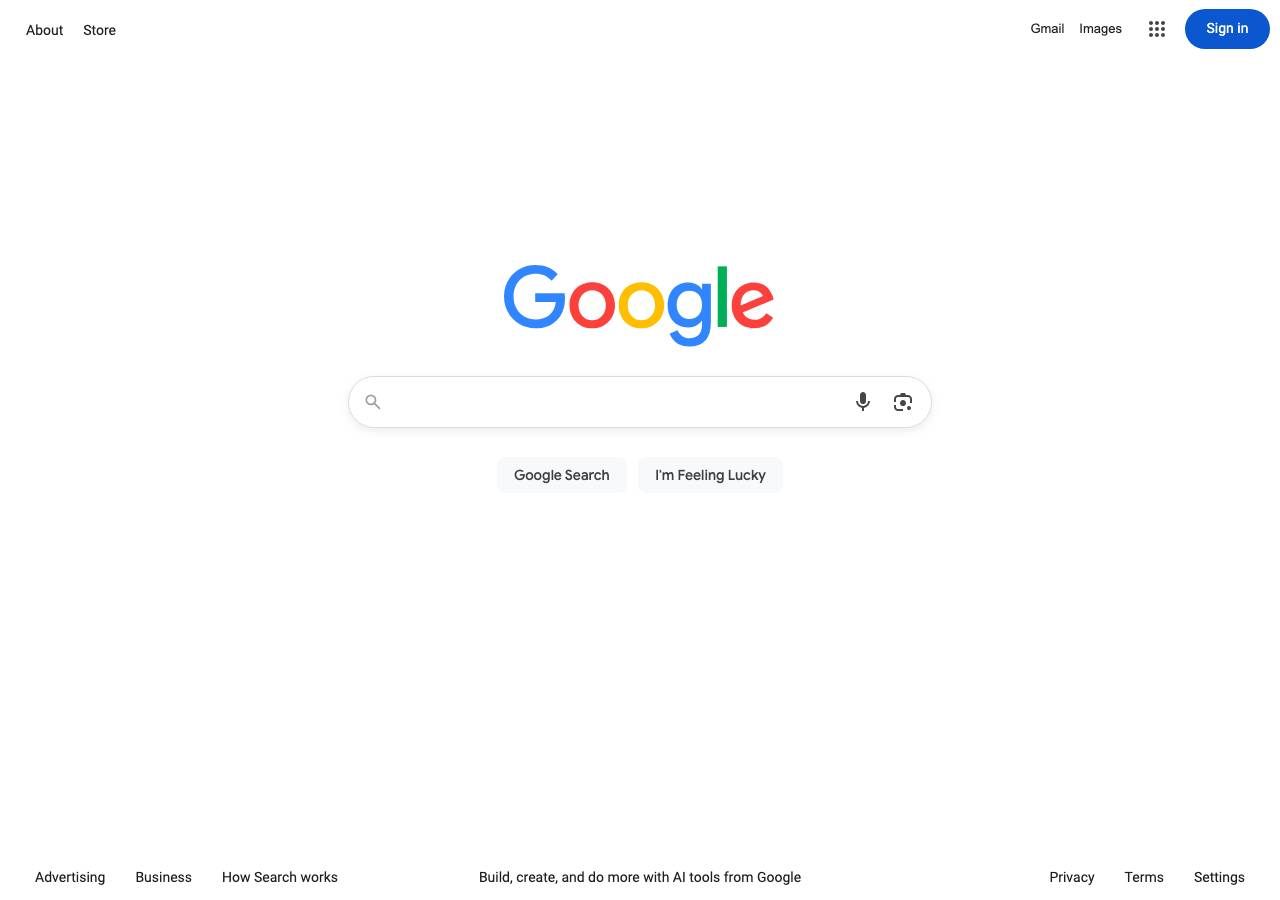
The domain serves no content of its own. It points its nameservers at ns1/ns2.google.com and simply lands on the real Google homepage, so the Google form and branding are not impersonation. Still, the throwaway .info name via NICENIC, with a 'be-' Belgium-style prefix and the lure word 'bestandsupdates' ('file updates'), plus a decoy redirect to Google, fits a cloaked phishing domain waiting to be armed.
typesafe first pass (gate 0.4): p=suspicious:0.52 benign:0.27 abuse:0.11 | impersonates=0.34 credential=0.51 parked=0.52 evidence=1.5 | target=none:0.64
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, September 26, 2026
Same data as JSON: /api/zone/domain/be-bestandsupdates.info. This page is not indexed by search engines and does not link to the site it describes.