consumidor.lol
Appeared in the .lol zone on Sunday, September 20, 2026; by the end of that day the census found active website about saas & tech. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
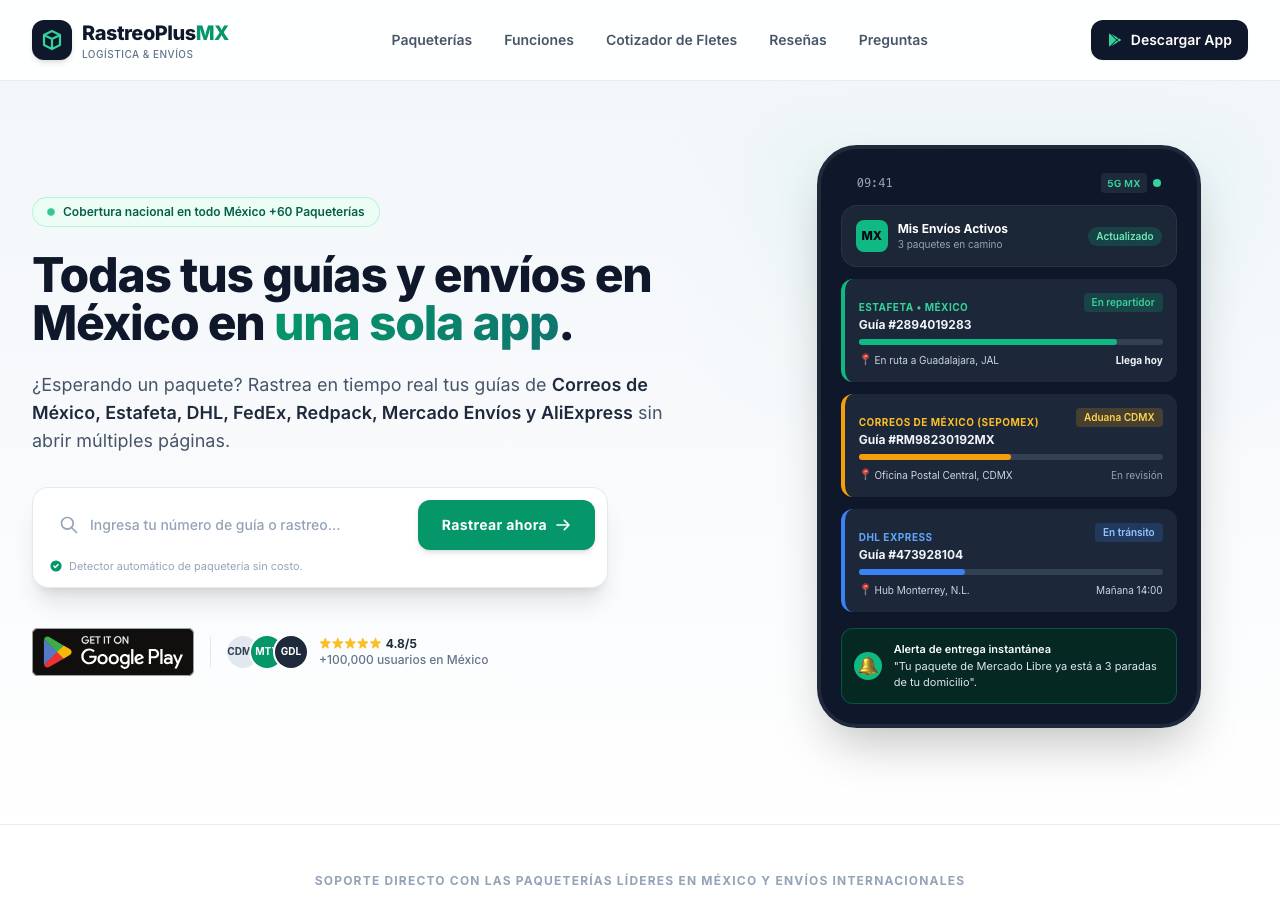
Site presents its own brand 'RastreoPlus MX', a parcel-tracking aggregator; DHL/FedEx/Estafeta are named as supported carriers rather than impersonated, and the only form is a tracking-number GET to itself — no credential or payment capture. Still odd: a brand-new .lol domain named 'consumidor' unrelated to the site brand, behind Cloudflare, with eight links funnelling to a Google Play app install, which fits a tracking-lure doorway/app-install funnel rather than a real logistics service.
The domain consumidor.lol hosts 'RastreoPlus', a parcel tracking aggregator that impersonates DHL and FedEx branding and UI to deceive users into entering tracking numbers into a form posting to itself. The page displays fake tracking data and brand logos (DHL Express, FedEx) to establish false authority, with no legitimate connection to these carriers. The sealed-room form pattern (input→self, no offsite links except decoy Google Play) and .lol TLD are consistent with phishing infrastructure de
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, September 20, 2026
Same data as JSON: /api/zone/domain/consumidor.lol. This page is not indexed by search engines and does not link to the site it describes.