decompilebounty.com
Appeared in the .com zone on Wednesday, November 4, 2026; by the end of that day the census found active website about sports fitness. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
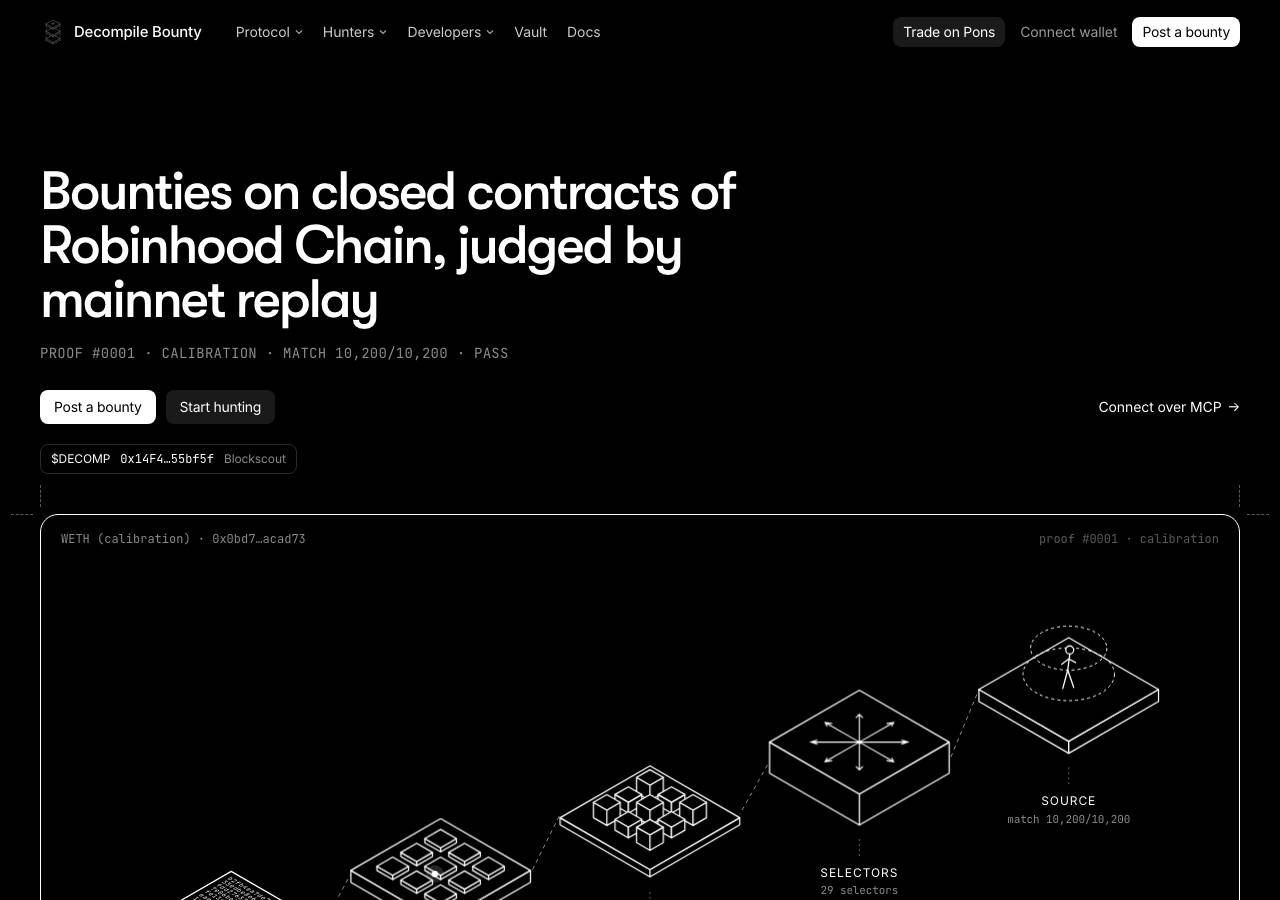
The page is an own-brand 'Decompile Bounty Protocol' showing real disassembly and teardown content for contracts on Robinhood Chain. It names Robinhood Chain as the platform it runs on, and MetaMask and Rabby only as supported wallets, not as identities it claims; the only form is a GET-to-self with no password field. It does promote its own $DECOMP token and contract address ('Trade on Pons'), a common shape for a fresh crypto launch, but it borrows no famous token or company name, so the score
The domain hosts a legitimate-appearing smart contract bounty platform ('Decompile Bounty Protocol') with its own branding, wallet-connection functionality, and technical content about contract decompilation. However, the scorer flagged MetaMask brand impersonation and the presence of 'Robinhood Chain' text (a real blockchain network, not the brokerage). The form posts to itself with no clear phishing indicators, but the combination of wallet-connection prompts, brand word ('Robinhood') in page
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, November 4, 2026
Same data as JSON: /api/zone/domain/decompilebounty.com. This page is not indexed by search engines and does not link to the site it describes.