devref.shop
Appeared in the .shop zone on Monday, September 14, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
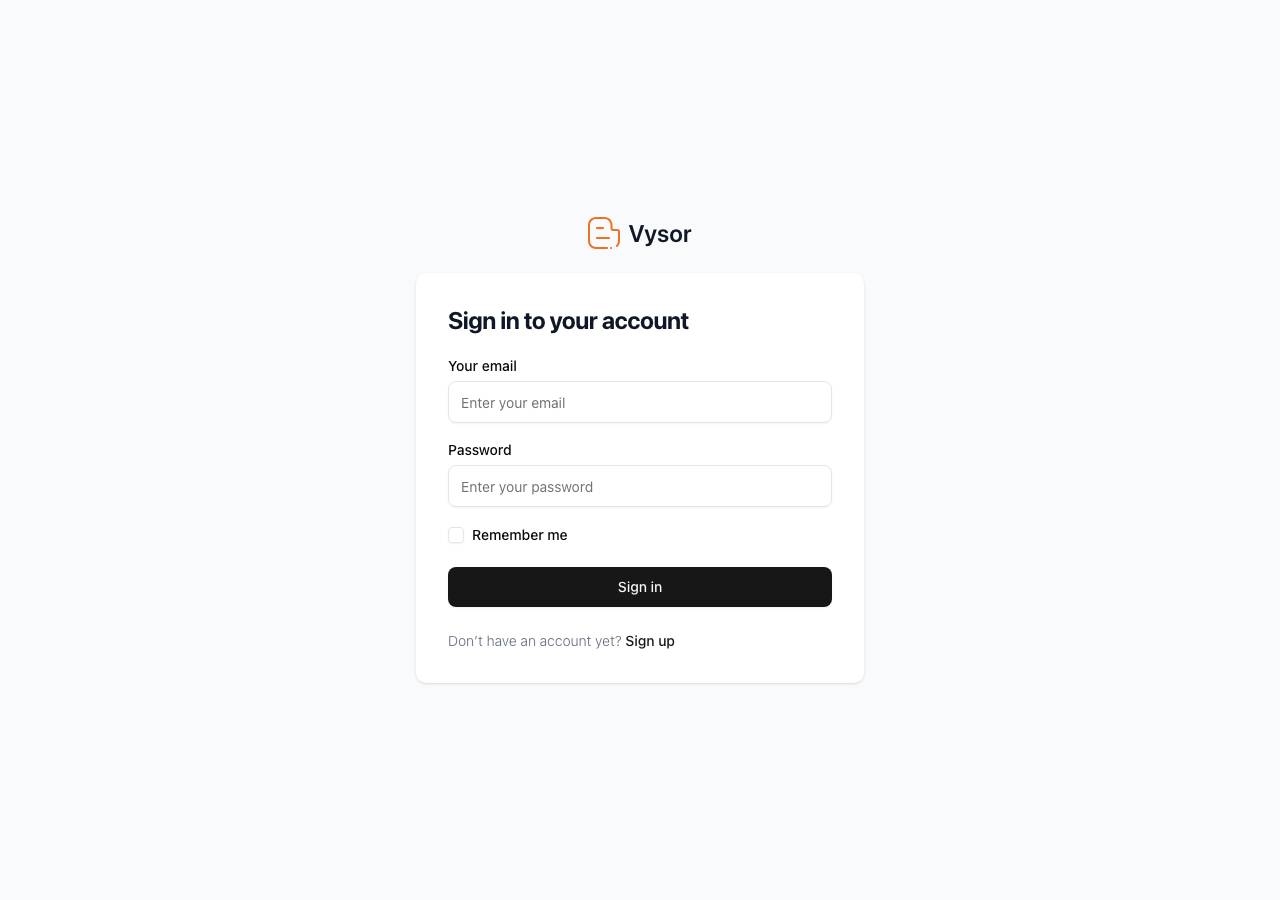
Fresh Vercel-hosted domain serving only a self-posting email/password form titled "Sign in | Vysor", a brand the domain has no relation to; however the generic orange icon and Flowbite-style template do not reproduce Vysor's actual branding, so this may equally be a developer demo/boilerplate app ("devref" = dev reference) rather than a live credential trap.
The page displays the Vysor logo and title ('Sign in | Vysor') and presents a credential-capture form (email + password) that posts to itself with no legitimate offsite links—the classic sealed-room phishing pattern. The domain devref.shop has no legitimate connection to Vysor and uses parking nameservers, confirming this is an impersonation attack designed to harvest Vysor user credentials.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, September 14, 2026
Same data as JSON: /api/zone/domain/devref.shop. This page is not indexed by search engines and does not link to the site it describes.