directdeliveriesinc.app
Appeared in the .app zone on Tuesday, November 3, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
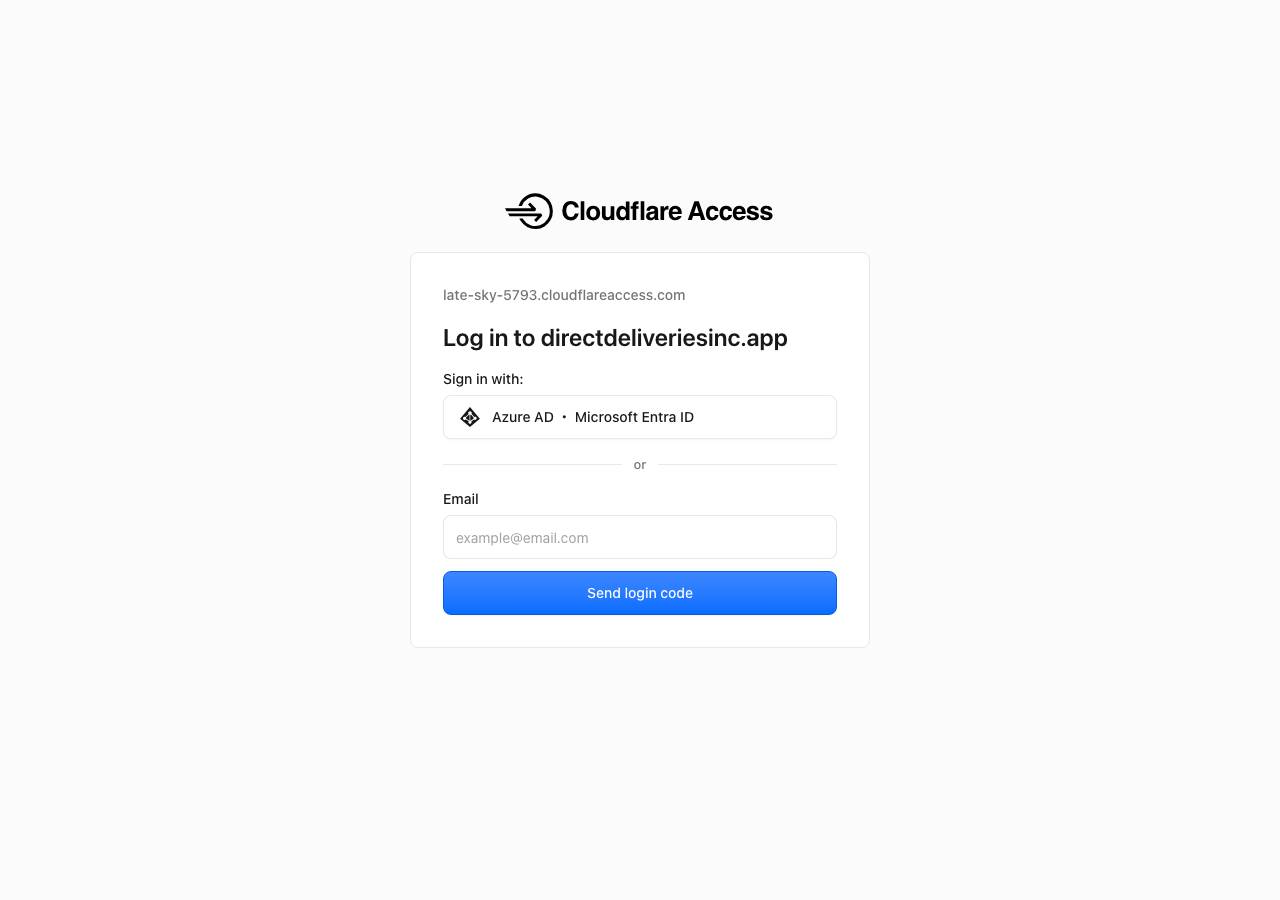
The domain sits behind a real Cloudflare Access gate (the rosesinmay.cloudflareaccess.com team domain, a signed JWT for this hostname, and Azure AD/Entra SSO through login.microsoftonline.com). That is a business locking down its own internal app, not a page pretending to be Cloudflare or Microsoft. The name is a generic delivery-company name with no brand in it, and the login form belongs to the genuine Access service.
The domain directdeliveriesinc.app redirects to a page displaying the Cloudflare Access logo and branding, with a login form claiming "Log in to directdeliveriesinc.app" but hosting on rosesinmay.cloudflareaccess.com. The page impersonates Cloudflare Access infrastructure to capture credentials (email and login code) for a non-existent business domain. The form posts credentials back to the attacker-controlled subdomain, not to Cloudflare's legitimate services, creating a sealed-room phishing tr
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, November 3, 2026
Same data as JSON: /api/zone/domain/directdeliveriesinc.app. This page is not indexed by search engines and does not link to the site it describes.