droolies.lol
Appeared in the .lol zone on Wednesday, November 4, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The page has a form requesting wallet address (0x...) and numeric inputs, posting to itself with no external links—a classic phishing topology. However, 'Droolies' appears to be an original NFT project branding on Robinhood Chain, not an impersonation of an established organisation; the OpenSea mention is contextual (where NFTs are minted), not impersonation. The sealed-room form shape and wallet-harvest fields are red flags for credential/asset theft, but without proof the project itself is fra
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, November 4, 2026
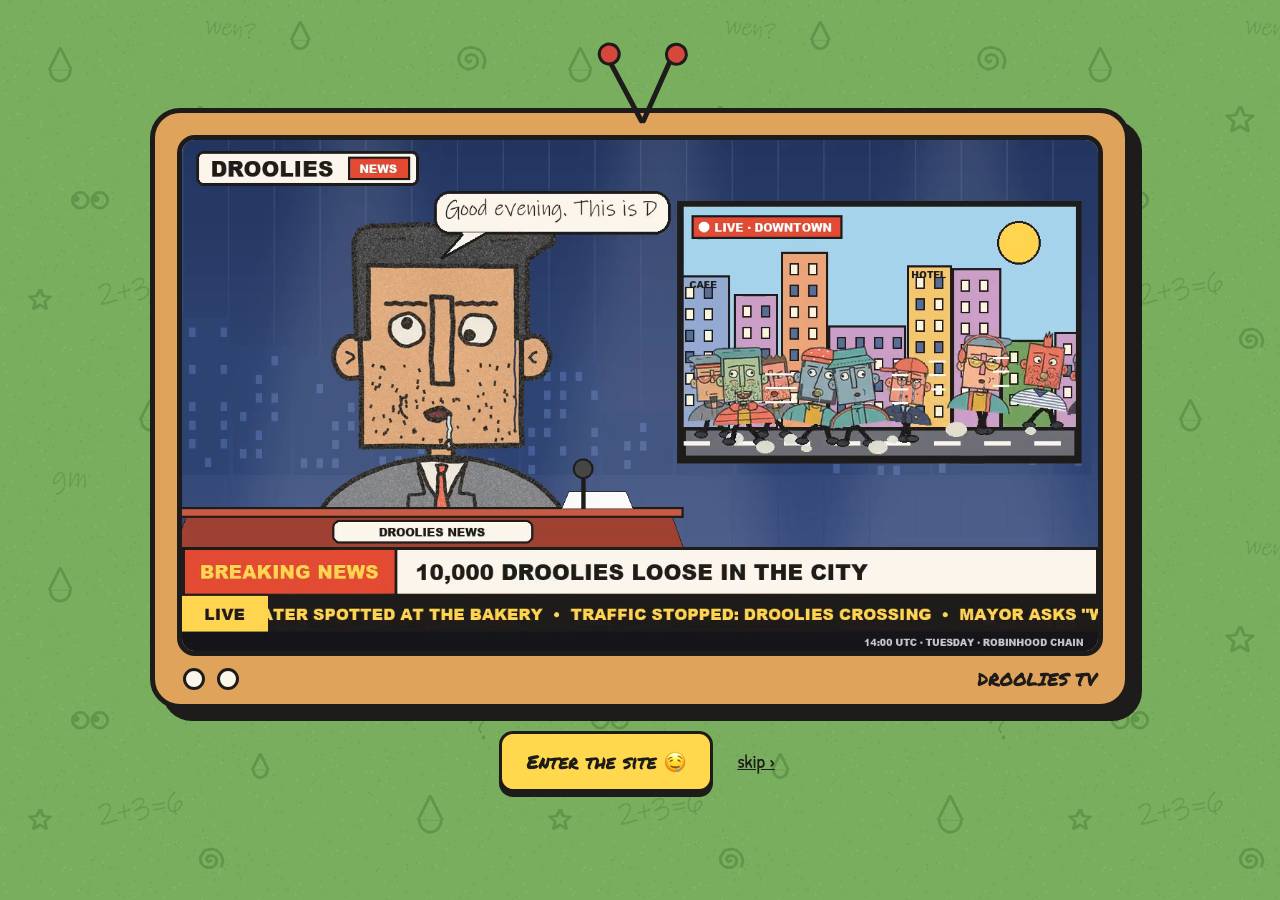
Same data as JSON: /api/zone/domain/droolies.lol. This page is not indexed by search engines and does not link to the site it describes.