dwlvcaap.shop
Appeared in the .shop zone on Wednesday, September 16, 2026; by the end of that day the census found active website about e-commerce & retail. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
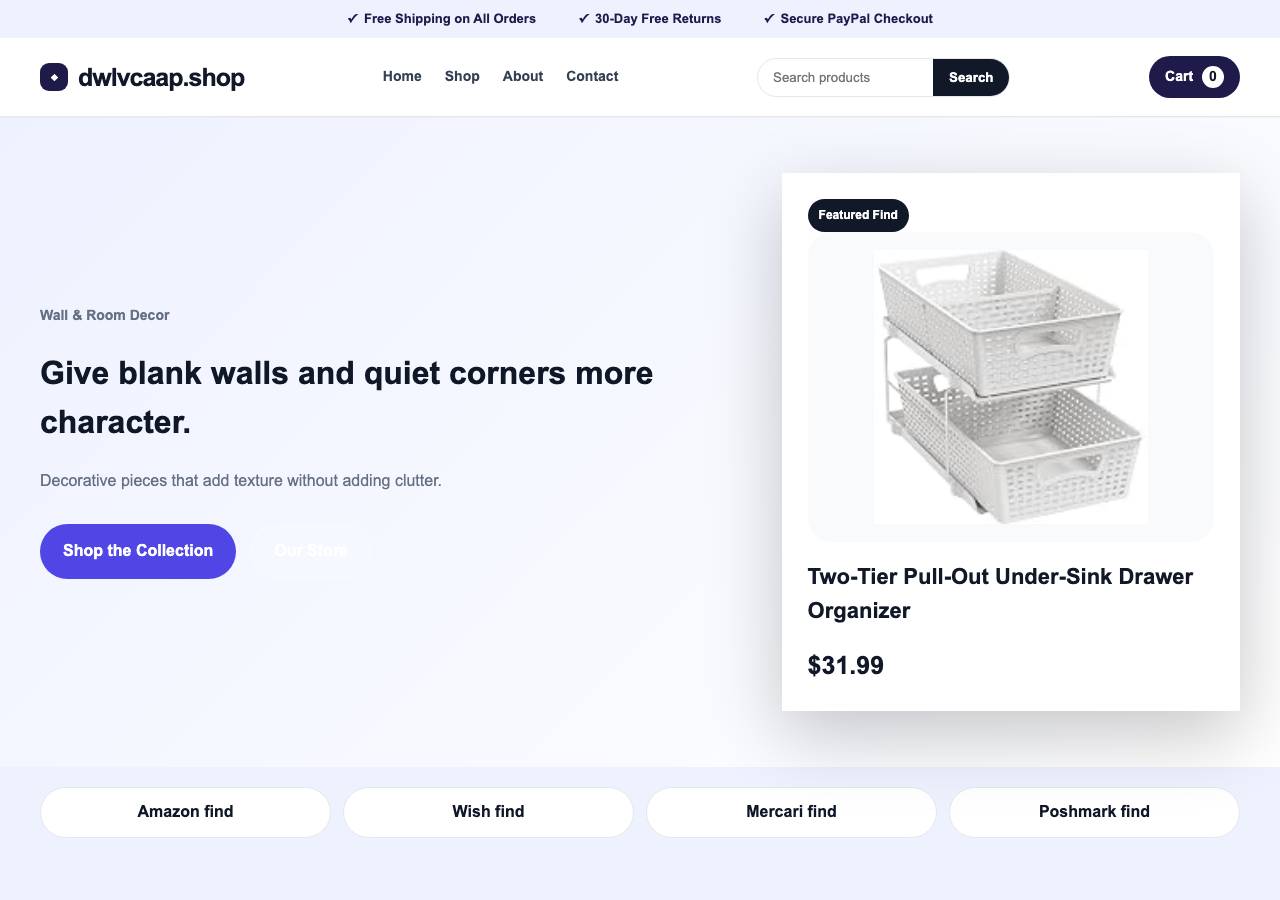
Random-string .shop domain hosting a thin four-product 'store' whose items are openly scraped from Amazon/Wish/Mercari/Poshmark listings, with generic trust badges (free shipping, 30-day returns) and no offsite or real merchant identity — the classic throwaway fake-shop shape. The 'Secure PayPal Checkout' text is a payment mention, not PayPal impersonation, and the forms are cart posts rather than credential capture, so this is fraud without brand impersonation.
The page impersonates PayPal by prominently displaying 'Secure PayPal Checkout' in the header and throughout the site copy, yet the domain (dwlvcaap.shop) is not PayPal's. The page contains multiple forms posting to itself with hidden fields (action, slug, cart_token) in a sealed-room architecture with no offsite links—a classic credential-capture phishing pattern. The scorer correctly identified brand impersonation and form-on-brand-page signals; this is a fake e-commerce front using PayPal bra
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, September 16, 2026
Same data as JSON: /api/zone/domain/dwlvcaap.shop. This page is not indexed by search engines and does not link to the site it describes.