esl-org-mobile-alerts.cfd
Appeared in the .cfd zone on Monday, October 5, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
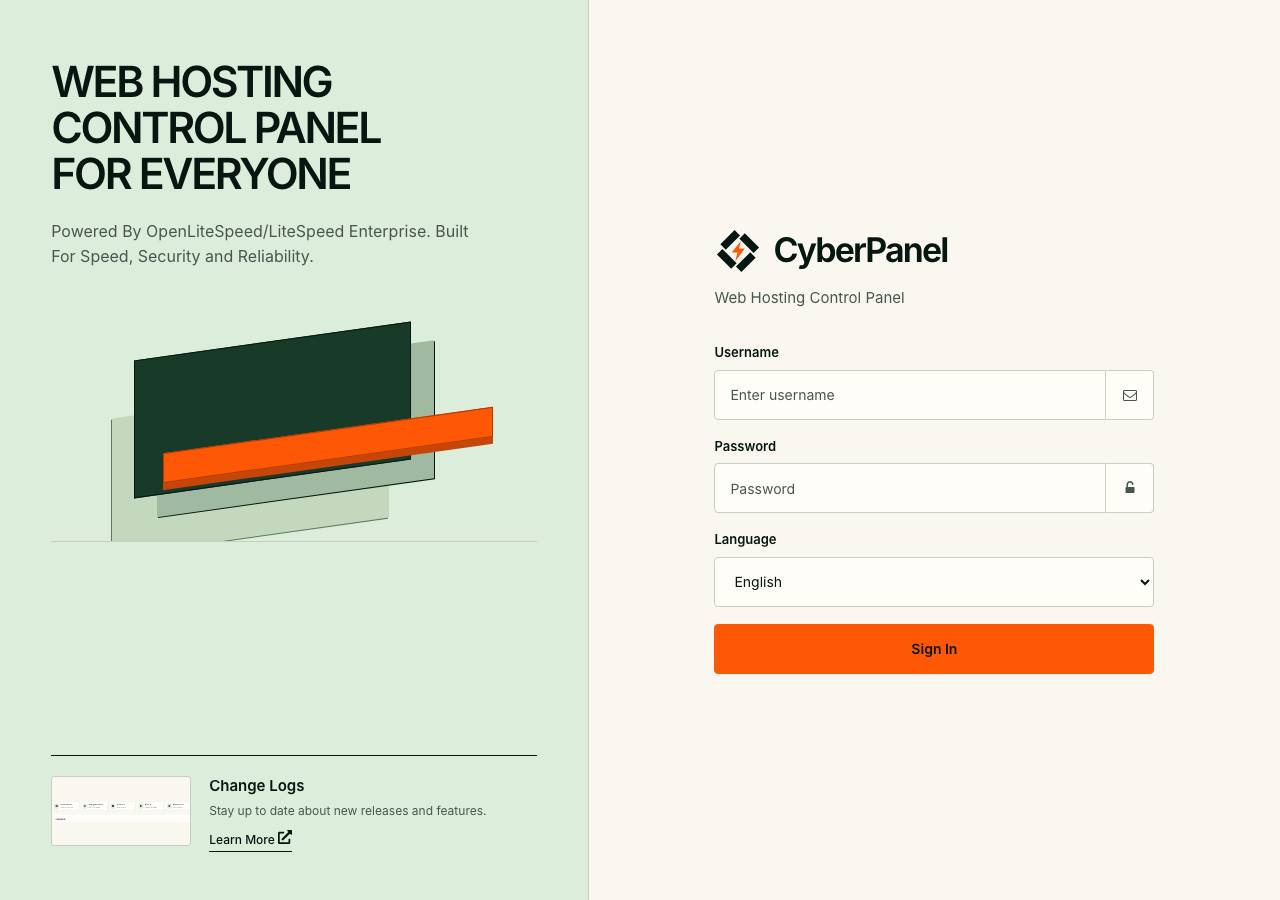
The page is a stock CyberPanel hosting-control-panel login, which is the server's own admin panel and not a brand impersonation. The 'mobile≈tmobile' match is spurious. Still, the throwaway .cfd name 'esl-org-mobile-alerts' reads like smishing-alert infrastructure, and it is one of 28 identical freshly staged pages, so this looks like a campaign being set up but not yet decisive.
The domain name impersonates ESL/mobile alerts via typosquat (mobile≈tmobile, alert keywords) to lure victims, but the actual page impersonates CyberPanel's web hosting control panel with its logo, branding, and login form. The password form posts to itself with no legitimate offsite links—the classic sealed-room phishing pattern designed to capture credentials.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 5, 2026
Same data as JSON: /api/zone/domain/esl-org-mobile-alerts.cfd. This page is not indexed by search engines and does not link to the site it describes.