f7wzz0om.top
Appeared in the .top zone on Monday, October 19, 2026; by the end of that day the census found active website about hosting & domains. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
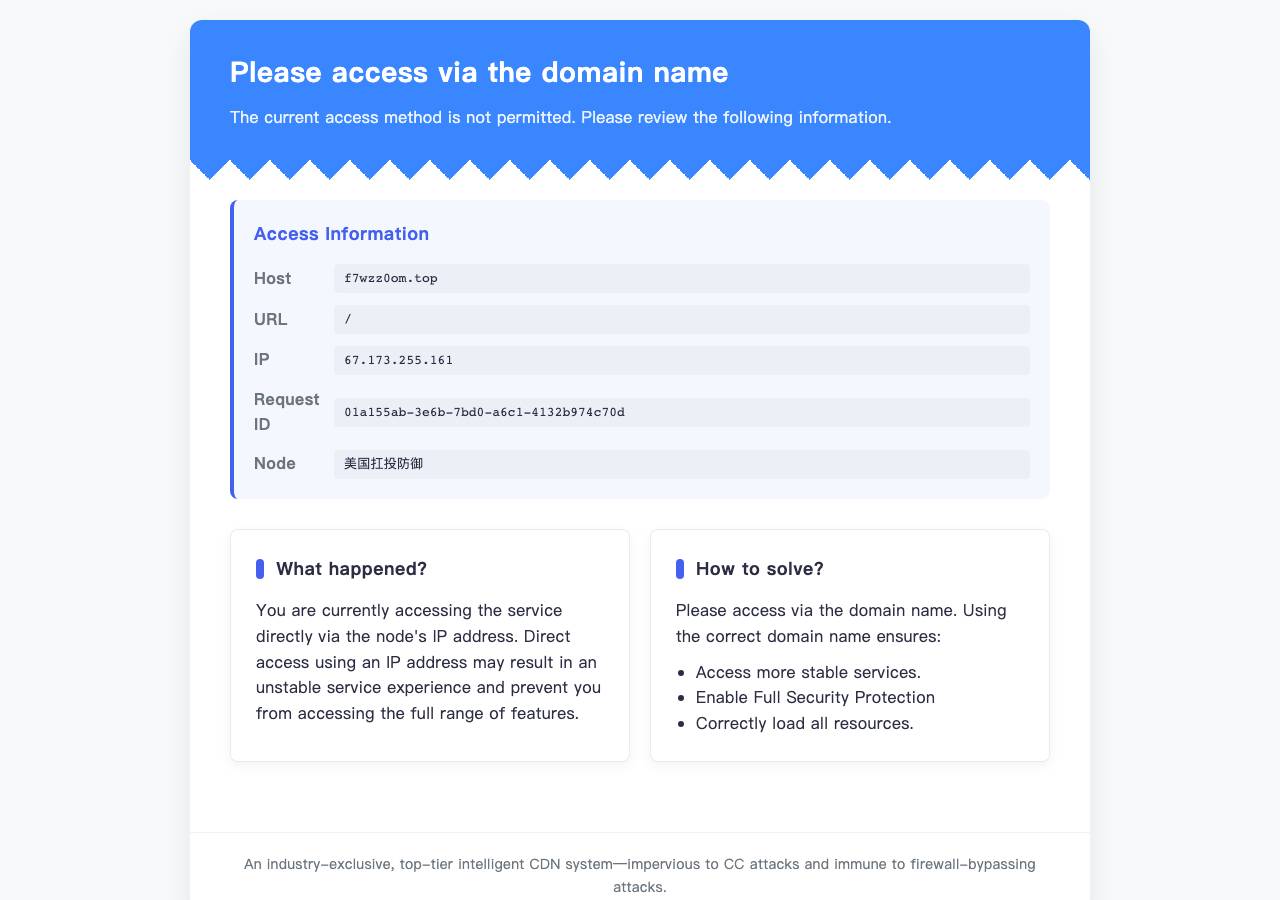
The only page is a Chinese CDN 'access via the domain name' error whose node is labelled 美国扛投防御 ('US complaint-resistant defense'), a bulletproof-hosting marker often fronting gambling or scam sites on random-string .top names. There is no content, form or links, and the 'zoom' leet match in f7wzz0om looks incidental to a random string, so this is not decisive impersonation.
typesafe first pass (gate 0.4): p=abuse:0.58 suspicious:0.21 benign:0.21 | impersonates=0.09 credential=0.03 parked=0.85 evidence=1.3 | target=zoom:0.80
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 19, 2026
Same data as JSON: /api/zone/domain/f7wzz0om.top. This page is not indexed by search engines and does not link to the site it describes.