fedex-wt.com
Appeared in the .com zone on Thursday, October 15, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The name pairs the FedEx brand with 'wt' (likely waybill tracking), sits on Alibaba Cloud DNS that FedEx would not use, and redirects to an unrelated brand's site (apple.com). That redirect is a common cloaking pattern for parcel-phish domains that show scanners a harmless page, but no FedEx-impersonating page was observed, so this is a brand-squat rather than confirmed phishing.
The domain fedex-wt.com contains a FedEx brand typosquat coupled with a redirect to Apple's legitimate site, a classic phishing setup designed to deceive users into visiting a spoofed domain before redirecting to the real site to capture credentials or data. The combination of a deceptive domain name with Alidns nameservers (commonly used in phishing infrastructure) and the immediate offsite redirect pattern indicates this is a phishing campaign using a decoy redirect.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 15, 2026
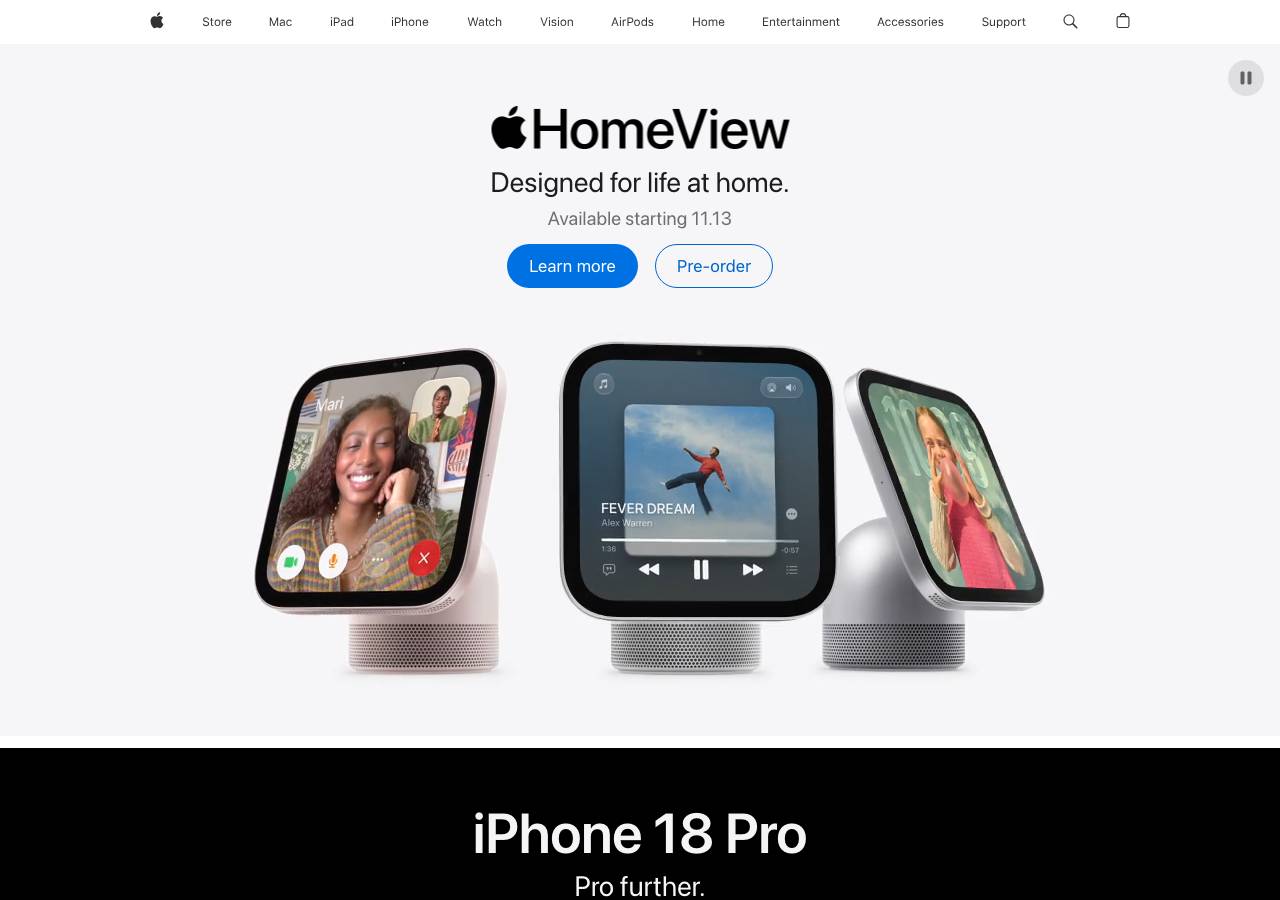
Same data as JSON: /api/zone/domain/fedex-wt.com. This page is not indexed by search engines and does not link to the site it describes.