fedextq.com
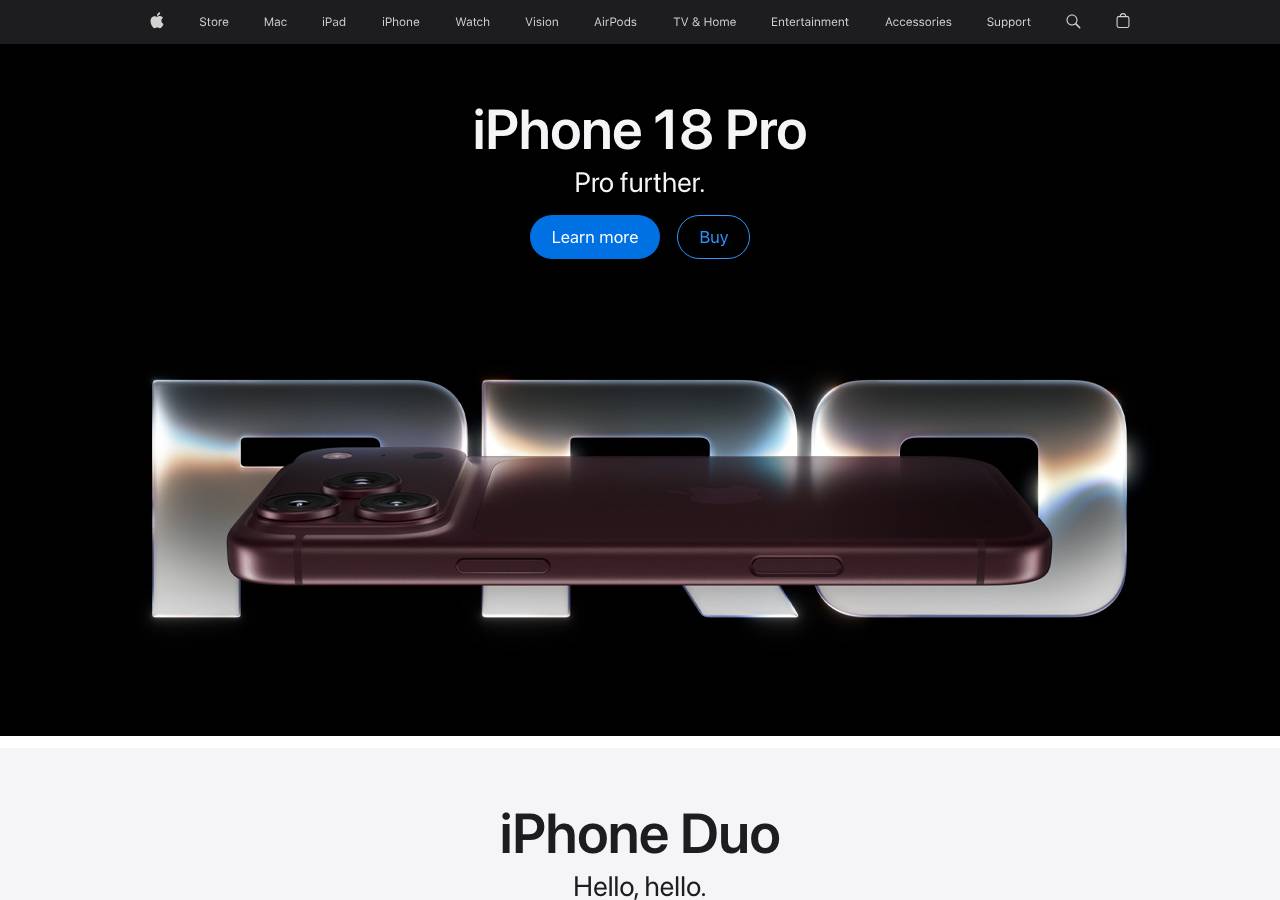
Appeared in the .com zone on Sunday, October 4, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The name pairs the distinctive brand 'fedex' with a random suffix ('tq'). It was registered through Onamae on share-dns nameservers, a setup common in Japanese parcel-smishing campaigns, and it redirects to an unrelated brand (apple.com), which is a typical cloaking move to hide a phish from scanners. No deceptive page is served yet, so this is a brand-squat rather than confirmed phishing.
The domain fedextq.com combines two unrelated brand names (FedEx + TQ suffix) and immediately redirects to Apple's legitimate site, a classic typosquat pattern. The non-standard nameservers (share-dns.com/net) and GMO registrar are consistent with throwaway redirect infrastructure. This is a brand-squat with no independent content whose only plausible purpose is deception or SEO manipulation.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, October 4, 2026
Same data as JSON: /api/zone/domain/fedextq.com. This page is not indexed by search engines and does not link to the site it describes.