fidelityandsecurity.app
Appeared in the .app zone on Thursday, October 1, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
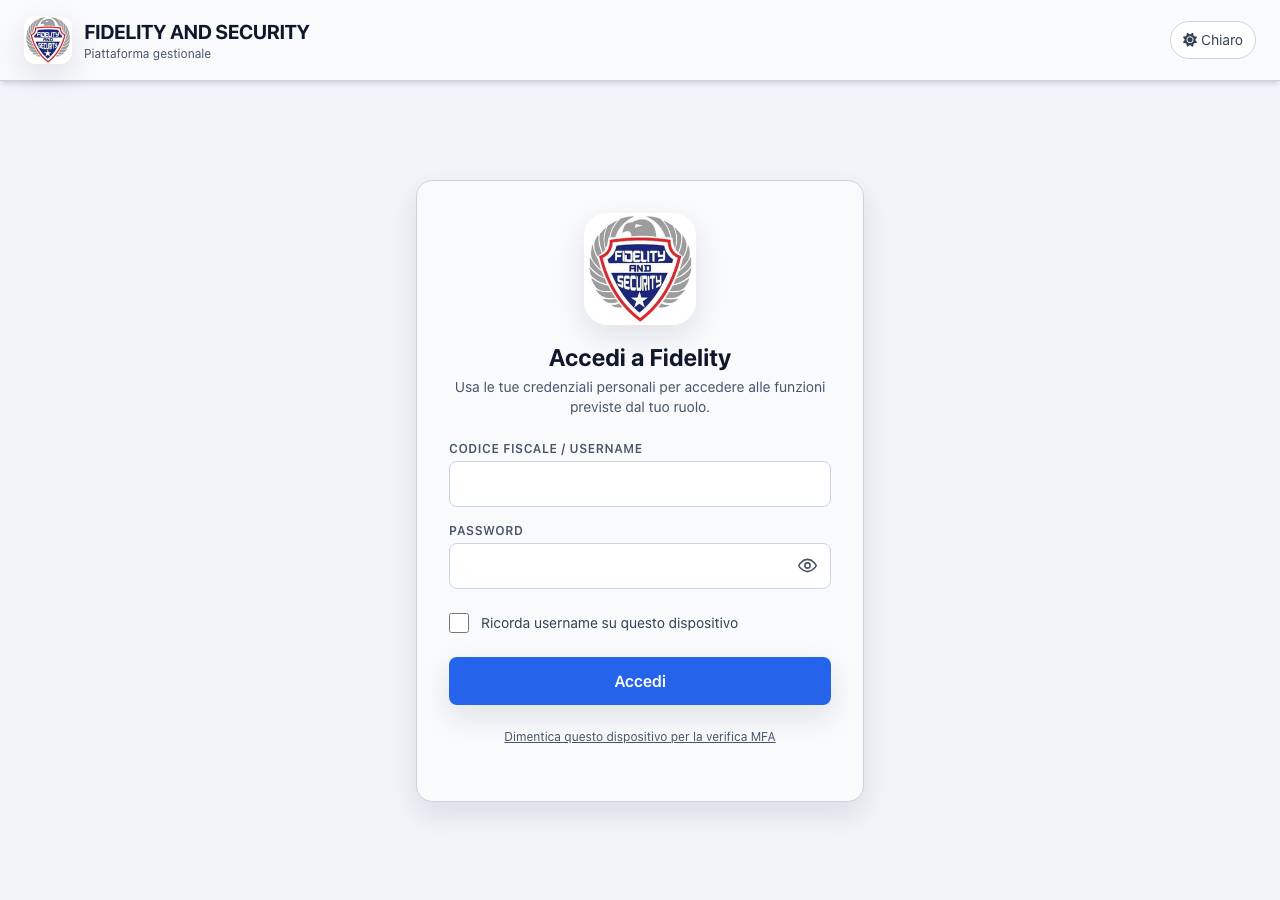
This is the internal management portal of an Italian private-security firm called "Fidelity and Security". It has its own eagle-shield logo, a codice fiscale login, and staff modules such as guard shift scheduling, patrol interventions, EasyPlan/Sabanet history and absence requests. Nothing references Fidelity Investments' branding, accounts or financial services, so the 'fidelity' match is a coincidental business name, not impersonation.
The domain impersonates Fidelity with a login page titled 'Accedi a Fidelity' (Log in to Fidelity) using Fidelity branding and a shield logo, requesting credentials (codice fiscale/username and password) that post to the same domain with no legitimate Fidelity infrastructure present. The sealed-room architecture—password form posting to self with no offsite links—is the classic phishing shape.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 1, 2026
Same data as JSON: /api/zone/domain/fidelityandsecurity.app. This page is not indexed by search engines and does not link to the site it describes.