filepackage-documentm365778-okta.info
Appeared in the .info zone on Thursday, October 8, 2026; by the end of that day the census found active website about real estate. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
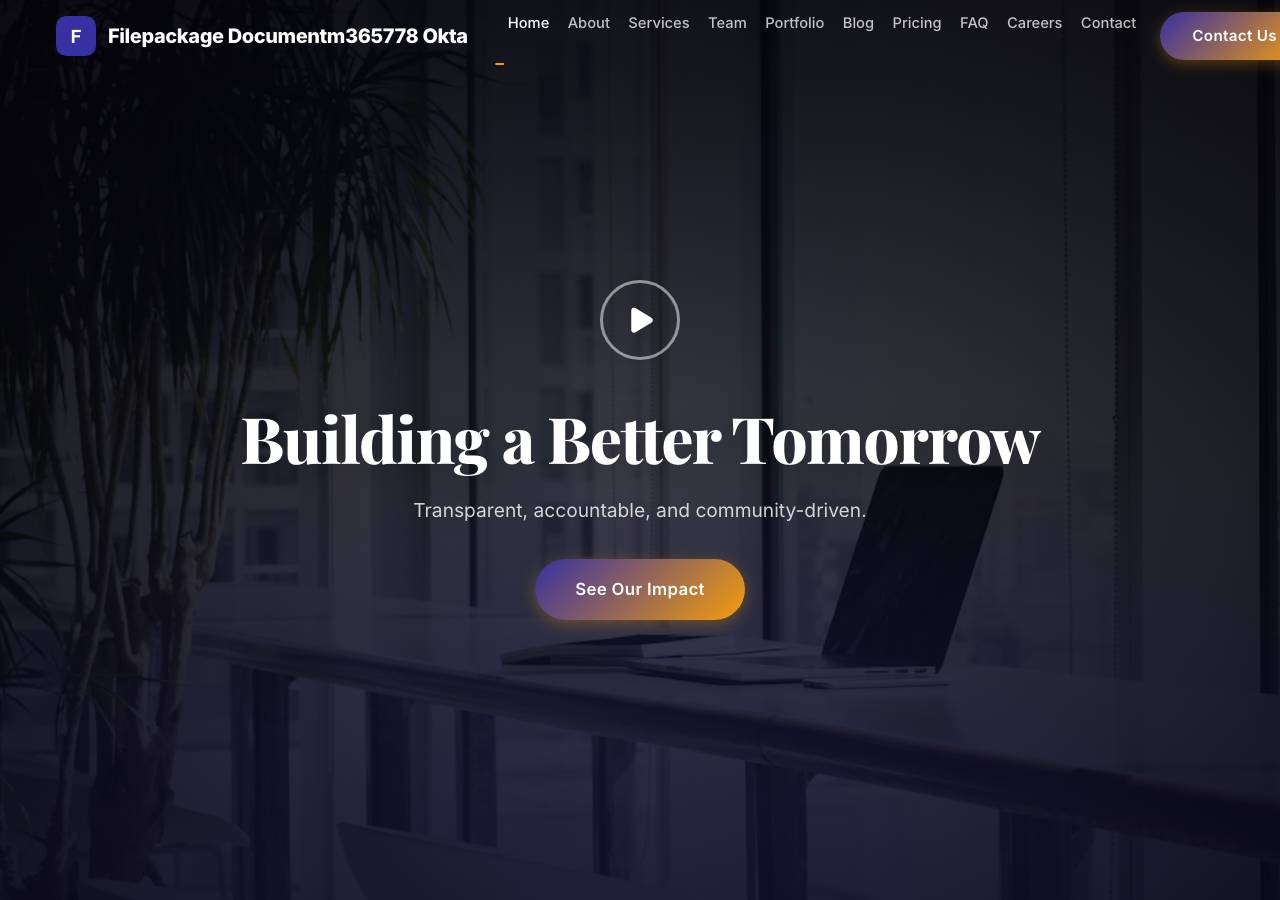
The name stacks Okta and M365 with file/document-package lure words and digits, which is the shape of a credential-phish hostname. The page itself is a generic 'Lumen Networks' corporate template, with the domain auto-inserted as the logo and only an email newsletter form. That makes it a brand-squat with decoy or cloaking content rather than a live Okta login clone.
Domain name embeds 'okta' with obfuscating padding ('filepackage-documentm365778-okta.info'), page title claims 'Lumen Networks' while the browser tab/header shows 'Filepackage Documentm365778 Okta', and a form requesting email posts to itself with no offsite links—a classic sealed-room phishing pattern designed to harvest credentials by impersonating Okta infrastructure.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 8, 2026
Same data as JSON: /api/zone/domain/filepackage-documentm365778-okta.info. This page is not indexed by search engines and does not link to the site it describes.