gowisp.fun
Appeared in the .fun zone on Sunday, October 25, 2026; by the end of that day the census found active website about crypto web3. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The page uses its own 'Wisp' brand and presents itself as a privacy pool built on Robinhood Chain, not as Robinhood itself. Its only form is a GET field for looking up a public wallet address, not a credential capture. Still, a day-old .fun domain that promotes a $WISP token, asks users to connect wallets and shield funds into an unaudited pool, and lists no offsite project links fits a crypto-lure or drainer shape without being decisive.
The page impersonates Robinhood by prominently featuring 'Robinhood Chain' throughout (title, headings, branded mockup) and includes a functional form ('Read your wallet's diary') that posts to itself with no offsite links—the sealed-room phishing pattern. The form invites users to 'connect' their wallet or paste addresses, a classic credential/key capture attack. Wisp is presented as a Robinhood product, not a separate DeFi tool, deceiving visitors into trusting the Robinhood brand for wallet i
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, October 25, 2026
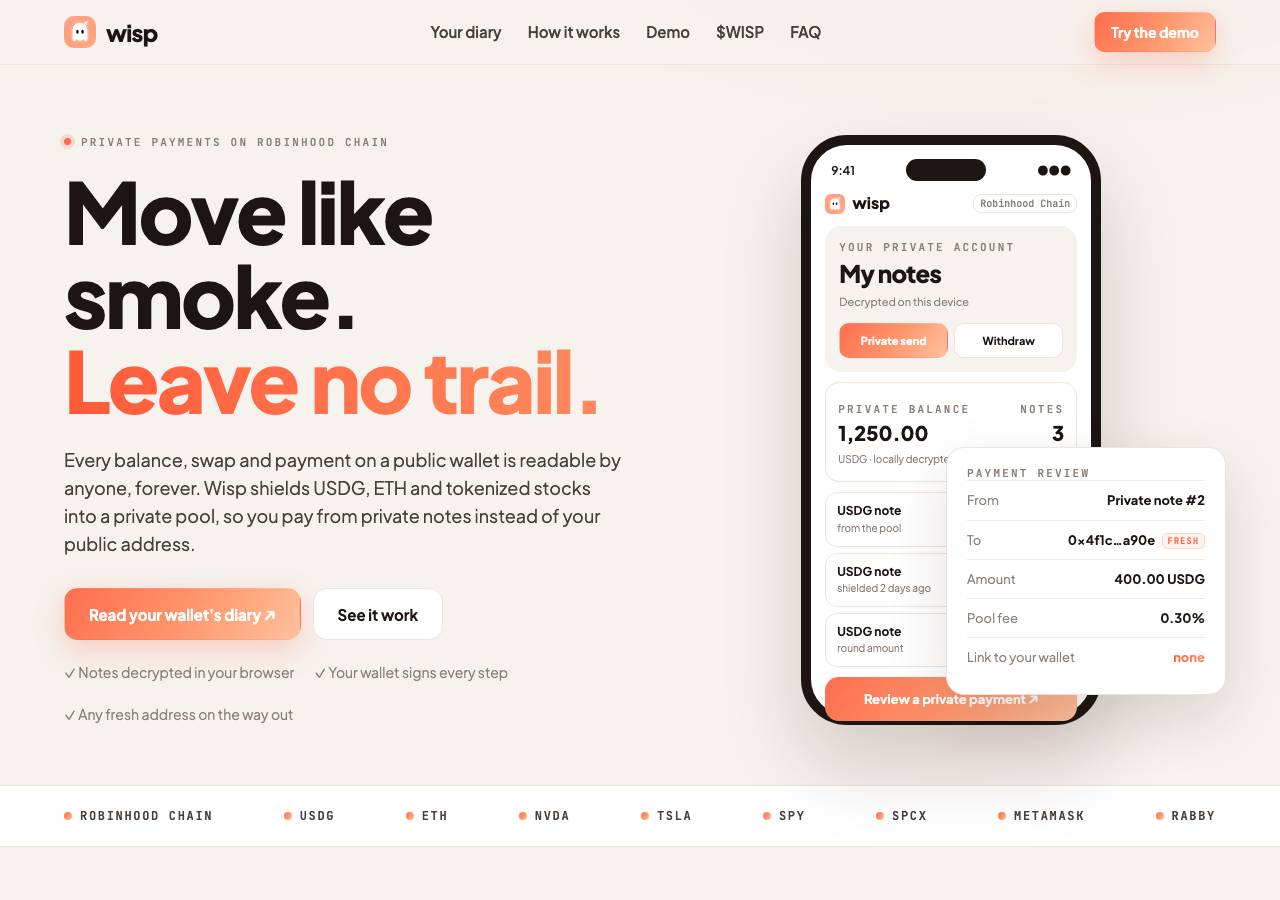
Same data as JSON: /api/zone/domain/gowisp.fun. This page is not indexed by search engines and does not link to the site it describes.