heist.monster
Appeared in the .monster zone on Sunday, November 1, 2026; by the end of that day the census found active website about crypto web3. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
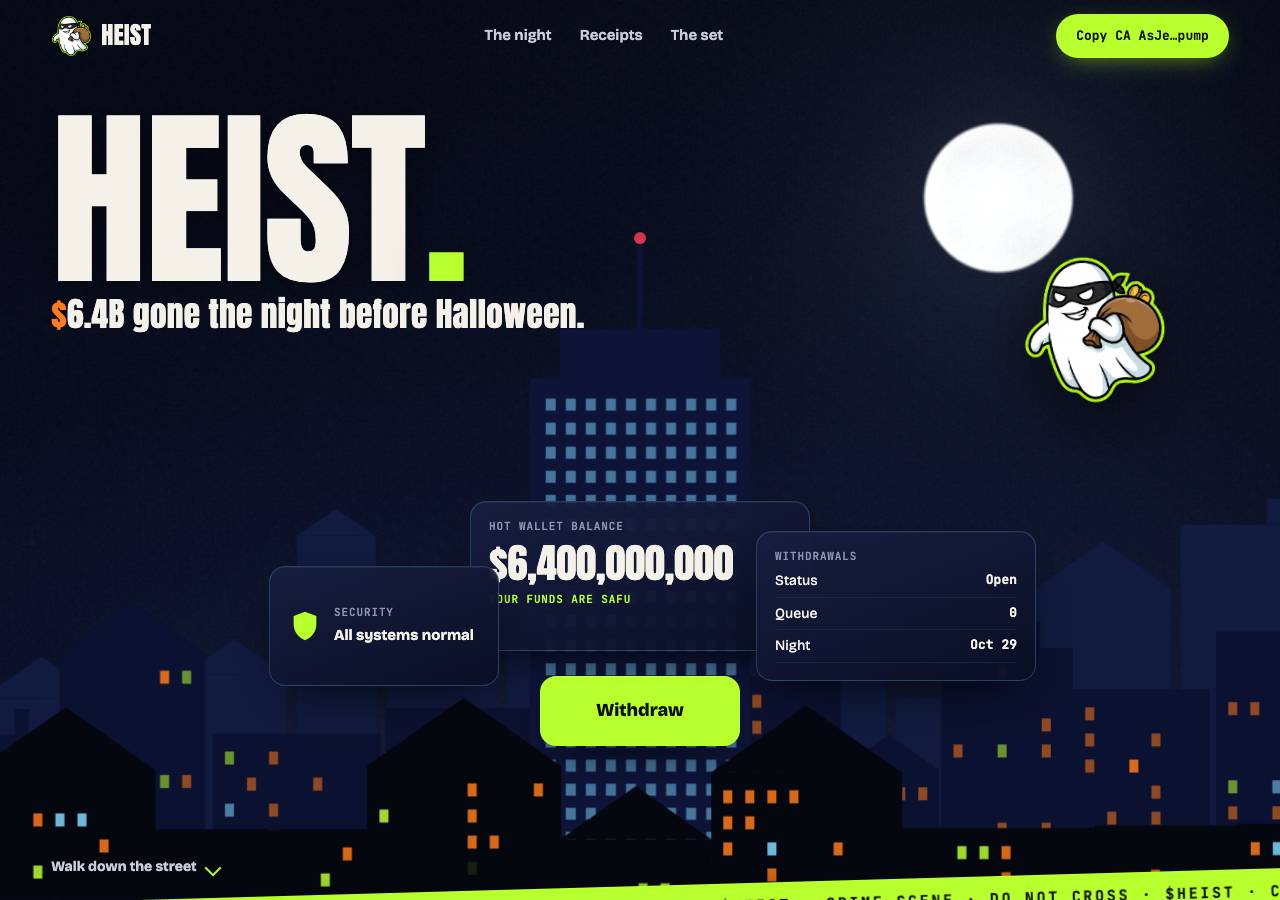
Pump.fun memecoin promo page for $HEIST with a 'Copy CA …pump' contract-address button. It trades on a claimed $6.4B Binance hack, CZ and Elon quotes, and a mock 'Withdraw / Your funds are SAFU' exchange widget to push buying the token. There is no credential form, so this is a crypto lure borrowing Binance's name, not a Binance login phish.
The page is a cryptocurrency token promotion ($HEIST) themed around a fictional Binance heist narrative, not an impersonation of Binance itself. It has its own branding, a withdraw button for the token, and links to legitimate news sources (Decrypt, Bloomberg) and crypto platforms (pump.fun). While it references Binance in the fictional heist story, the page does not impersonate Binance's login, portal, or attempt to capture credentials—it promotes a speculative crypto asset using an attention-g
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, November 1, 2026
Same data as JSON: /api/zone/domain/heist.monster. This page is not indexed by search engines and does not link to the site it describes.