https-plugngostore-myshopify-com-password.store
Appeared in the .store zone on Thursday, September 17, 2026; by the end of that day the census found other. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
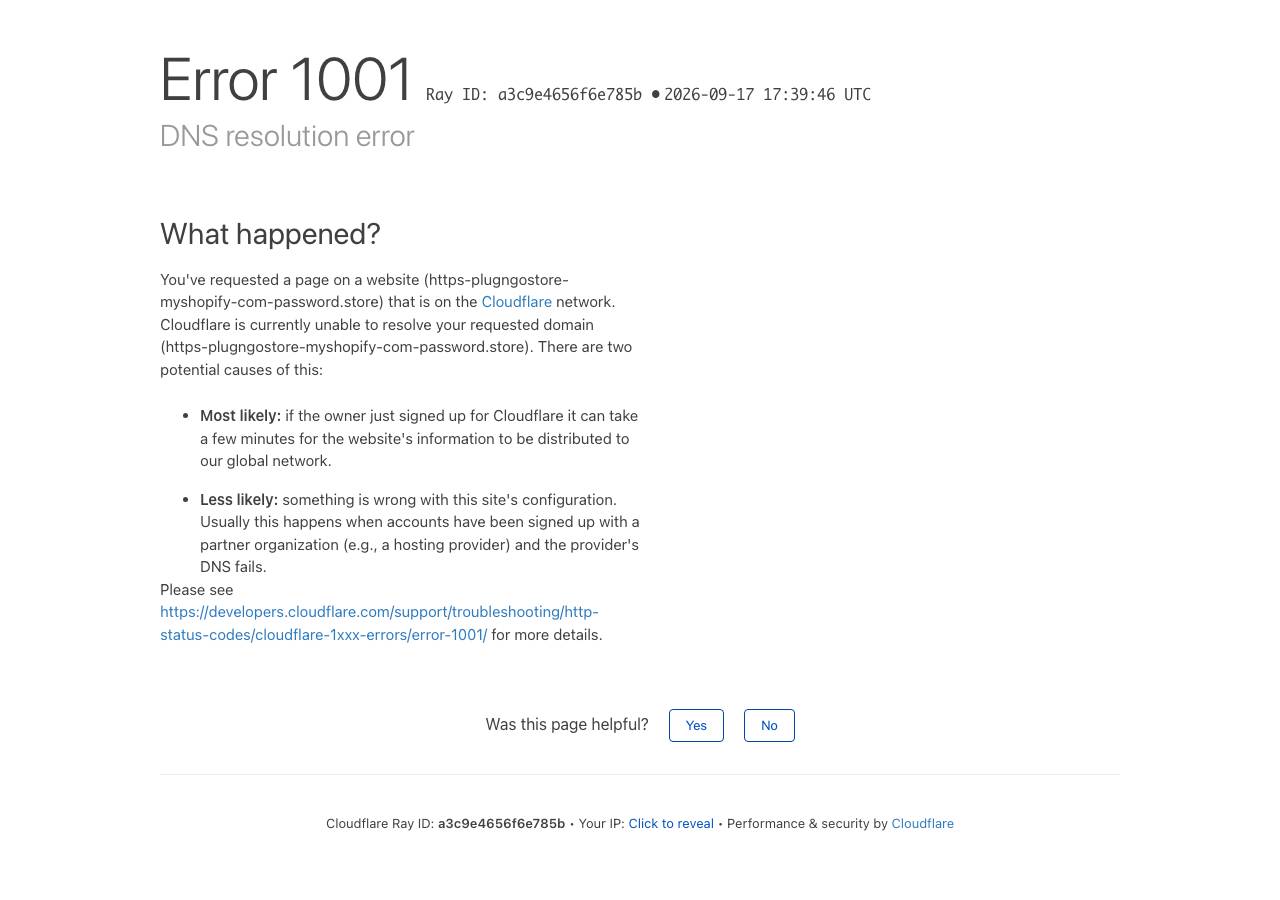
The domain is a full URL-spoof — 'https-plugngostore-myshopify-com-password.store' reproduces the Shopify storefront password-page URL (https://plugngostore.myshopify.com/password) as a hostname, a shape whose only purpose is to make a victim believe they are on Shopify; the served page is only a Cloudflare Error 1001 DNS-resolution notice (not impersonation itself), so the site is pre-launch rather than yet observed capturing credentials.
typesafe first pass (gate 0.4): p=suspicious:0.51 abuse:0.35 unreachable:0.07 | impersonates=0.44 credential=0.03 parked=0.85 evidence=1.2 | target=shopify:0.75
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, September 17, 2026
Same data as JSON: /api/zone/domain/https-plugngostore-myshopify-com-password.store. This page is not indexed by search engines and does not link to the site it describes.