hub-pay-by-mobile-casino.fun
Appeared in the .fun zone on Saturday, September 26, 2026; by the end of that day the census found redirect not followed. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
A throwaway keyword-stuffed .fun name ('pay-by-mobile-casino') 307-redirects through Cloudflare to a random-string domain's /de/registration page carrying affiliate tracking (cxd=35371_614382, utm_campaign=ATF_SeparateDE), which fits an affiliate funnel into casino sign-ups aimed at Germany (an unlicensed-gambling front). The 'mobile≈tmobile' match is a false positive: 'pay by mobile' is a generic payment term and nothing impersonates T-Mobile.
The domain hub-pay-by-mobile-casino.fun uses a brand-typo pattern ('mobile' ≈ T-Mobile) combined with payment-lure language ('pay') and immediately redirects to an unrelated obfuscated domain (e12atf8e1g.com) with UTM tracking. This redirect-without-own-content pattern, paired with the typosquat name and irrelevant destination, indicates a squat or affiliate fraud scheme rather than legitimate branding.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
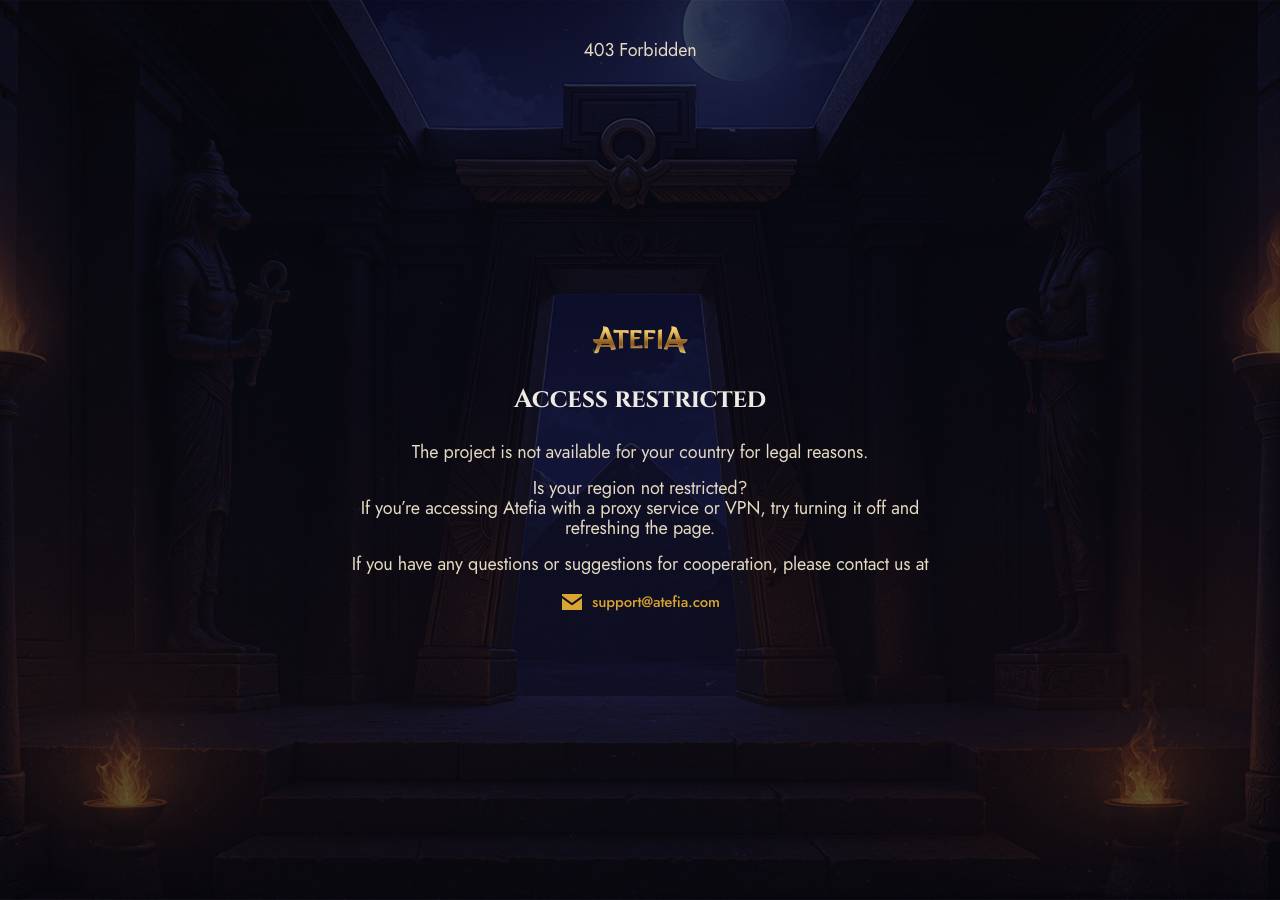
What the page looked like on Saturday, September 26, 2026
Same data as JSON: /api/zone/domain/hub-pay-by-mobile-casino.fun. This page is not indexed by search engines and does not link to the site it describes.