imgmail.link
Appeared in the .link zone on Thursday, October 15, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
'imgmail' is img+mail, not a Gmail squat: it is one of ~30 file-extension+mail domains (pngmail.fyi, sqlmail.fyi, csvmail.win, dllmail.org…) listed as supported domains on getotp.cc. That site is a self-branded Japanese mailbox-login/2FA service with no Google branding, so this is a pool domain for a disposable-mail service, not impersonation. Its shadowban-checker tooling suggests it may serve account farming, which is worth watching but not decisive.
Domain imgmail.link contains 'mail' (Gmail impersonation signal) and redirects to getotp.cc, a credential-harvesting login page with email and password fields. The destination page lists imgmail.link among 30+ lookalike domains it targets, confirming coordinated phishing infrastructure; the password form posts to getotp.cc with no legitimate purpose, and the sealed-room redirect pattern is classic phishing architecture.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 15, 2026
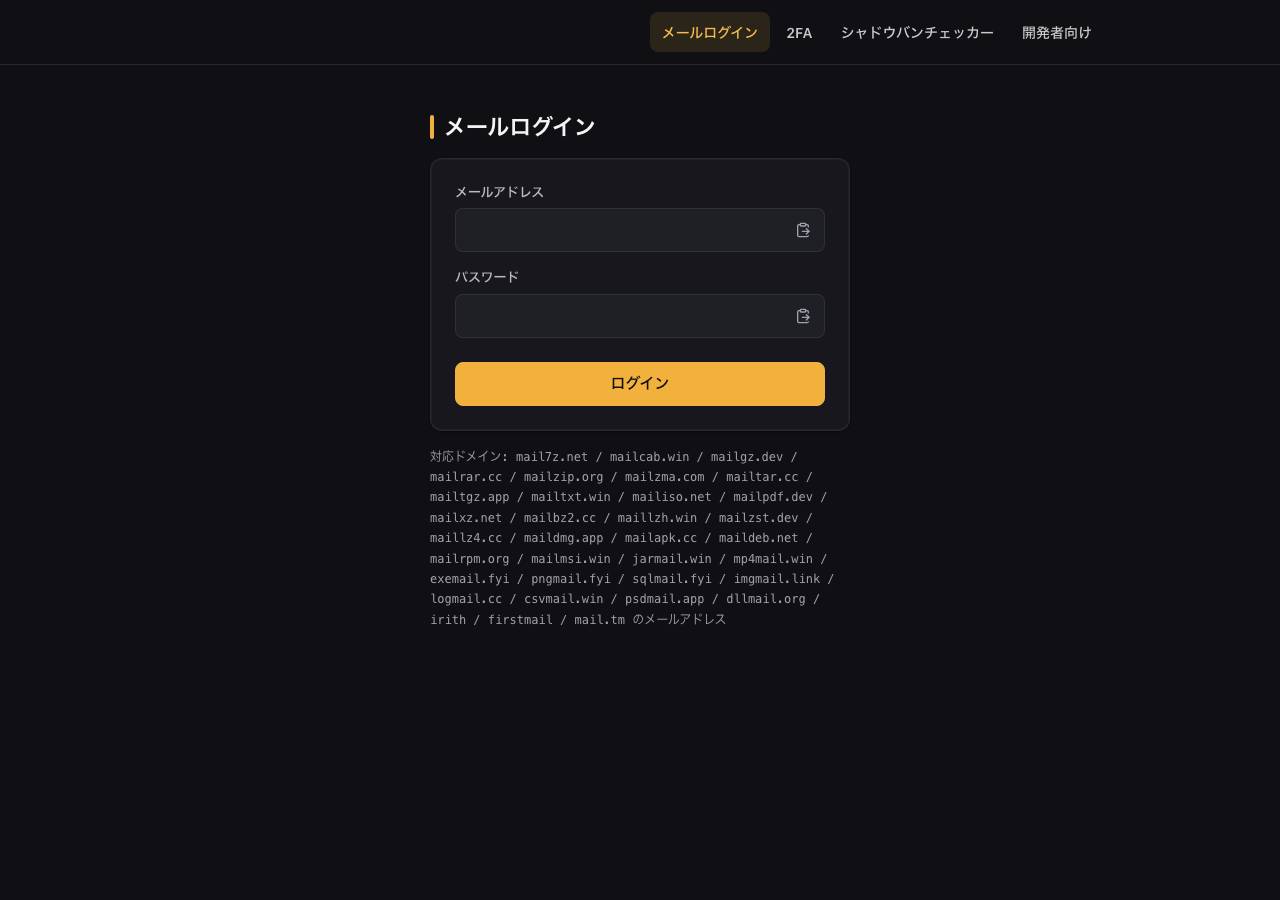
Same data as JSON: /api/zone/domain/imgmail.link. This page is not indexed by search engines and does not link to the site it describes.