irecovery.pro
Appeared in the .pro zone on Monday, October 26, 2026; by the end of that day the census found active website about saas & tech. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The page carries its own 'iRecovery' brand and does not pose as Apple. It markets a Russian-language Windows download that restores sanctions-removed apps (Sberbank, VK, T-Bank) to iPhones, and users must sign into their Apple ID inside the downloaded program. That is a plausible grey-market tool but also a classic credential-harvesting and malware delivery shape, so with a new domain, reg.ru DNS and Telegram-only contact the evidence is not decisive.
The page impersonates Apple by presenting itself as an official tool to recover missing App Store applications using Apple ID credentials. The title, branding, and workflow ("Войдите в Apple ID" / "Sign in to Apple ID") are designed to deceive users into entering their Apple ID login on a third-party domain, capturing credentials. The Russian-language presentation and Telegram operator contact links are typical phishing infrastructure.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 26, 2026
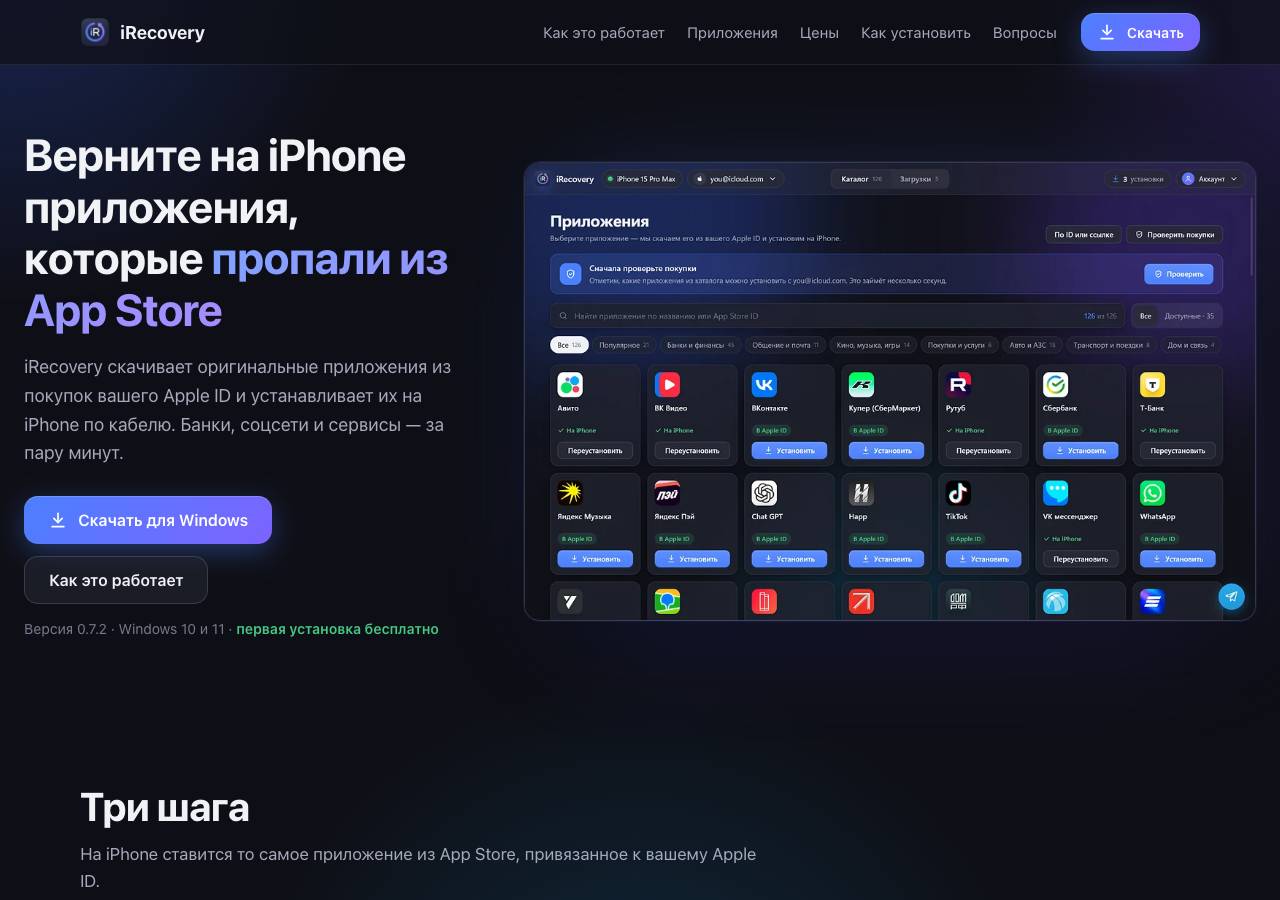
Same data as JSON: /api/zone/domain/irecovery.pro. This page is not indexed by search engines and does not link to the site it describes.