login-pls.top
Appeared in the .top zone on Friday, October 23, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
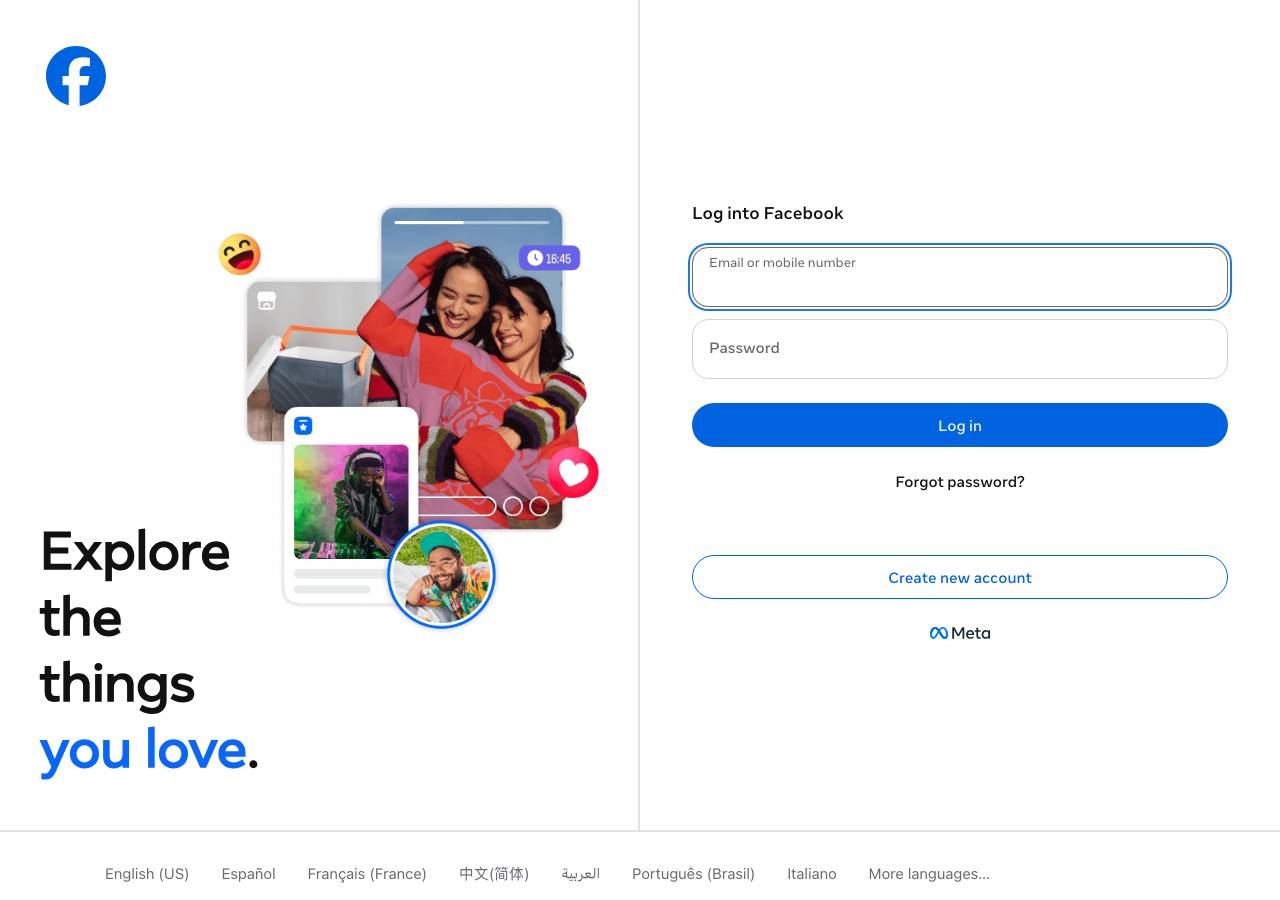
The domain serves no content of its own. It redirects to the real www.facebook.com, and the password form there posts to Facebook itself, so no credentials are captured. Still, a throwaway .top name built on lure words ('login-pls') behind Cloudflare that bounces visitors to a login page fits a cloaked phishing setup, where scanners get the genuine site, so it is not decisive either way.
The domain login-pls.top is a suspicious redirect URL that disguises its purpose with a generic, lure-word name ('login') and the .top TLD commonly used in phishing campaigns. It redirects to Facebook's legitimate login page, but the domain itself exists as an intermediary—a classic phishing infrastructure pattern. The attacker controls login-pls.top (Cloudflare nameservers) and channels traffic through it to the real Facebook site, allowing credential harvesting via tracking, form interception,
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Friday, October 23, 2026
Same data as JSON: /api/zone/domain/login-pls.top. This page is not indexed by search engines and does not link to the site it describes.