mega2kb.bid
Appeared in the .bid zone on Thursday, November 12, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
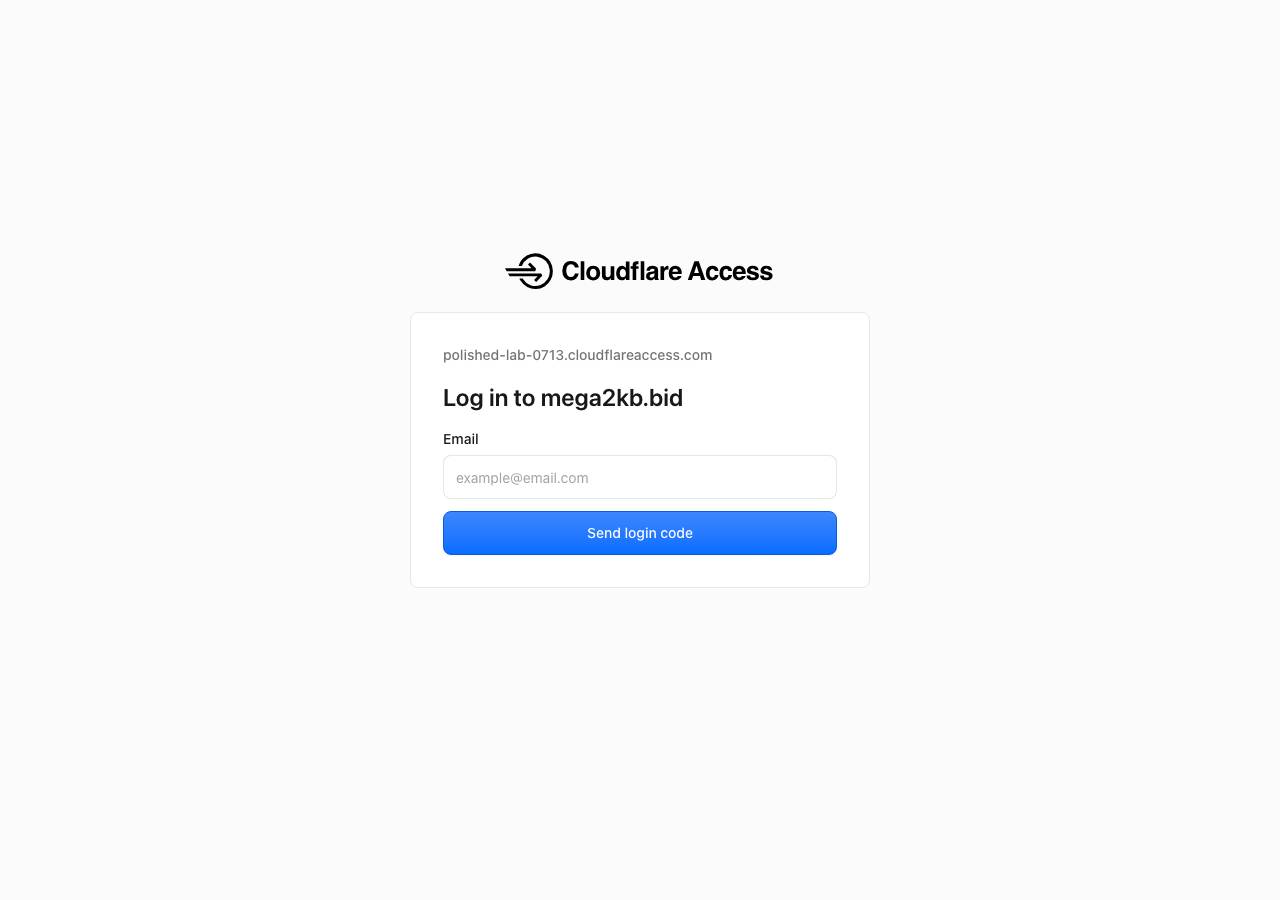
The redirect lands on a genuine Cloudflare Access (Zero Trust) login gate on a real cloudflareaccess.com tenant protecting mega2kb.bid, so it does not impersonate Cloudflare. The actual content is hidden behind the gate, and the throwaway 'mega2kb' name on a .bid TLD matches the naming pattern of darknet-market mirrors, but nothing visible confirms abuse.
The domain mega2kb.bid redirects to a polished-lab-0713.cloudflareaccess.com login page that impersonates Cloudflare Access. The page displays the Cloudflare Access logo and title, presents a login form for 'mega2kb.bid', and collects email credentials via a form posting to the attacker-controlled Cloudflare Access instance. This is a sealed-room phishing attack: a fake authentication gateway designed to harvest credentials for a domain the attacker controls.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, November 12, 2026
Same data as JSON: /api/zone/domain/mega2kb.bid. This page is not indexed by search engines and does not link to the site it describes.