microsoftsharepoint.top
Appeared in the .top zone on Friday, October 16, 2026; by the end of that day the census found server error. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
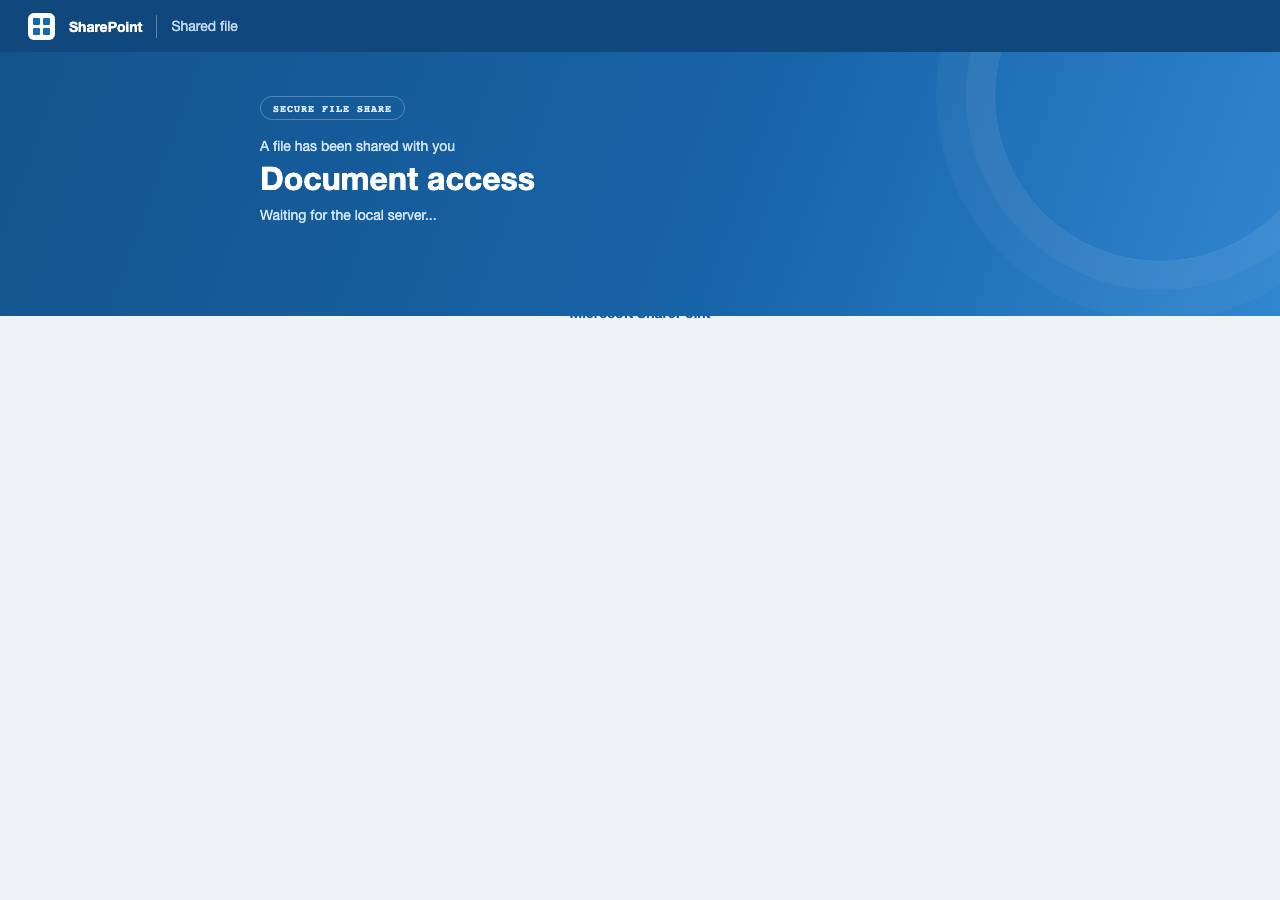
The domain microsoftsharepoint.top is not Microsoft's, and its rendered page uses SharePoint branding with a "A file has been shared with you / Document access / Secure file share" lure, the classic shared-document credential-phish template. The 502 behind Caddy and the 'Waiting for the local server' text suggest a phishing kit whose backend is not yet connected, which is why no login form appears yet.
Domain name microsoftsharepoint.top impersonates Microsoft's SharePoint product; the page displays Microsoft's SharePoint logo and branding with a 'Document access' prompt falsely claiming 'A file has been shared with you', a classic phishing lure designed to trick users into entering credentials. The 502 error masks what would likely be a login form, and the use of free DNS (dnsowl.com) and a typosquat domain (.top) with no legitimate purpose indicates malicious intent.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Friday, October 16, 2026
Same data as JSON: /api/zone/domain/microsoftsharepoint.top. This page is not indexed by search engines and does not link to the site it describes.