northwallet.app
Appeared in the .app zone on Tuesday, November 10, 2026; by the end of that day the census found active website about pharma health. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
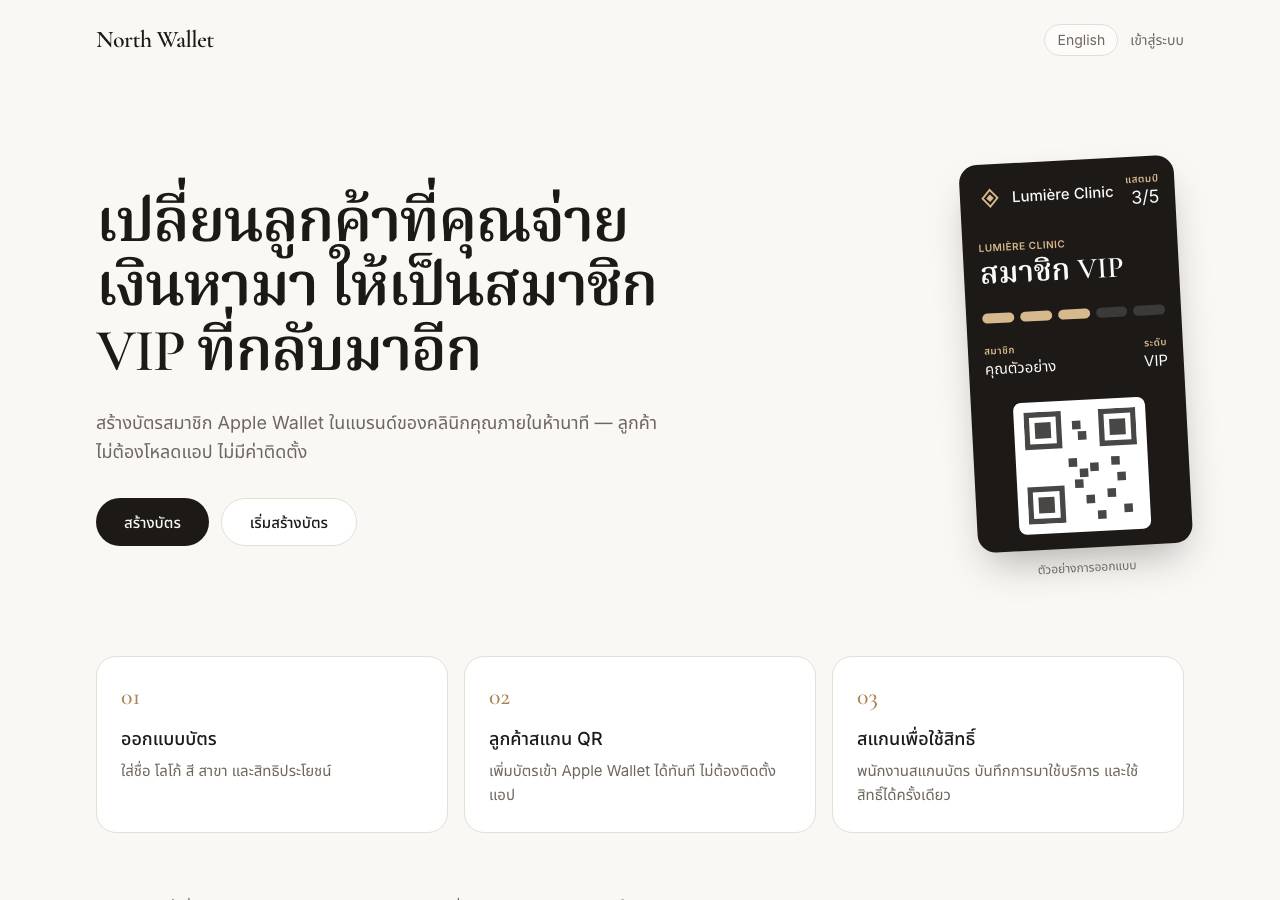
The page is a Thai SaaS landing page for 'North Wallet', its own brand, that lets clinics create loyalty passes for Apple Wallet. 'Apple Wallet' appears only as the integration target, with no Apple logo, account language or credential capture. The self-posting form is a Next.js server action carrying only a locale field, typical of a Vercel-hosted startup site rather than a phish.
The page title is 'North Wallet' but the content repeatedly impersonates Apple Wallet ('สร้างบัตรสมาชิก Apple Wallet' = 'Create Apple Wallet membership cards'), presenting Apple's product name and branding as if North Wallet IS Apple Wallet. The page has a login form posting to itself with hidden fields—the sealed-room phish pattern—designed to harvest credentials from visitors who believe they are accessing an Apple service.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, November 10, 2026
Same data as JSON: /api/zone/domain/northwallet.app. This page is not indexed by search engines and does not link to the site it describes.