p0stbank.org
Appeared in the .org zone on Tuesday, November 3, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
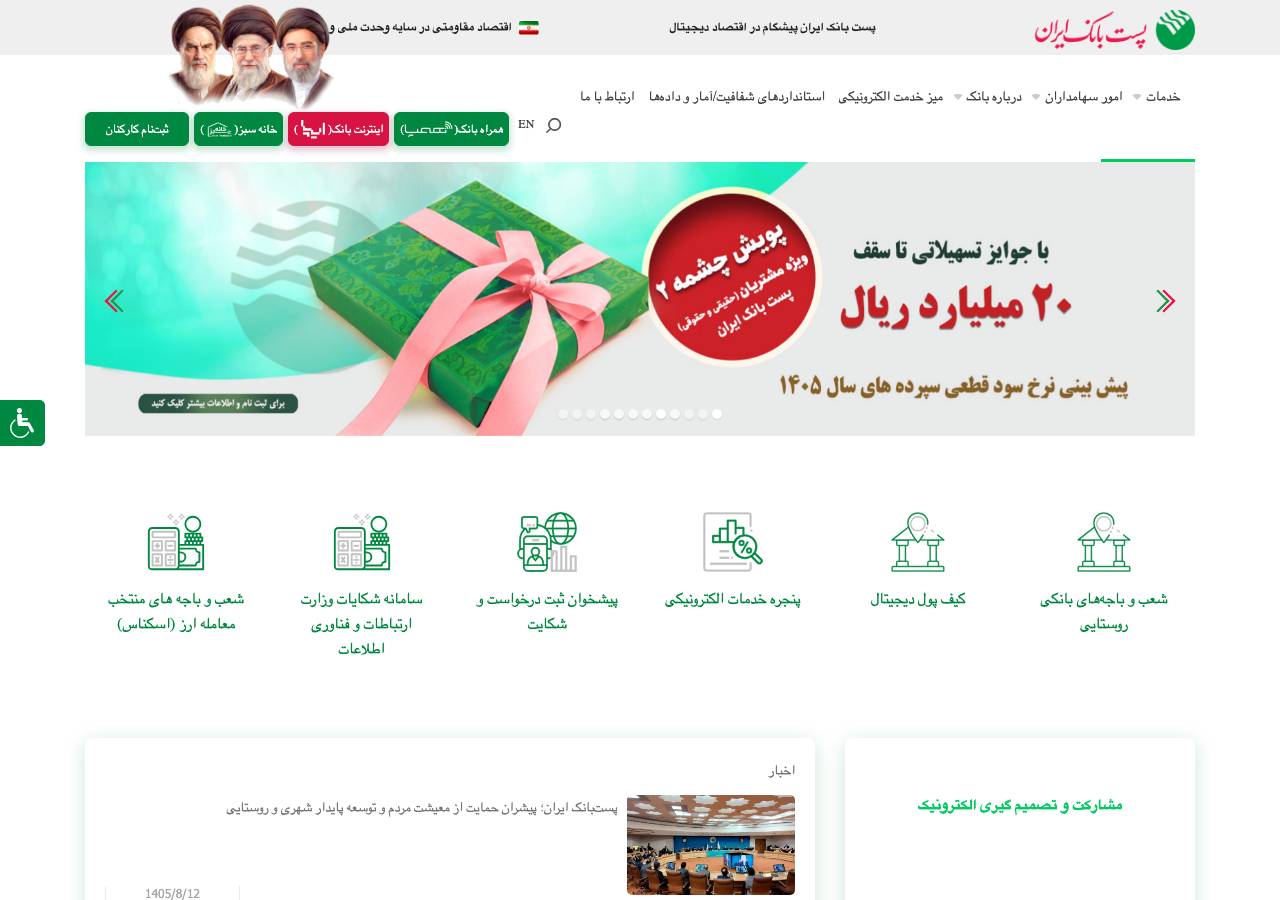
The leet typosquat p0stbank.org serves a full clone of Post Bank of Iran's homepage, with its logo and services, titled 'Post Bank - infrastructure test' and carrying a 'server active' test banner, on HostIran nameservers. All forms and banking links still point to the real postbank.ir and there is no credential capture yet, so this looks like phishing infrastructure being staged under a brand-squat rather than a live phish.
Domain p0stbank.org uses leet-speak substitution (0 for o) to impersonate Postbank Iran. The page displays Postbank's logo, Persian-language branding, and official design, with forms posting to www.postbank.ir. The combination of typosquat domain, brand impersonation via logo/layout, and credential-capture forms designed to deceive Persian-speaking users into submitting data to the attacker's infrastructure constitutes phishing.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, November 3, 2026
Same data as JSON: /api/zone/domain/p0stbank.org. This page is not indexed by search engines and does not link to the site it describes.