payment-service.top
Appeared in the .top zone on Sunday, September 20, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
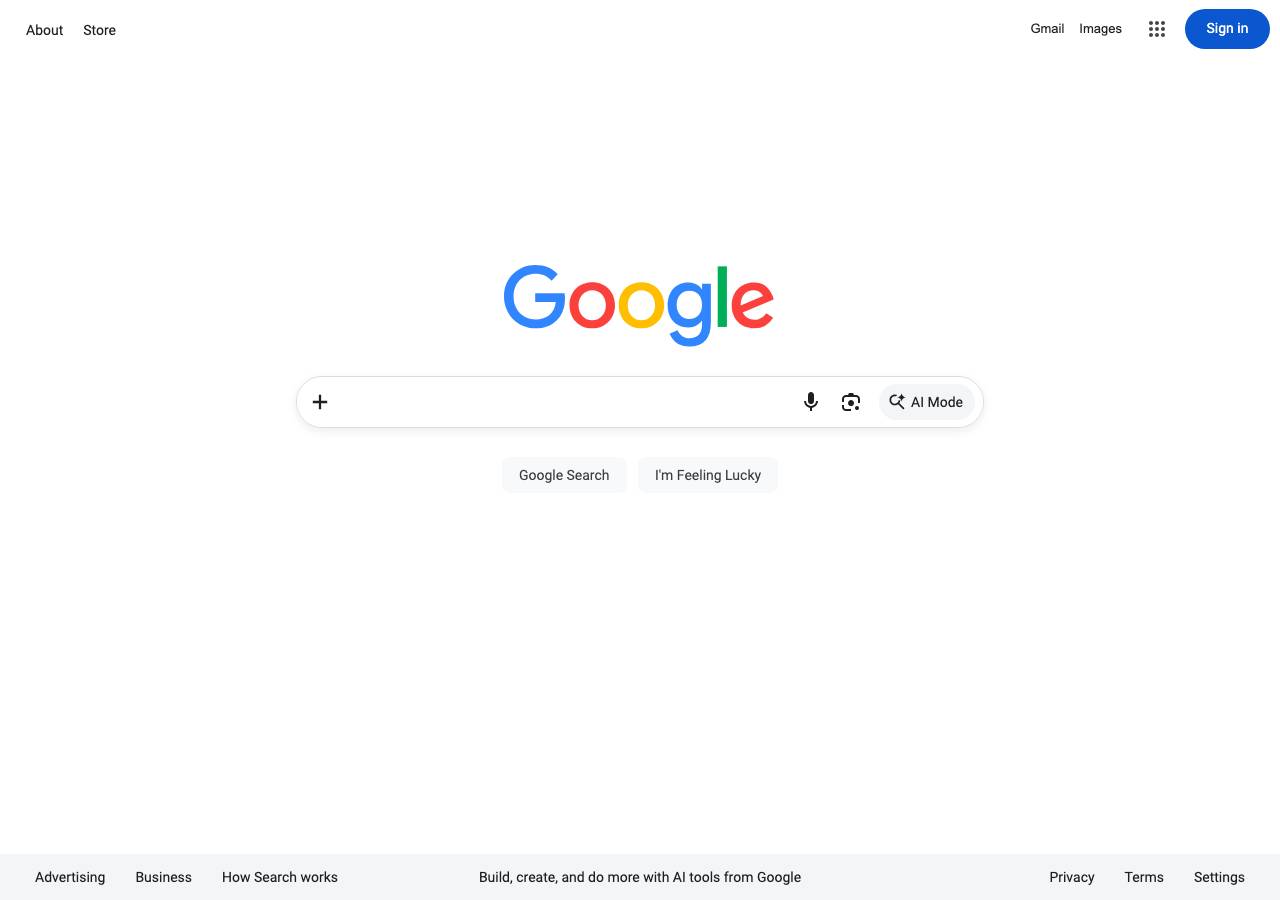
The name "payment-service.top" is a generic finance/payment lure on a cheap TLD behind Cloudflare nameservers, but it serves no content of its own — it simply redirects to www.google.com, a classic placeholder/cloaking posture for a domain being held before a payment-themed phishing or smishing campaign. The Google branding, sign-in and search form belong to the redirect destination, not to this domain, so there is no impersonation evidence yet.
Domain name 'payment-service.top' uses lure words (payment, service) combined with a .top TLD with poor reputation history, and redirects to Google's legitimate homepage. The redirect alone is not proof of phishing intent—it could be a misconfigured redirect or abandoned domain—but the deliberate choice of a deceptive domain name paired with redirection to a major brand's login ecosystem suggests potential credential-harvesting setup. The actual destination is Google's real page, not a phishing
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, September 20, 2026
Same data as JSON: /api/zone/domain/payment-service.top. This page is not indexed by search engines and does not link to the site it describes.