paypad.tech
Appeared in the .tech zone on Friday, October 2, 2026; by the end of that day the census found active website about crypto web3. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
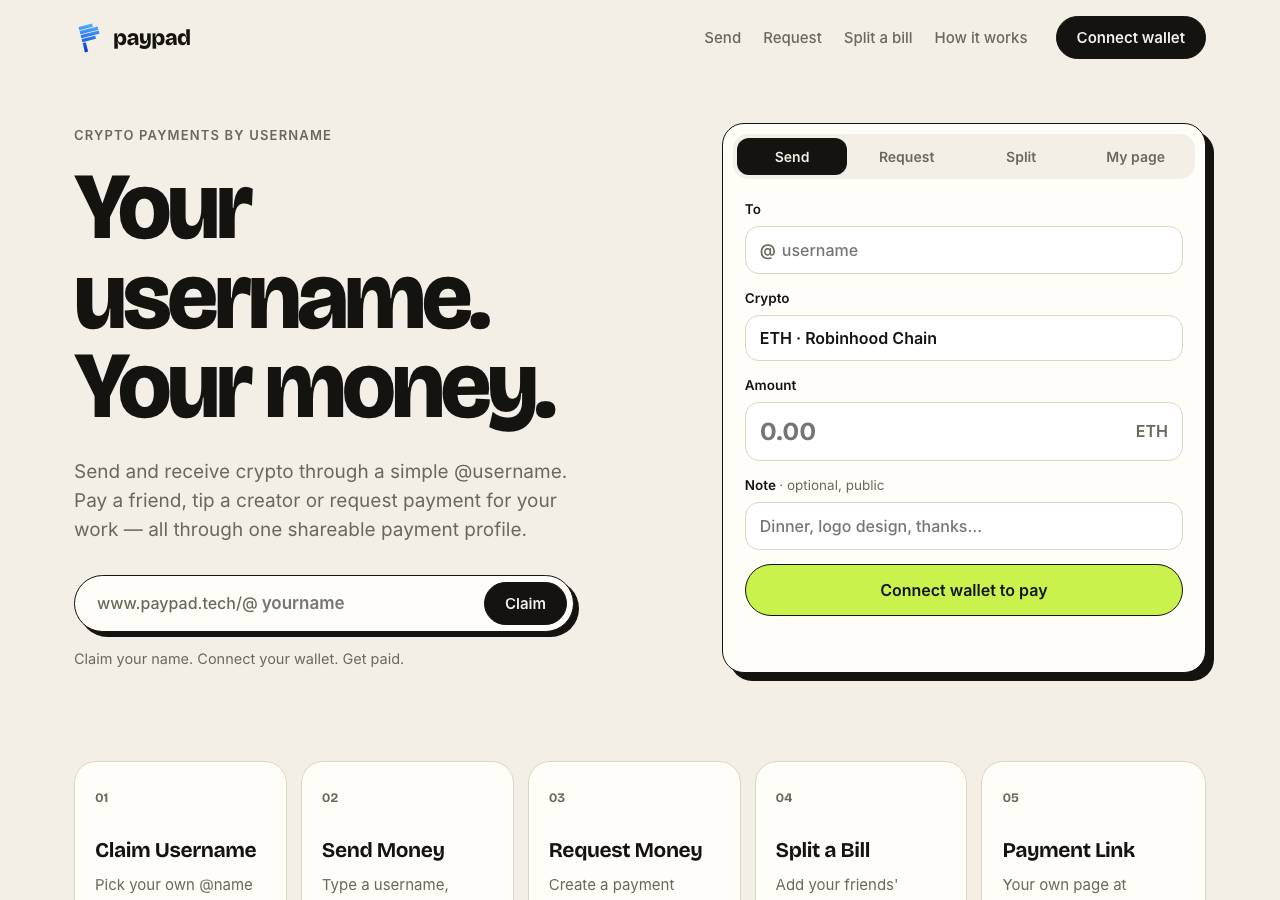
Model opinions
The page is a coherent crypto-payment-by-username product with its own 'paypad' logo and design. It uses no PayPal logo, colours or account language, and its only forms are GET username-claim fields posting to itself, with no password capture. The paypad≈paypal similarity is a generic pay+pad compound, though the new-domain 'Connect wallet' flow carries some unverified drainer risk.
Domain name 'paypad.tech' is a typosquat of PayPal designed to deceive. The page displays a functional crypto payment form ('Send', 'Request', 'Split') posting to itself with no legitimate wallet integration, mimicking PayPal's brand identity and payment language ('Send and receive', 'Request payment') to trick users into entering credentials or connecting wallets. The sealed-room form shape (self-posting with no offsite links) and deliberate brand confusion confirm phishing intent.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Friday, October 2, 2026
Same data as JSON: /api/zone/domain/paypad.tech. This page is not indexed by search engines and does not link to the site it describes.