pngmail.fyi
Appeared in the .fyi zone on Thursday, October 15, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
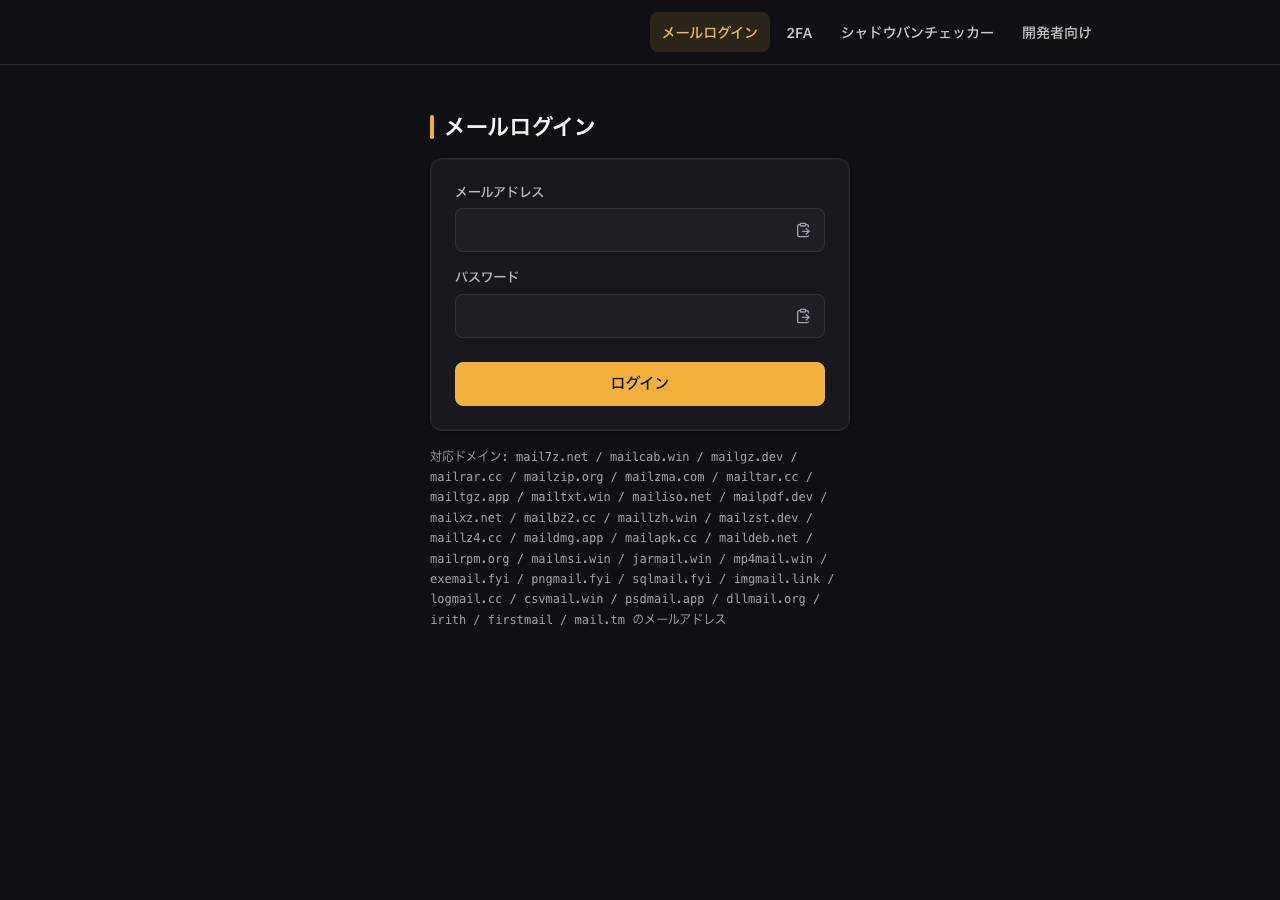
The 'gmail' hit is a false positive: the name parses as png+mail, and the domain belongs to a set of file-extension-themed mailbox domains (exemail.fyi, sqlmail.fyi, dllmail.org…). Getotp.cc lists pngmail.fyi among the domains its own branded Japanese mail-login, 2FA and shadowban-checker tool supports, with no impersonation of Google or anyone else. The bulk/throwaway-mailbox service hints at account farming but shows no phishing or fraud.
pngmail.fyi is a typosquat domain containing 'mail' that redirects to getotp.cc, a credential harvesting page styled as an email login form. The page explicitly lists pngmail.fyi among dozens of lookalike mail domains it 'supports,' and the form posts credentials to getotp.cc—a classic sealed-room phishing infrastructure pattern designed to collect email and password from users deceived by the typosquat name.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 15, 2026
Same data as JSON: /api/zone/domain/pngmail.fyi. This page is not indexed by search engines and does not link to the site it describes.