popofashnellele.click
Appeared in the .click zone on Monday, October 26, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The domain serves no content of its own and simply redirects to the real www.facebook.com, so the login form posts to Facebook itself and is not impersonation. However, a fresh gibberish .click name (Eranet registrar, behind Cloudflare) bouncing visitors to Facebook matches the cloaking pattern phishing kits use to hide from scanners, so the risk is real but unproven.
The domain popofashnellele.click redirects to Facebook's login page, creating a deceptive entry point. The typosquat domain name has no legitimate purpose other than to trick users into visiting Facebook via an attacker-controlled redirect, a classic phishing infrastructure pattern designed to harvest credentials or track login attempts through an intermediary.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 26, 2026
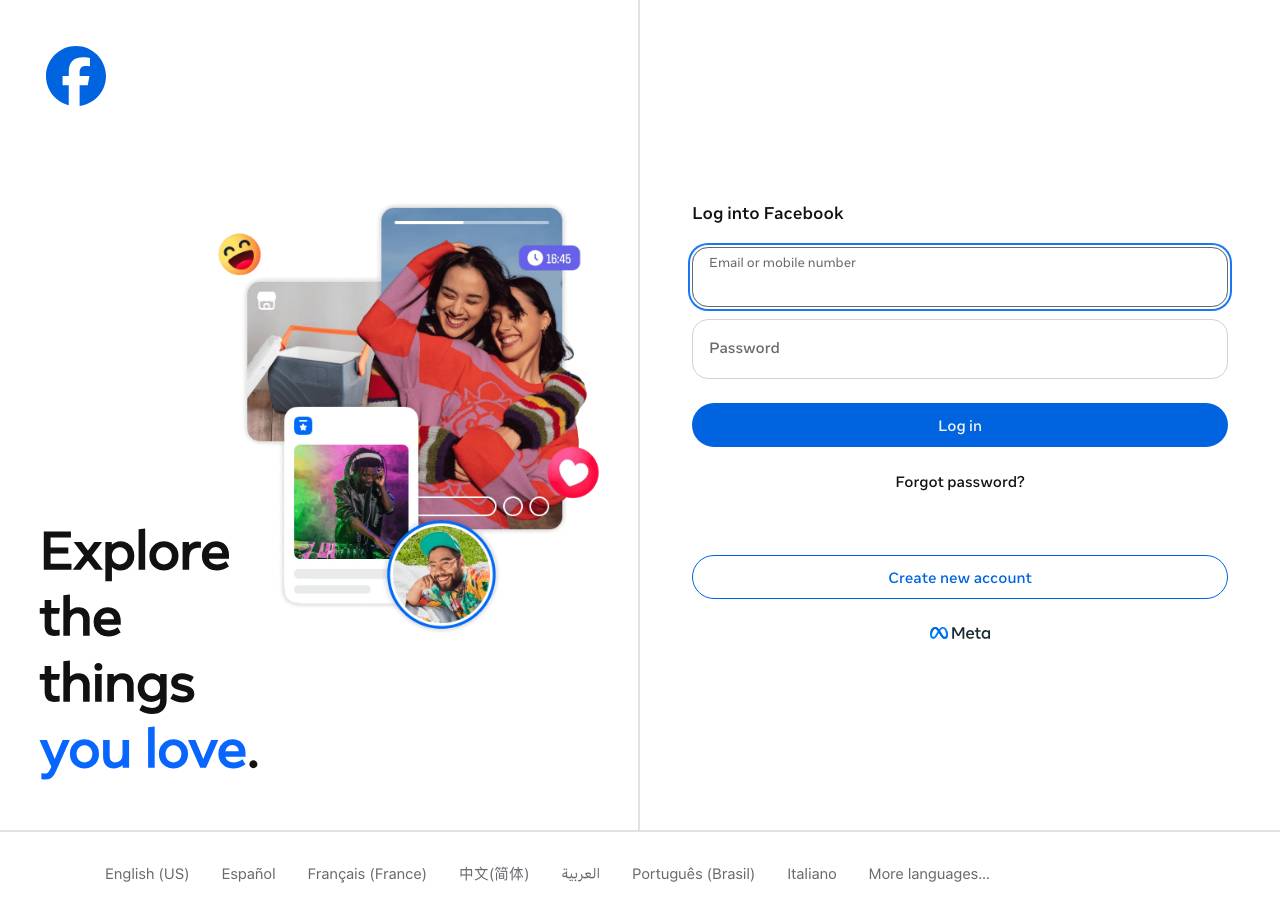
Same data as JSON: /api/zone/domain/popofashnellele.click. This page is not indexed by search engines and does not link to the site it describes.