postal.top
Appeared in the .top zone on Wednesday, September 30, 2026; by the end of that day the census found boilerplate page. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The domain 'postal.top' is a near-homophone of PostNL (major Dutch postal/logistics operator), and the page title 'Verification' with a hCaptcha challenge suggests credential or account verification phishing setup. However, the page currently shows only a CAPTCHA with no login form visible, making it a work-in-progress rather than an active phishing page; the lack of visible form fields and the boilerplate state prevent a definitive phishing verdict.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, September 30, 2026
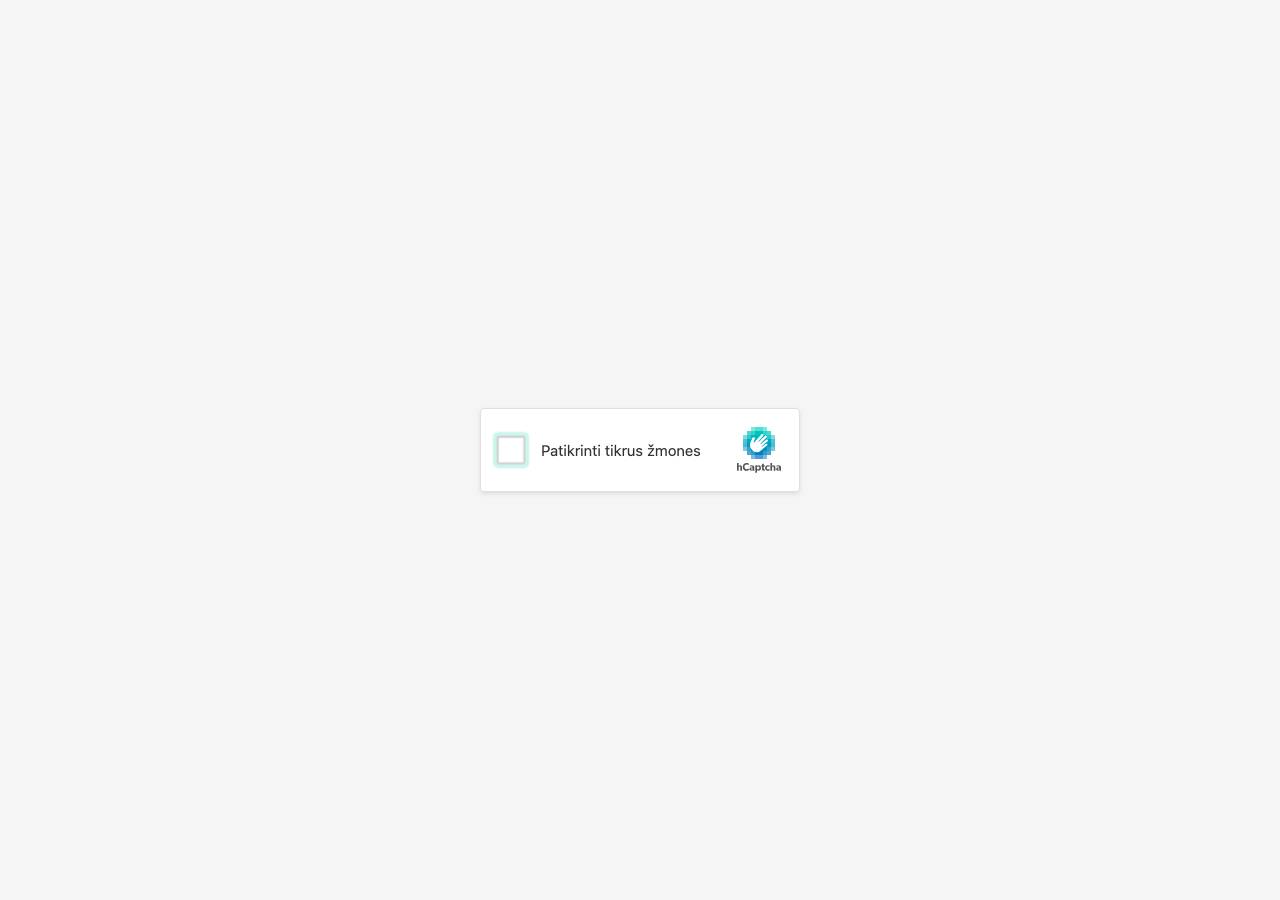
Same data as JSON: /api/zone/domain/postal.top. This page is not indexed by search engines and does not link to the site it describes.