receivableslinkedin.com
Appeared in the .com zone on Wednesday, November 11, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The name joins the distinctive brand 'linkedin' with the invoice/finance term 'receivables', which suggests BEC or invoice-fraud staging. It is registered through budget Spaceship nameservers rather than LinkedIn's own infrastructure, and it currently just redirects to the real www.linkedin.com, the usual cover for a brand-squat held in reserve, with no phishing page served yet.
Domain name 'receivableslinkedin.com' is a typosquat designed to deceive users into believing they are visiting LinkedIn. The domain redirects to LinkedIn's legitimate login page, creating a classic phishing setup where victims enter credentials at a deceptive URL before being sent to the real site. The use of Spaceship nameservers and the redirect-to-impersonation pattern are hallmarks of phishing infrastructure.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, November 11, 2026
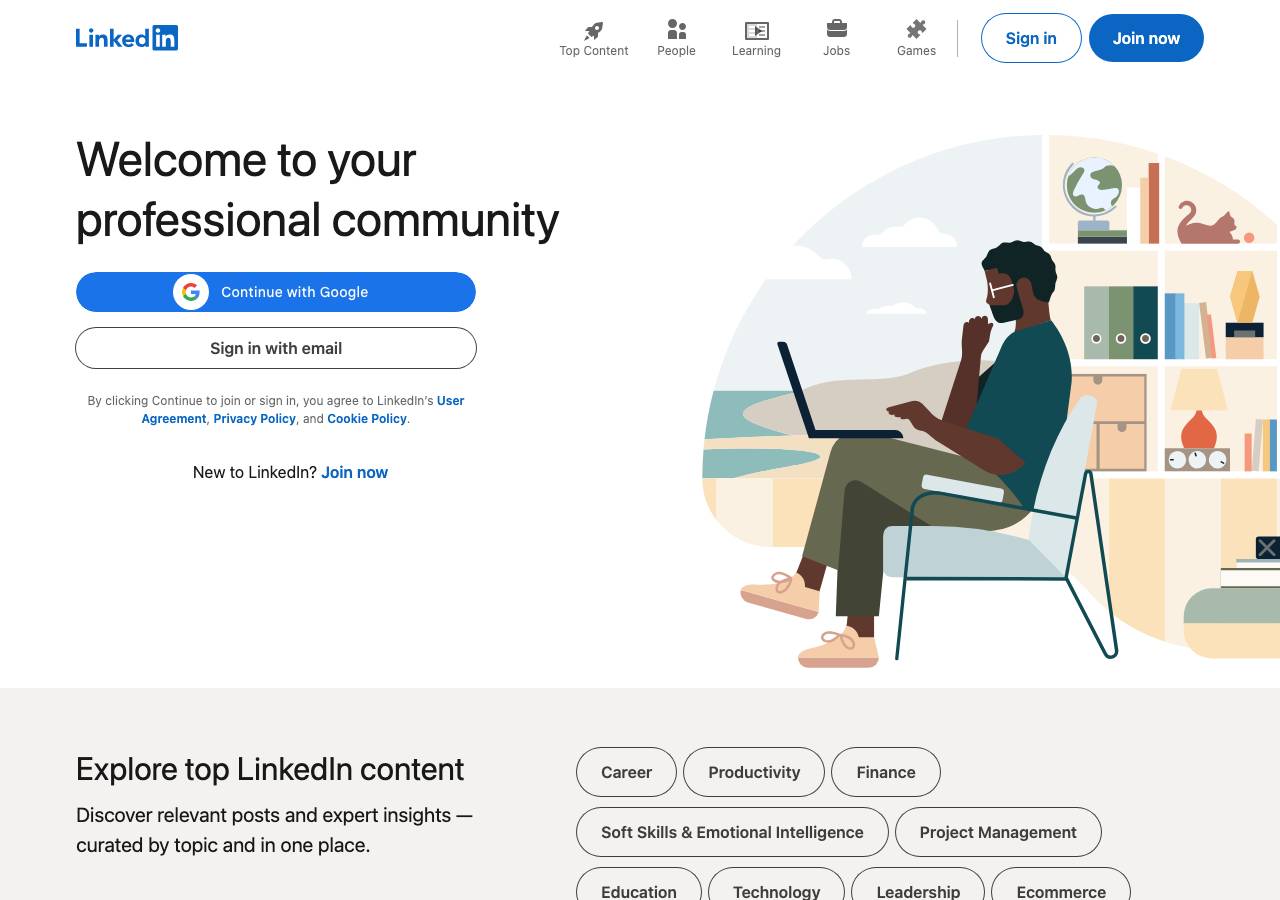
Same data as JSON: /api/zone/domain/receivableslinkedin.com. This page is not indexed by search engines and does not link to the site it describes.