retested.click
Appeared in the .click zone on Tuesday, September 15, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
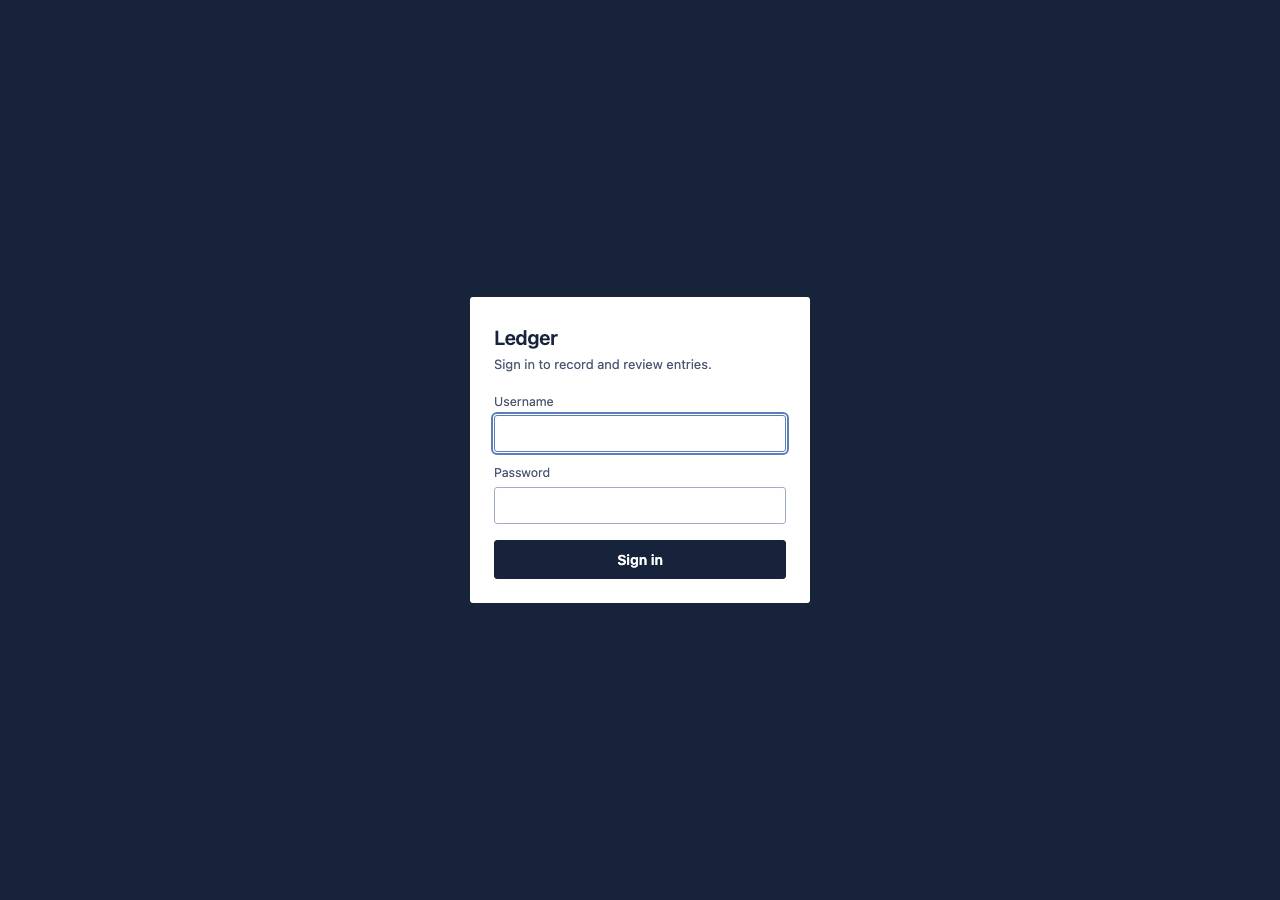
The 'Ledger' word here is generic bookkeeping language ('Sign in to record and review entries') with no Ledger Live branding, logo, or seed-phrase request, so the brand-in-title hit is a false positive; what remains is a bare self-posting username/password panel with zero other content on a brand-new throwaway .click domain, which is unexplained but not evidently impersonating anyone.
The page at retested.click/login.php impersonates Ledger with the title 'Sign in Ledger' and prompts users to 'Sign in to record and review entries.' The password form posts to itself with no legitimate offsite links, creating a credential-capture trap. The domain name does not contain 'ledger' but the page content clearly pretends to be Ledger's login portal to harvest credentials.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, September 15, 2026
Same data as JSON: /api/zone/domain/retested.click. This page is not indexed by search engines and does not link to the site it describes.