royalmail.work
Appeared in the .work zone on Saturday, September 19, 2026; by the end of that day the census found active website about e-commerce & retail. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
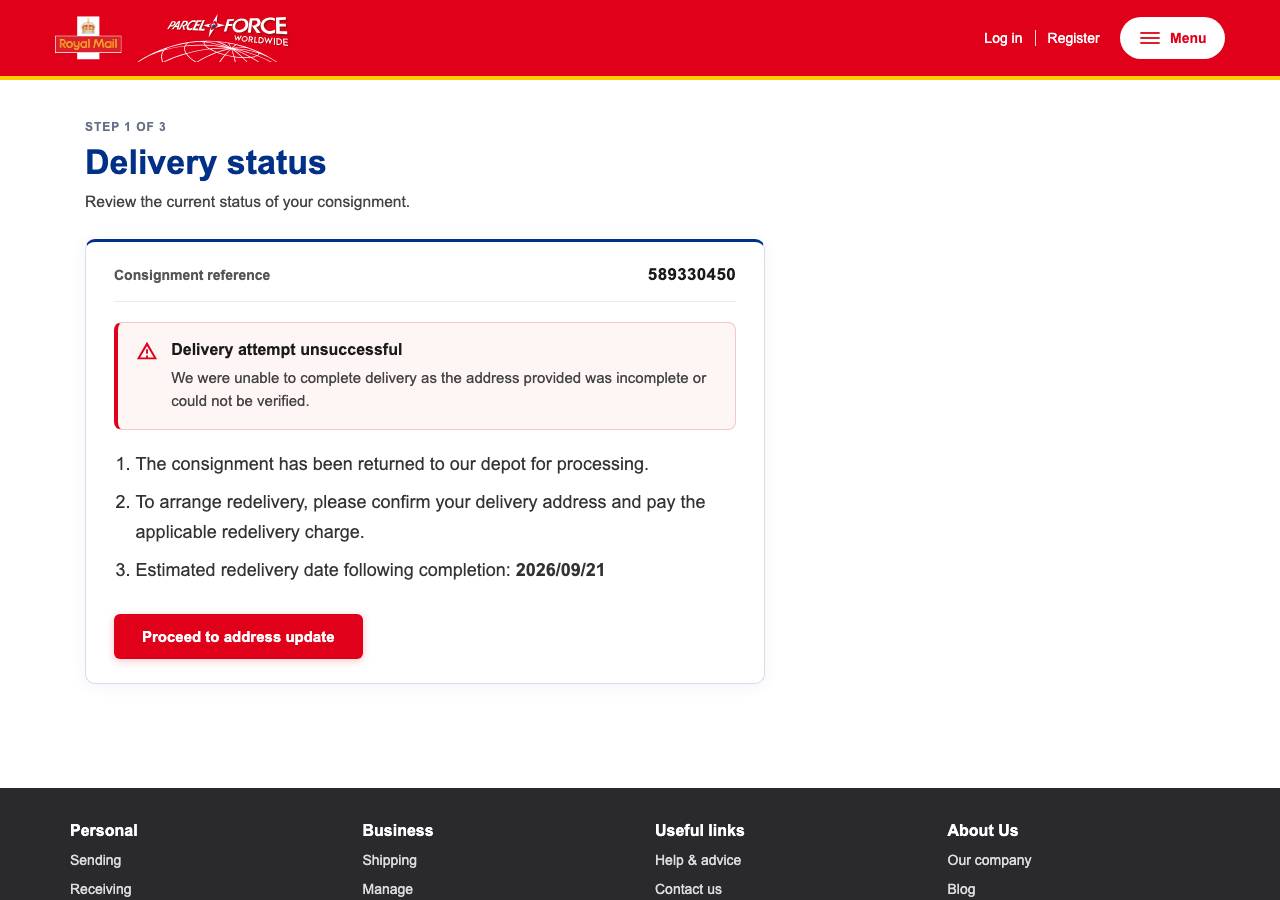
Domain royalmail.work hosts a cloned Parcelforce/Royal Mail 'Track and Trace' page with failed-delivery pretext, collecting full name, address, email and card number/expiry/CVV for a token £0.23 redelivery fee; forms post to self with no offsite links — classic parcel-redelivery card-harvesting phish.
Domain royalmail.work impersonates Royal Mail/Parcelforce with authentic branding (logo, page title 'Parcelforce Worldwide', red header). The page uses a fake failed-delivery pretext to social-engineer users into a three-step form that captures full name, address, email, phone, and complete card details (number, expiry, CVV, cardholder name) — all posted to self with no offsite links, the sealed-room phishing pattern. The £0.23 redelivery charge is a psychological manipulation tactic to appear l
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, September 19, 2026
Same data as JSON: /api/zone/domain/royalmail.work. This page is not indexed by search engines and does not link to the site it describes.