sessionapi-whatsapp.com
Appeared in the .com zone on Monday, October 19, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
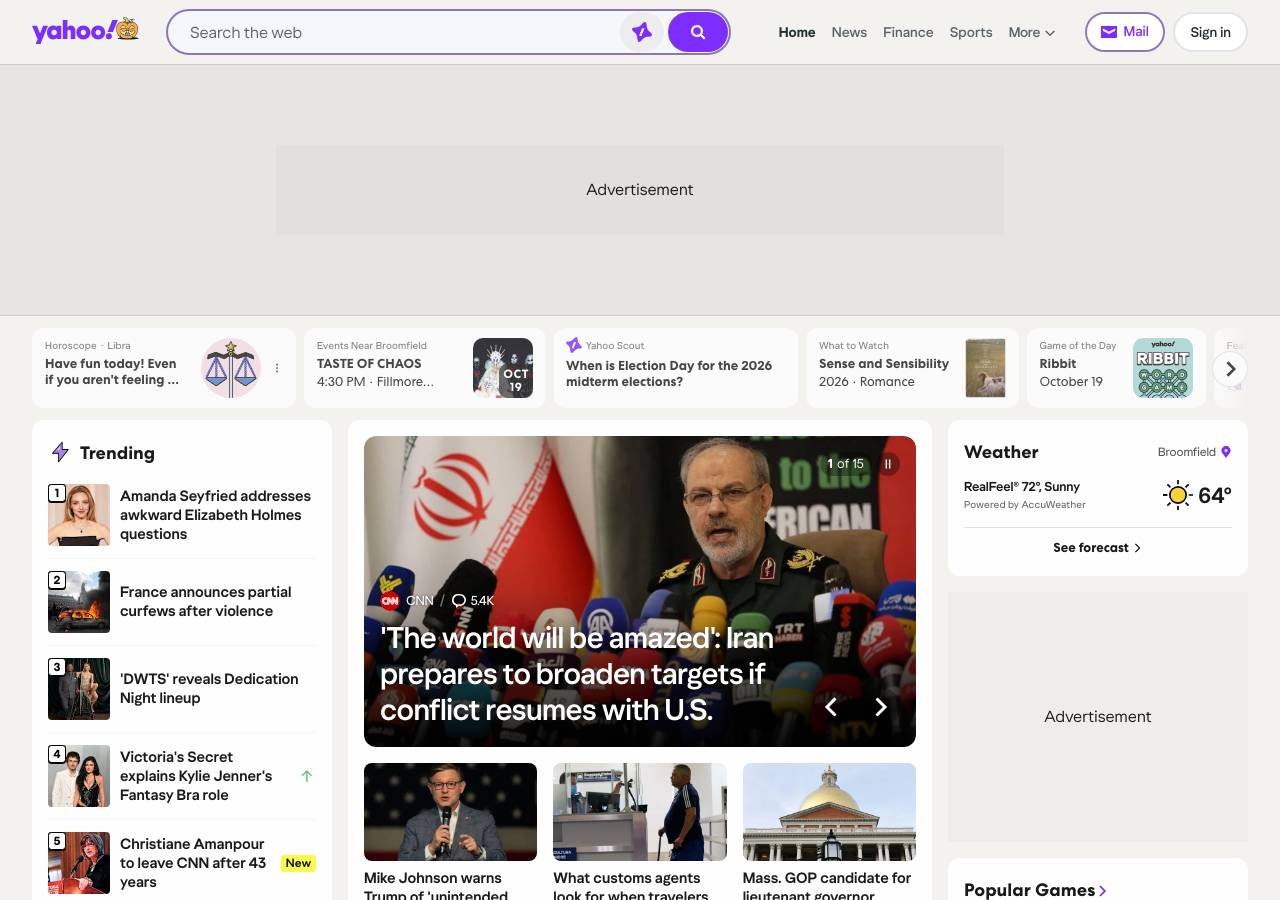
The name is built on the distinctive WhatsApp brand plus 'sessionapi', which suggests unofficial WhatsApp session/API tooling or a session-hijack lure, and the domain is not WhatsApp's own. It serves no content of its own and redirects to the unrelated www.yahoo.com, a common cloaking pattern. It uses xundns nameservers, so it reads as a brand-squat held for later deceptive use.
Domain name 'sessionapi-whatsapp.com' impersonates WhatsApp's brand to create false authority, then redirects to an unrelated site (Yahoo). The domain name itself is a typosquat designed to deceive users seeking WhatsApp API documentation or session management; the redirect to Yahoo suggests either SEO manipulation, click fraud, or infrastructure for a redirect-based scam campaign.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 19, 2026
Same data as JSON: /api/zone/domain/sessionapi-whatsapp.com. This page is not indexed by search engines and does not link to the site it describes.