simplecash.bid
Appeared in the .bid zone on Sunday, September 20, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
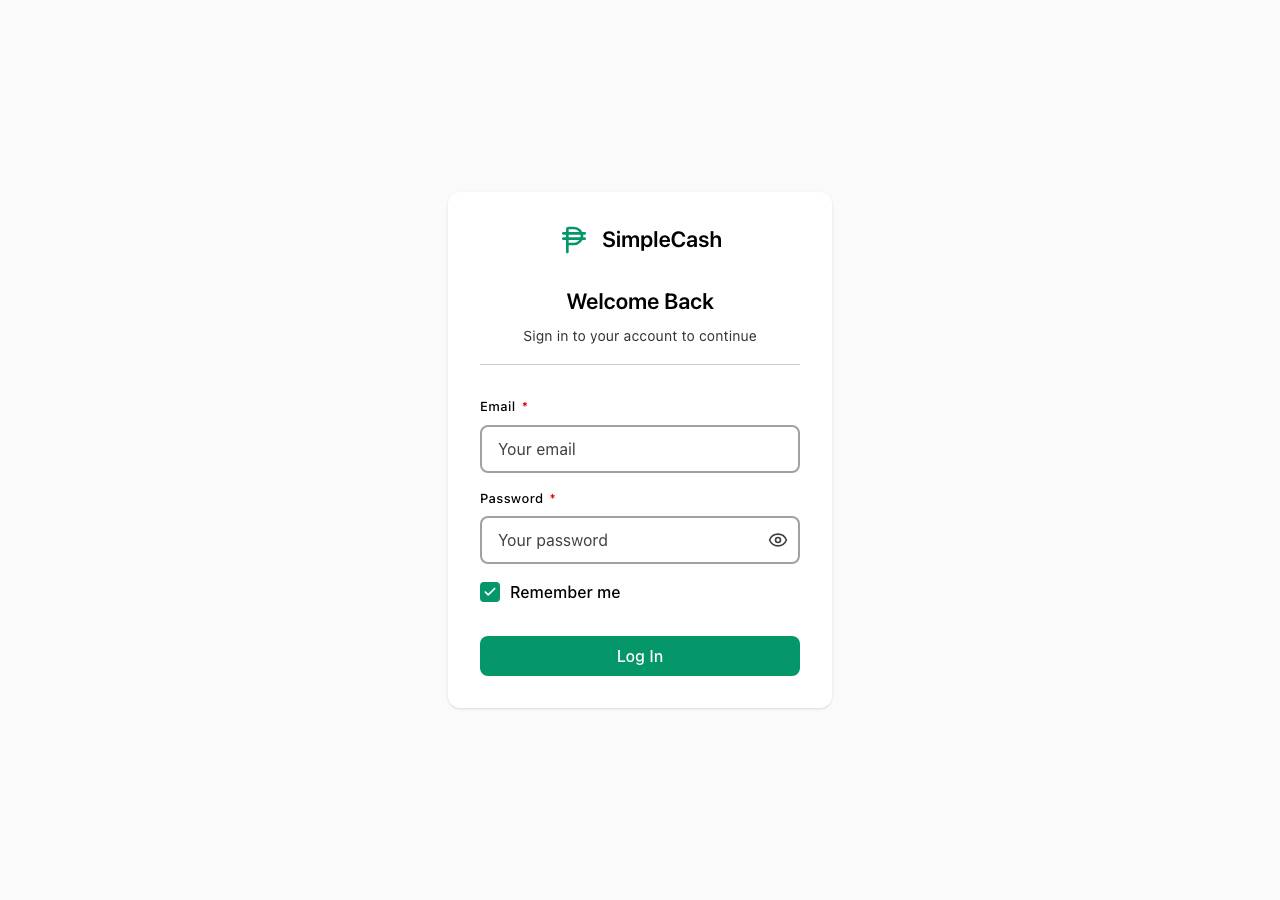
Brand-new .bid domain behind Cloudflare serving nothing but a self-posting email/password form branded "SimpleCash" with a peso (₱) logo — the sealed-room login shape with zero other content or offsite links, consistent with credential harvesting aimed at Philippine cash-loan app users, but no verified organisation is being imitated so impersonation cannot be confirmed yet.
The domain simplecash.bid displays a login form titled 'SimpleCash' with email and password fields that posts to itself with no offsite links—the classic sealed-room phishing pattern. The .bid TLD and newly registered domain combined with a credential-harvesting form impersonating a financial service create strong evidence of phishing infrastructure.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, September 20, 2026
Same data as JSON: /api/zone/domain/simplecash.bid. This page is not indexed by search engines and does not link to the site it describes.