streamsm.top
Appeared in the .top zone on Saturday, October 17, 2026; by the end of that day the census found active website about blogs & personal. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
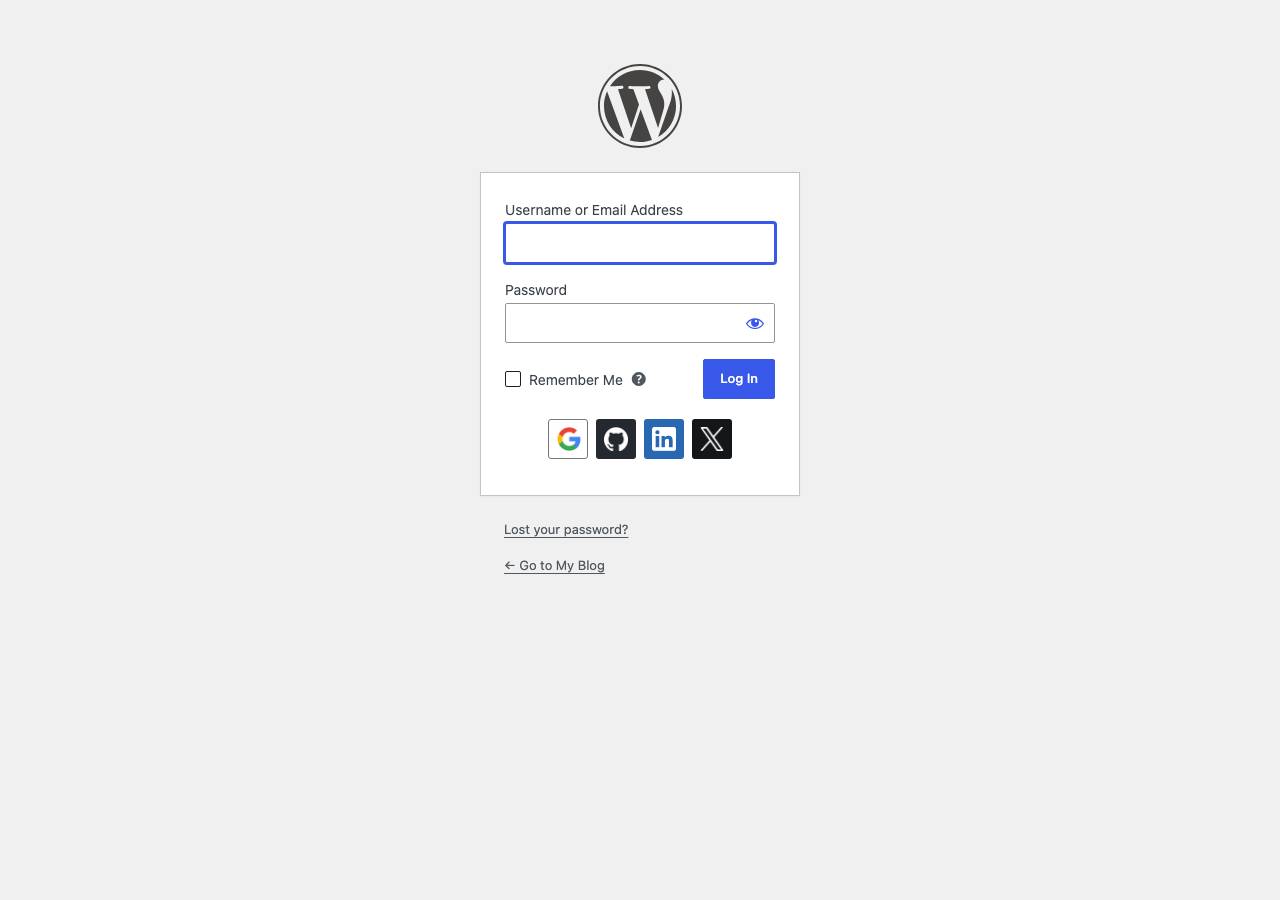
This is the stock WordPress wp-login.php page of a fresh install: the default "My Blog" site title, social-login plugin buttons, and a form posting to its own WordPress backend. That is the site's own admin login, not an impersonation of WordPress, and the generic name "streamsm.top" carries no brand deception.
The page displays the WordPress logo and login form titled 'Log In ‹ My Blog — WordPress' on domain streamsm.top, impersonating WordPress to capture credentials. The password form posts to itself with no legitimate WordPress infrastructure links, matching the 'sealed-room' phishing pattern where captured credentials are sent to the attacker's server rather than WordPress.org.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, October 17, 2026
Same data as JSON: /api/zone/domain/streamsm.top. This page is not indexed by search engines and does not link to the site it describes.