tango-stack.top
Appeared in the .top zone on Sunday, September 20, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
Generic non-brand name on a cheap .top behind Cloudflare that serves no content of its own and 302s straight to a genuine amazon.com product listing — the shape of a throwaway affiliate/traffic-laundering redirector rather than impersonation; the Amazon branding shown belongs to the real destination, so there is no phishing evidence, but the disposable domain-to-Amazon redirect pattern is not legitimate content either.
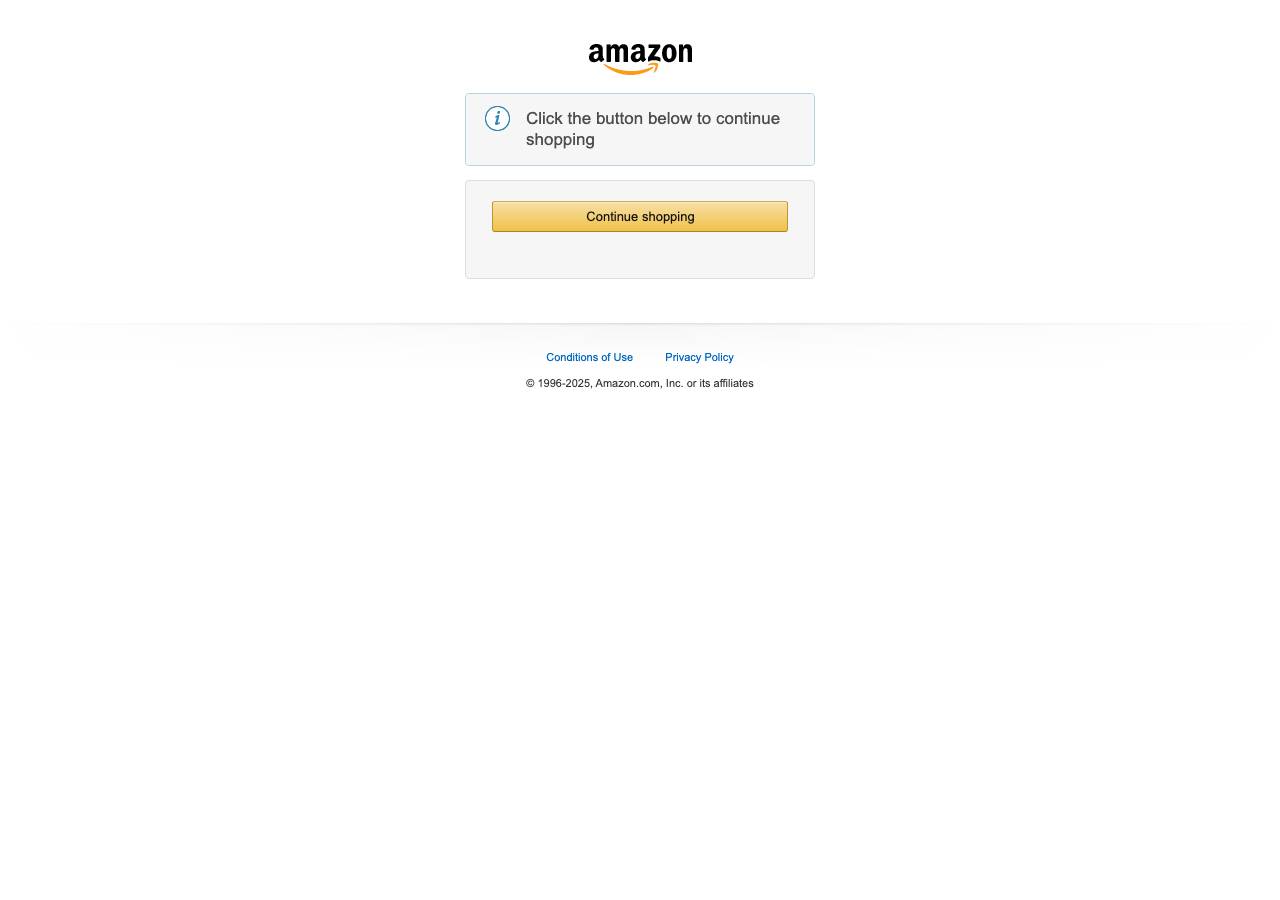
The domain tango-stack.top redirects to Amazon's real site but serves an interstitial page bearing Amazon's logo with a 'Continue shopping' button that appears designed to harvest credentials or inject tracking. The domain name itself is generic and unrelated to Amazon, yet it impersonates Amazon's branding on its own page before redirecting; this is a classic phishing redirect-interstitial pattern to capture user data or inject affiliate/malware parameters.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Sunday, September 20, 2026
Same data as JSON: /api/zone/domain/tango-stack.top. This page is not indexed by search engines and does not link to the site it describes.