teleg-mvote.click
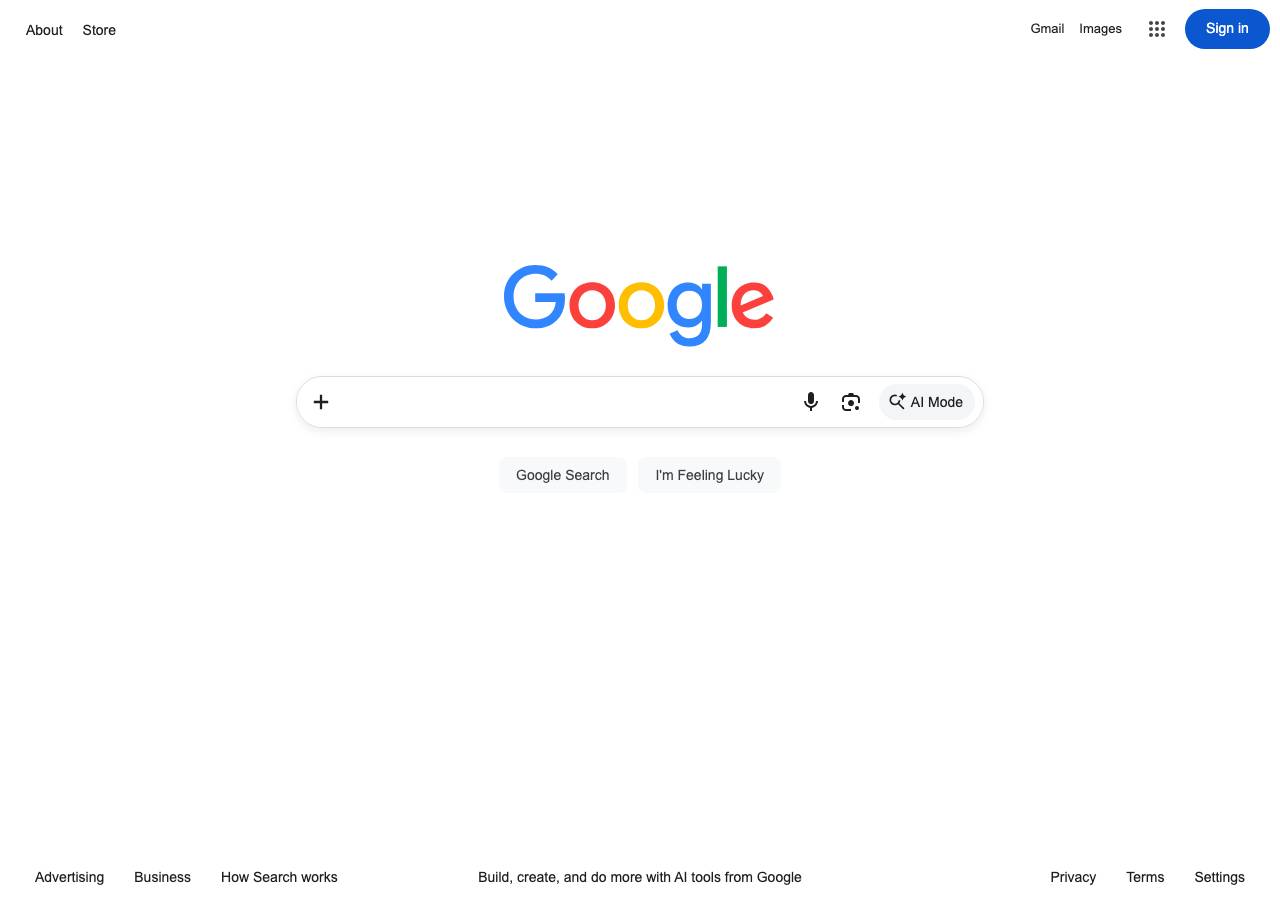
Appeared in the .click zone on Saturday, October 3, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
The name 'teleg-mvote' fits the known Telegram 'vote for my friend' account-takeover lure, and it sits on a cheap .click TLD with Cloudflare DNS. Bouncing visitors to google.com is a common cloaking move that hides the phishing page from scanners and non-targeted traffic. The Google content is the redirect destination, not impersonation by this domain.
The domain teleg-mvote.click is a typosquat (Telegram + voting theme) that unconditionally redirects to www.google.com. The redirect-to-legitimate-site pattern with a deceptive domain name is a classic abuse tactic: the domain's only plausible purpose is to deceive visitors into thinking they are accessing a Telegram voting service, not to provide legitimate functionality. No phishing form is hosted on the attacker's domain itself.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, October 3, 2026
Same data as JSON: /api/zone/domain/teleg-mvote.click. This page is not indexed by search engines and does not link to the site it describes.