teleg-vote-x.click
Appeared in the .click zone on Tuesday, October 6, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
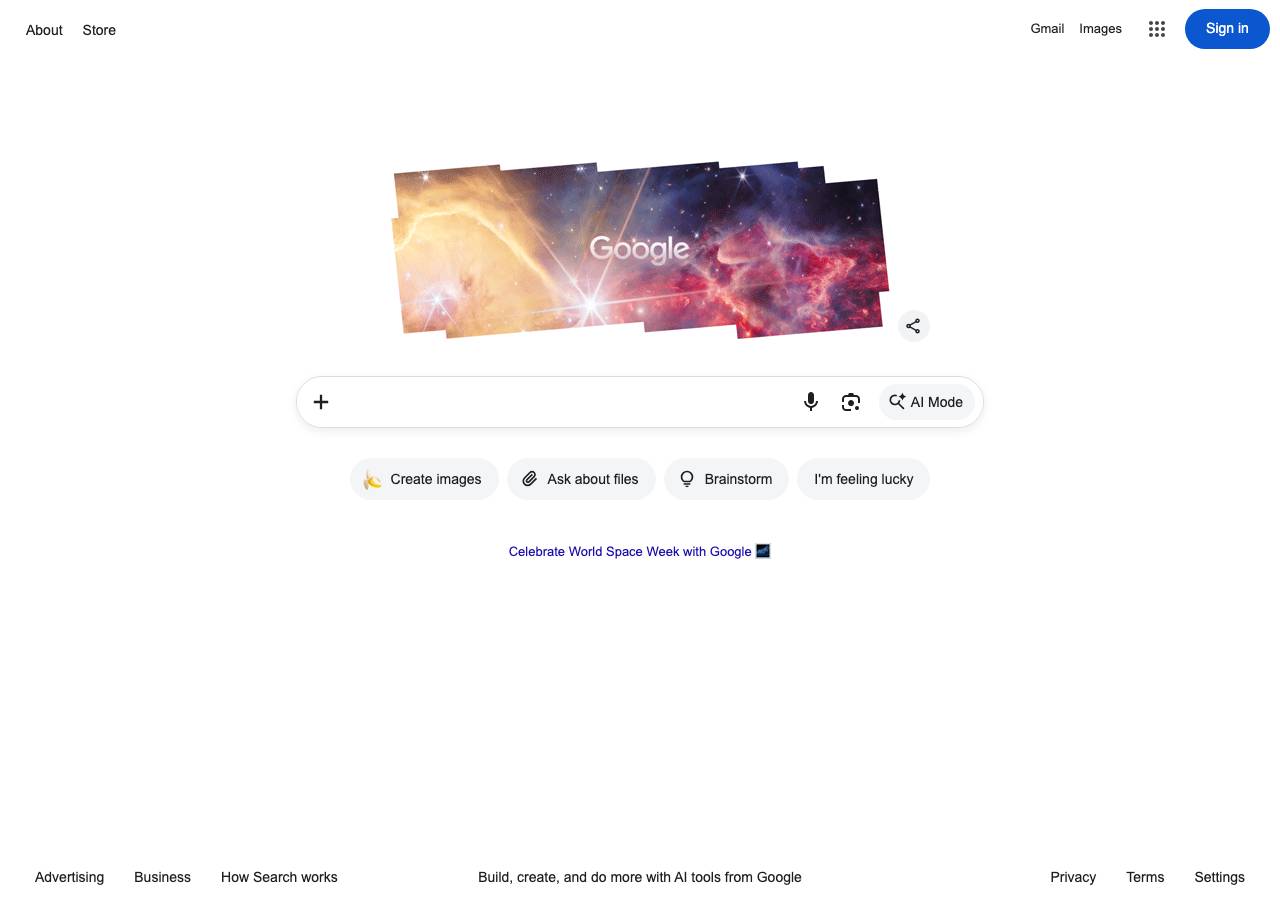
The name 'teleg-vote-x' matches the known Telegram 'vote for my contestant' account-takeover phishing pattern, registered on a cheap .click TLD behind Cloudflare. It currently redirects offsite to google.com, a common cloaking step that hides the lure from scanners. The Google page and form are the destination's own and are not evidence against this domain.
The domain teleg-vote-x.click is a clear typosquat/redirect squat with no legitimate purpose. It combines 'teleg' (Telegram typo), 'vote', and 'x' in a suspicious name, then redirects to Google's legitimate homepage—a classic bait-and-switch tactic to disguise the domain's true intent (likely to appear legitimate in phishing or scam traffic chains) while the destination page itself is authentic Google. The domain's only plausible purpose is deception through misdirection.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Tuesday, October 6, 2026
Same data as JSON: /api/zone/domain/teleg-vote-x.click. This page is not indexed by search engines and does not link to the site it describes.