tiempijama.fun
Appeared in the .fun zone on Wednesday, November 4, 2026; by the end of that day the census found active website about blogs & personal. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
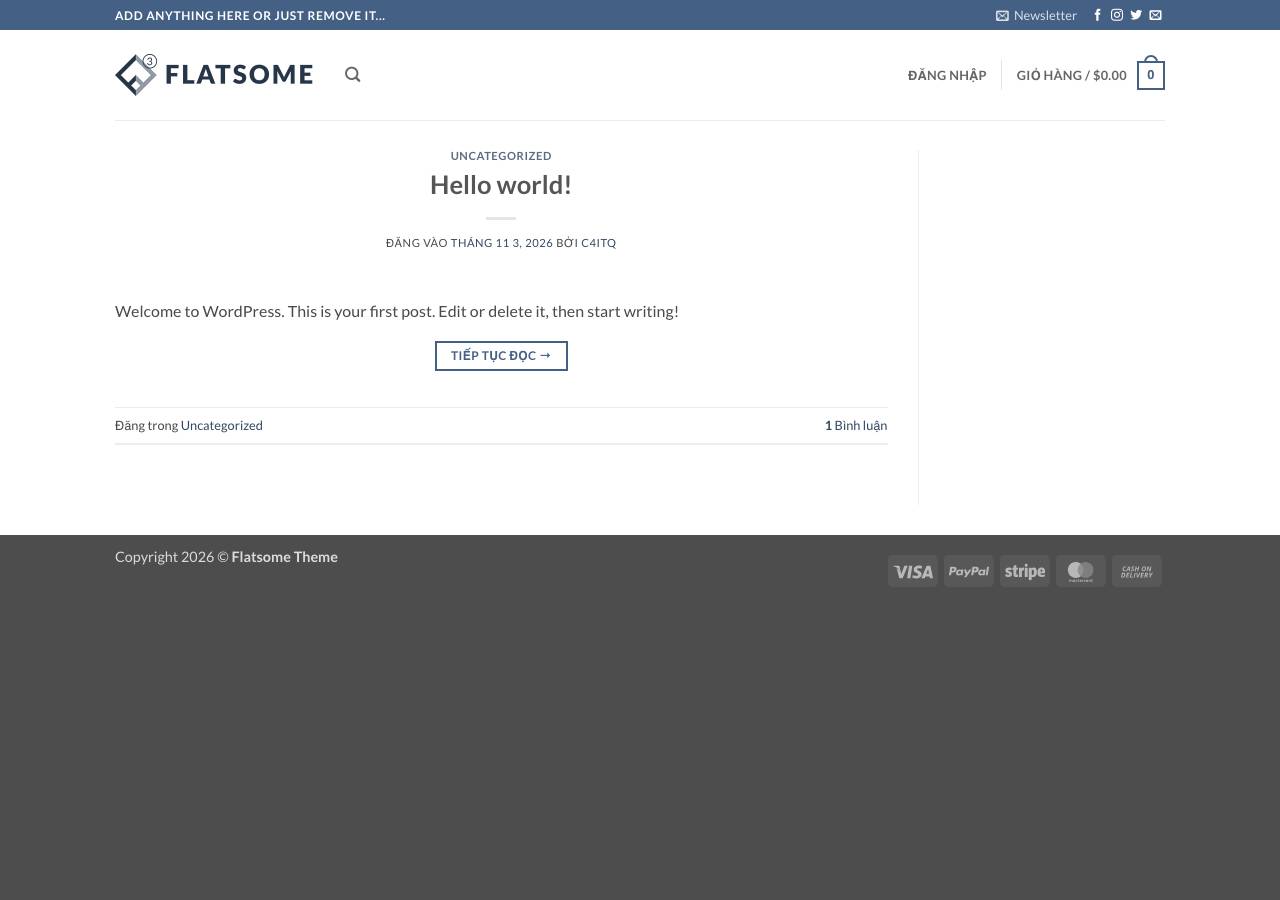
This is a fresh Vietnamese WordPress install with the default Flatsome/WooCommerce theme: a 'Hello world!' post and the stock WooCommerce account login that posts to itself. The PayPal hit comes only from the footer payment-method icons, and the name 'tiempijama' (pajama shop) is generic, so no brand is being impersonated.
The page displays PayPal and other payment logos (Visa, Stripe, MasterCard) in the footer, creating false association with legitimate payment processors. A login form with username/email and password fields posts to self (sealed-room phishing pattern), designed to harvest credentials from users who believe they are logging into a PayPal or payment-enabled account. The domain name 'tiempijama.fun' does not correspond to PayPal or any legitimate payment service, and the generic WordPress template
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, November 4, 2026
Same data as JSON: /api/zone/domain/tiempijama.fun. This page is not indexed by search engines and does not link to the site it describes.