vaco-portal.com
Appeared in the .com zone on Wednesday, November 4, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
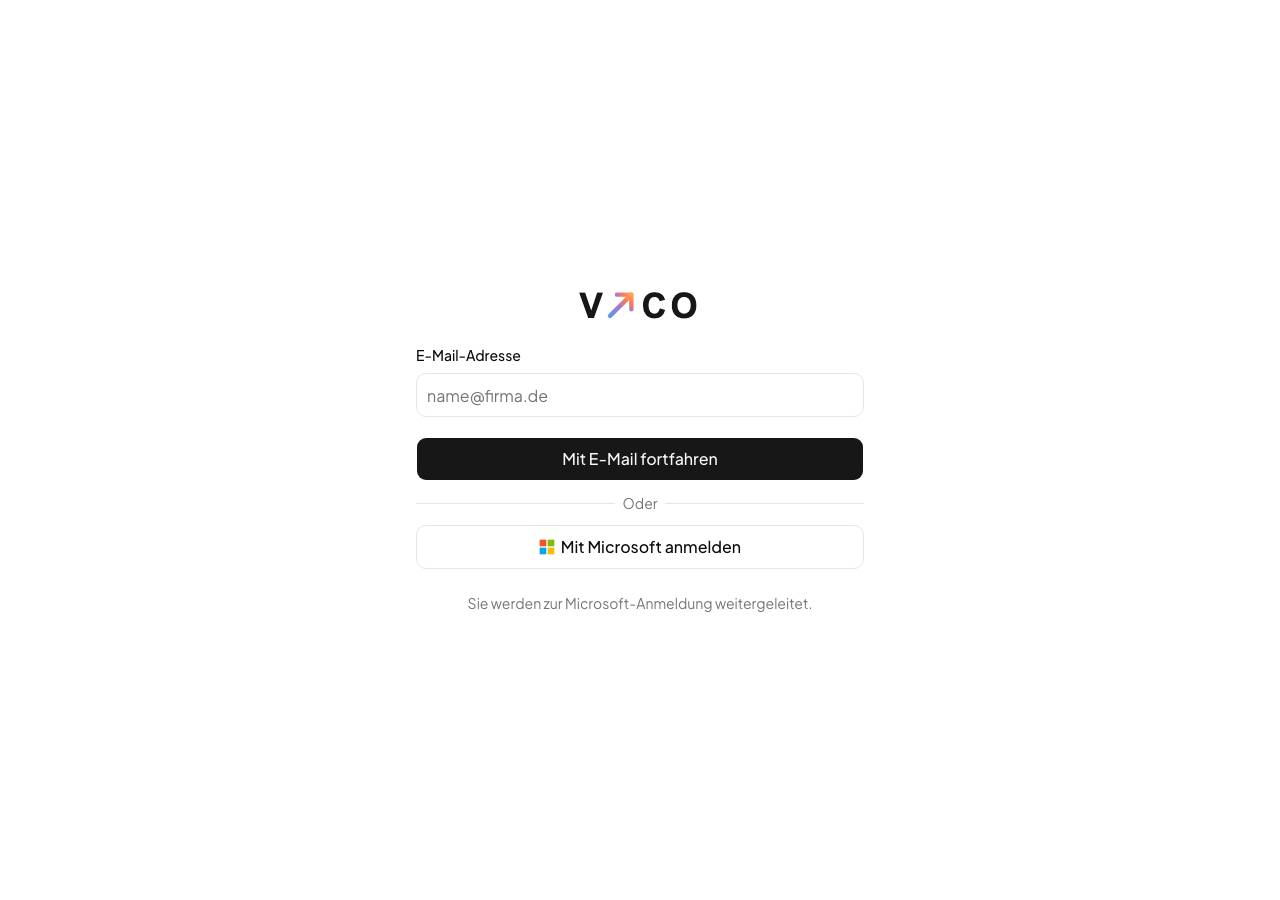
The page is a German vacation-carry-over ('Urlaubsübertrag') app under its own 'vaco' logo, matching the domain name. It asks only for an email (no password field) and offers a standard 'Mit Microsoft anmelden' OAuth button; its Next.js server-action forms and Azure DNS fit a small SaaS, not Microsoft impersonation.
The page impersonates a Microsoft login portal with a 'Mit Microsoft anmelden' (Sign in with Microsoft) button and claims users will be redirected to Microsoft authentication, but the forms post to itself (vaco-portal.com) with hidden action IDs, capturing credentials before any redirect. The domain name 'vaco-portal' combined with Microsoft branding in the page title and the sealed-room form architecture (no offsite links, self-posting forms) is a classic credential-theft phish.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Wednesday, November 4, 2026
Same data as JSON: /api/zone/domain/vaco-portal.com. This page is not indexed by search engines and does not link to the site it describes.