whatsappai-demo11.win
Appeared in the .win zone on Monday, September 14, 2026; by the end of that day the census found active website. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
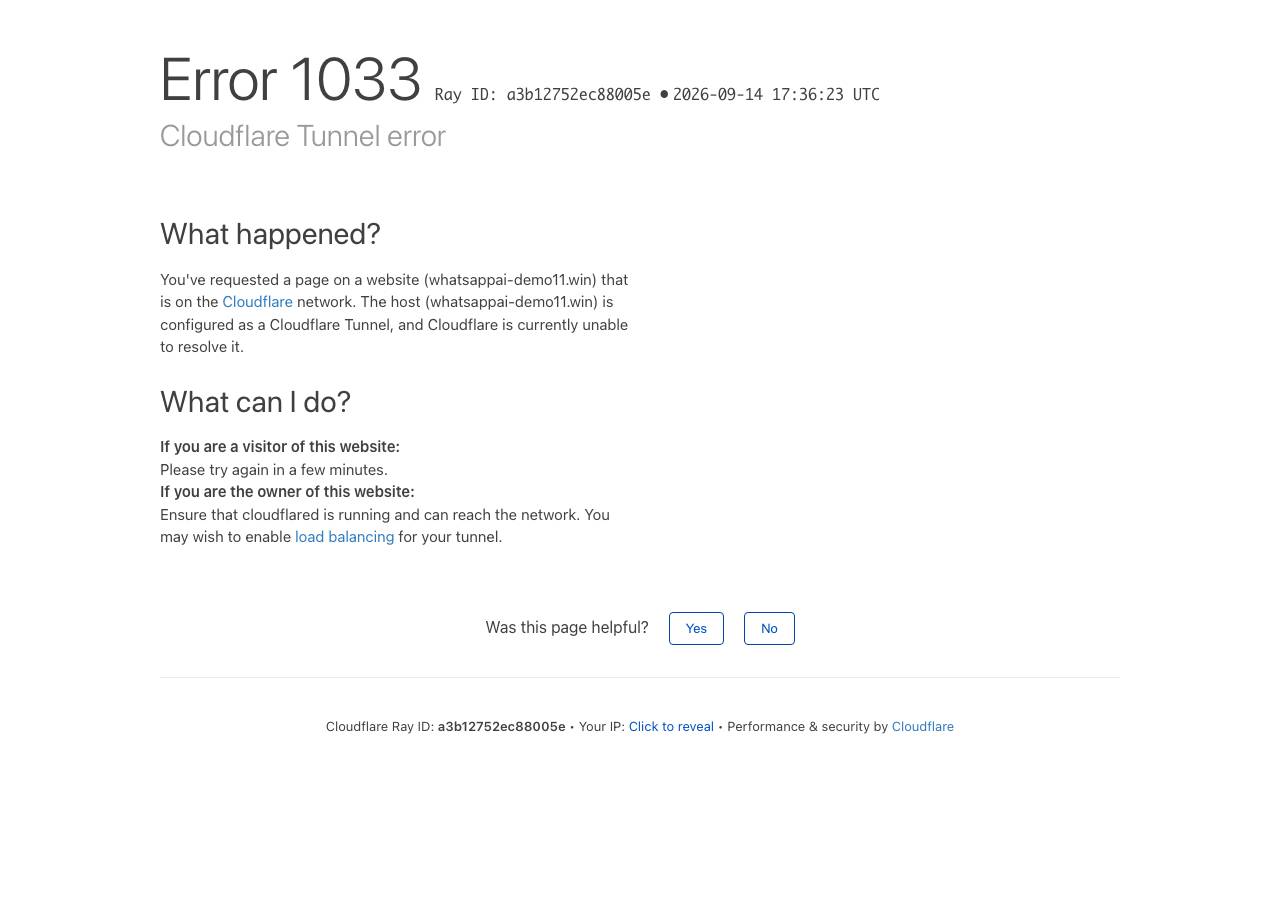
Not a victim-facing phish: the captured page is a Chinese-language operator console ("客户运营后台" – customer operations backend) asking for a 后台账号, and today it only returns a Cloudflare Tunnel 1033 error, so no WhatsApp branding is shown to deceive visitors. However, the name unauthorisedly uses the WhatsApp brand in a numbered demo series (whatsappai-demo11) on a .win domain fronted by a Cloudflare tunnel, the classic shape of grey-market WhatsApp AI bulk-messaging/marketing panels used to run fra
Domain impersonates WhatsApp with 'whatsappai-demo11.win' and resolves to a login page (登录 · 客户运营后台: 'Customer Operations Backend Login') with username/password form in Chinese, suggesting credential harvesting infrastructure. However, the page currently displays a Cloudflare Tunnel error (1033), so the phishing form is not fully operational—the intent is clear but the attack is incomplete or misconfigured.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, September 14, 2026
Same data as JSON: /api/zone/domain/whatsappai-demo11.win. This page is not indexed by search engines and does not link to the site it describes.