workspacegoog1e.icu
Appeared in the .icu zone on Thursday, October 15, 2026; by the end of that day the census found redirects elsewhere. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
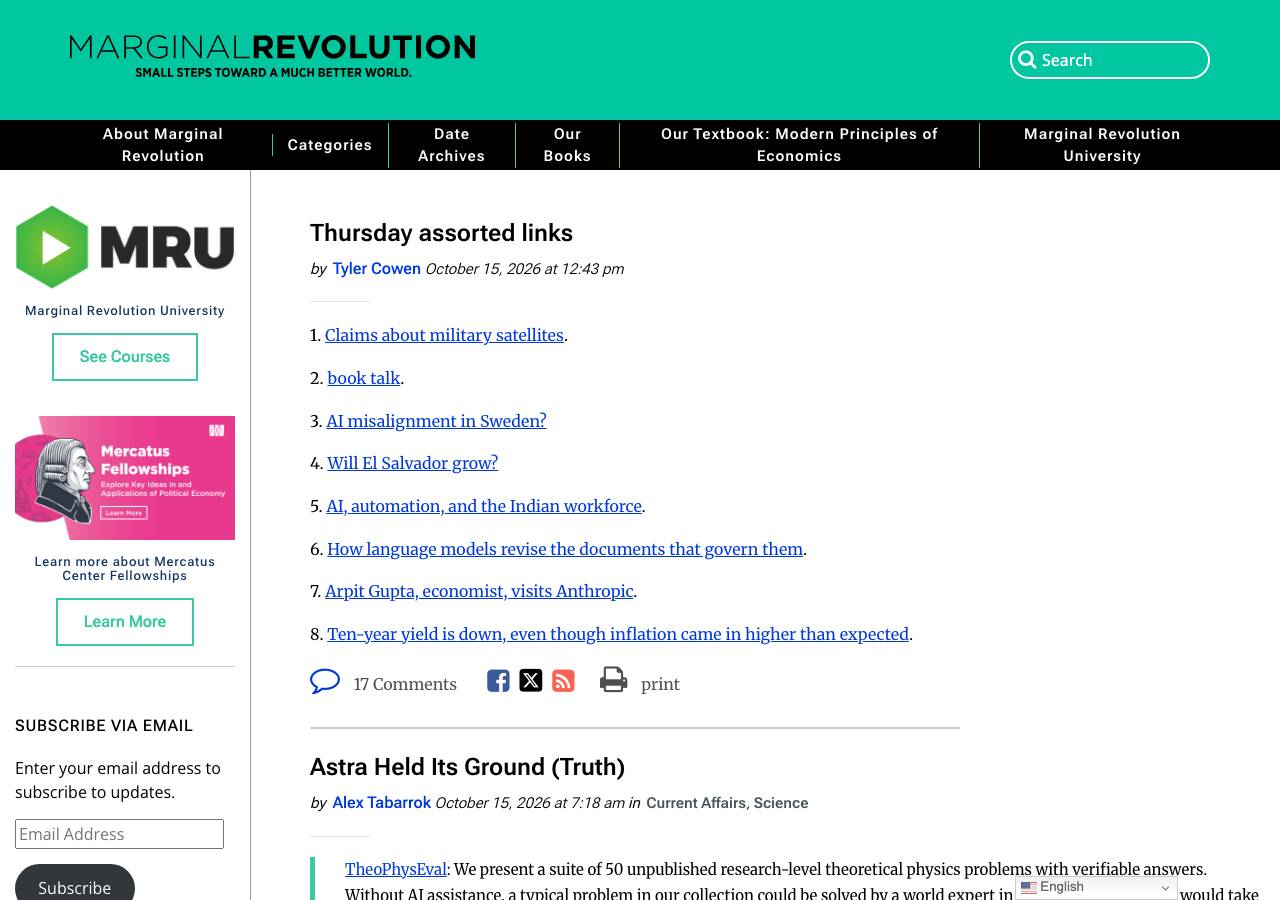
The name 'workspacegoog1e' is a leet-spelled Google Workspace typosquat on a cheap .icu TLD behind Cloudflare. It serves no content of its own and redirects to the unrelated marginalrevolution.com, whose only form is a newsletter signup, so this is a brand-squat (possibly cloaking for scanners) rather than an active phish.
The domain workspacegoog1e.icu uses leet-speak to impersonate Google (goog1e = google) combined with 'workspace' (a Google product), and redirects to an unrelated site (marginalrevolution.com). The domain name itself is crafted deception; the redirect to a legitimate economics blog is a misdirection tactic. The post-to-self email form on the destination page, combined with the typosquat domain infrastructure, indicates a sealed-room phishing setup designed to harvest credentials or data.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Thursday, October 15, 2026
Same data as JSON: /api/zone/domain/workspacegoog1e.icu. This page is not indexed by search engines and does not link to the site it describes.