xn--88-573g.top
Appeared in the .top zone on Monday, October 26, 2026; by the end of that day the census found active website about crypto web3. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
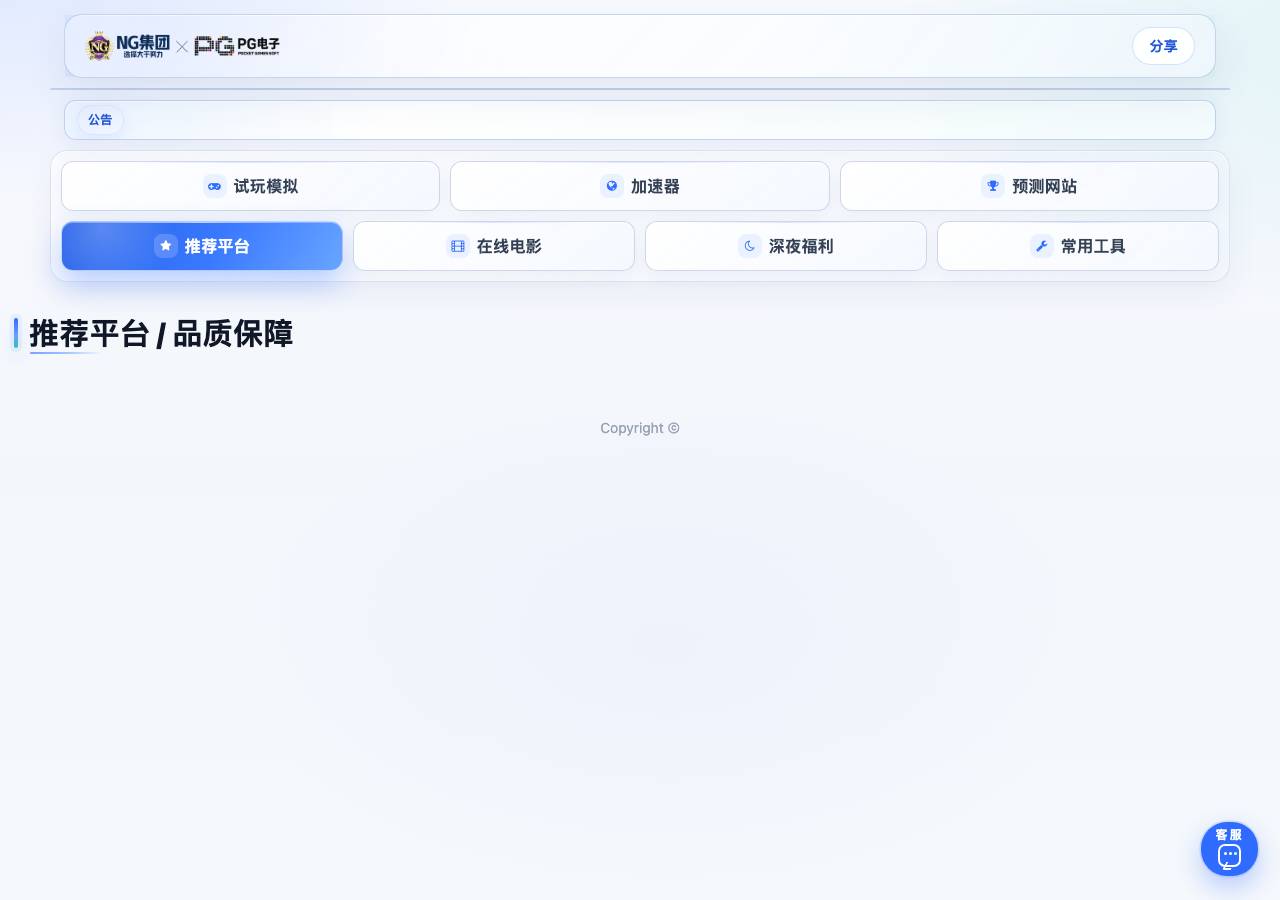
The punycode name 送88 ('send 88', a bonus-style lure) carries an NG集团 × PG电子 (PG Soft slots) branded link hub with demo-play, prediction-site, 'recommended platform' and late-night adult tabs plus Telegram/QQ customer-service popups, which marks it as an unlicensed-gambling front. The MetaMask, Trust Wallet, Binance and OKX entries are 'official download' links in a tool list rather than a page posing as those brands, though they could lead to trojanised wallet apps.
The domain uses a punycode-obfuscated name (送88, CJK script) and hosts a link aggregator directing users to download cryptocurrency wallets, VPNs, and gambling/prediction tools. While it references MetaMask and other legitimate brands in link form, this is a deceptive distribution portal designed to redirect users to potentially unsafe third-party sources—a classic abuse/squat pattern. The obfuscated domain name, generic casino/gambling/tool language, and aggregation of download links to sensiti
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Monday, October 26, 2026
Same data as JSON: /api/zone/domain/xn--88-573g.top. This page is not indexed by search engines and does not link to the site it describes.