zmexesje.shop
Appeared in the .shop zone on Saturday, October 31, 2026; by the end of that day the census found active website about e-commerce & retail. Full domain report
Signals, not verdicts. A domain appears here because heuristics matched its name, its infrastructure or the page it served on its first day. Where a model has looked at it, that is shown as an opinion with a confidence, not as a finding. Nothing on this page says a site is malicious. Read the evidence and decide for yourself.
Own one of these names and think the listing is wrong? Tell us and a person will look.
What matched
Model opinions
This is not PayPal phishing: PayPal appears only as the checkout method, and the forms are add-to-cart posts, not credential capture. It is a throwaway gibberish .shop name on a generic storefront template with just four products labelled 'Amazon/Wish/Mercari/Poshmark find' and boilerplate free-shipping and returns claims, which matches the fake-shop or PayPal-merchant triangulation campaign pattern.
The page prominently advertises 'Secure PayPal Checkout' and mentions PayPal multiple times, but the domain zmexesje.shop has no connection to PayPal. The site contains hidden form fields (action, slug, cart_token) posting to itself with no offsite payment processor links—a sealed-room phishing pattern designed to capture payment or account data before fraudulent submission to PayPal or interception by the attacker.
A model looked at the screenshot and page text and wrote what it thought. It can be wrong, and it is not a finding.
What the page looked like on Saturday, October 31, 2026
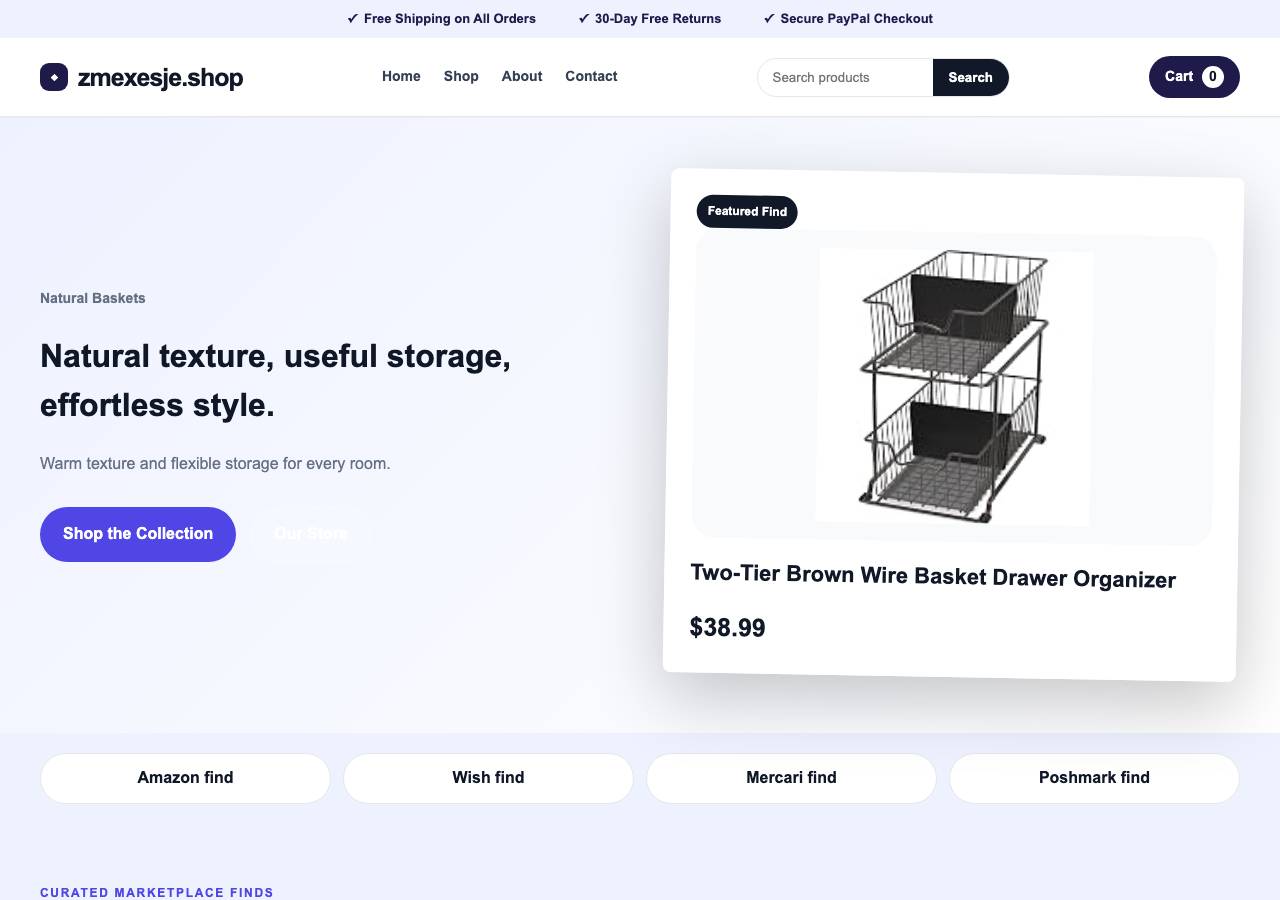
Same data as JSON: /api/zone/domain/zmexesje.shop. This page is not indexed by search engines and does not link to the site it describes.